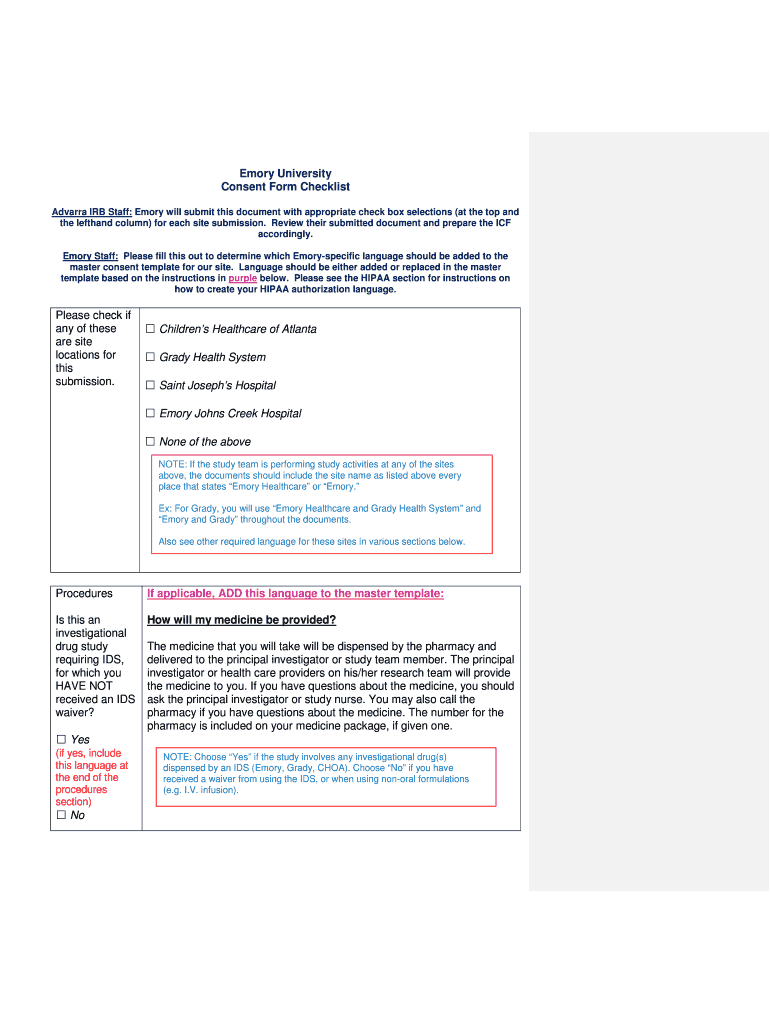
Emory University Consent Form Checklist Please Emory Irb
Use a Emory University Consent Form Checklist Please Emory IRB 0 template to make your document workflow more streamlined.
What the Emory consent checklist does
The Emory University Consent Form Checklist Please Emory Irb is an institutional control document used to verify that a consent package contains the required approvals, disclosures, signatures, dates, and version information. It is not a substitute for Emory IRB approval or the approved consent form. With signNow, a coordinator can upload the checklist, review detected fields, assign recipients, send it for electronic signatures, and retain the completed PDF with an audit trail. The institution must confirm the checklist’s current requirements, authorized signers, and retention policy before use.
Who uses the Emory consent checklist
Emory research teams
Emory research coordinators use the checklist to verify that an approved consent package contains the required fields, signatures, dates, investigator acknowledgments, and version references before the record enters the study file. signNow supports field assignment, routing, and audit-trail export without determining whether Emory has approved the underlying study materials.
IRB compliance reviewers
Institutional compliance reviewers and study administrators use the completed checklist as an evidence index for consent-package quality control. They can compare the signed checklist with the approved Emory version, inspect the audit trail, and restrict access to participant information according to the study’s privacy and retention requirements.
Key features for Emory checklist workflows
signNow combines field preparation, recipient routing, electronic signatures, audit evidence, and controlled storage for the Emory University Consent Form Checklist Please Emory Irb.
Field detection
Upload the Emory checklist and review automatically detected fields before adding missing signature, date, initials, or approval assignments. This reduces manual field placement while keeping the coordinator responsible for checking the approved institutional version.
Role routing
Assign each checklist field to a named recipient and establish routing order. Coordinators can separate participant, investigator, and reviewer actions so every person signs only the sections intended for them.
Audit trail
Capture signer actions, timestamps, delivery events, and document history in one audit trail. Export the evidence with the completed checklist so reviewers can evaluate the signing sequence and final record together.
Reusable templates
Use templates for a recurring Emory checklist only after the current approved version has been confirmed. Templates can preserve field placement and routing while reducing repeated preparation work for study teams.
Mobile signing
Complete assigned checklist fields from signNow mobile apps when study operations require mobile access. The responsible coordinator should still verify connectivity, recipient identity, and institutional handling requirements before finalizing the record.
Controlled storage
Connect signNow with approved systems such as Google Drive, Box, or Microsoft 365 when institutional controls permit. Centralized storage can keep signed checklists and audit exports associated with the study record.
How the Emory consent checklist works
The workflow converts the Emory University Consent Form Checklist Please Emory Irb into a controlled document sequence from preparation through archival.
Upload form: Upload the Emory checklist PDF Check fields: Review detected fields and add missing consent, date, or signature fields. Assign roles: Assign each field to the responsible Emory reviewer or signer. Store evidence: Send, complete, and retain the signed checklist with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete the Emory checklist
Use the approved Emory version, assign every required field, and preserve the signed document with its audit evidence.
Upload checklist:
Upload the approved Emory checklist PDF to signNow. Review fields:
Review auto-detected fields and add missing assignments. Route document:
Add authorized recipients and define signing order. Archive record:
Complete signatures and download the audit trail.
Recommended checklist workflow setup
Configure authentication, signature evidence, audit history, retention, encryption, and role-based user provisioning before sending an Emory checklist.
| Setting | Recommendation |
|---|---|
| Authentication method | Verified email with SMS code |
| Signature type | Electronic signature with signer intent |
| Audit trail | Exported with completed checklist |
| Document retention | Emory IRB policy and study schedule |
| Encryption | TLS 1.2/1.3 and AES-256 storage |
What the signNow audit trail records
The audit trail documents who interacted with the Emory checklist, when actions occurred, and how the completed record can be reviewed later.
Authenticate signer:
Capture timestamps:
Record document history:
Seal evidence:
Export records:
Retrieve later:
Record-keeping practices for consent checklists
Keep the completed checklist, approved version, signer evidence, and audit history together under Emory’s applicable research-record policy.
Export audit evidence with each completed checklist
Confirm retention rules before deleting records
Archive signed records in restricted storage
Index records against the approved version
Risks of incomplete consent records
Research coordinators
Clinical operations
Missing approval record
Attribution dispute
Version-control failure
Privacy incident
Privacy pitfalls in consent checklist workflows
Participant names, medical details, or study identifiers may remain visible to recipients who do not need access to the completed consent checklist. A consent checkbox or signature field assigned to the wrong person can leave participant authorization unproven in the final record. Shared links forwarded outside the approved study team can expose consent materials without the intended access controls or recipient verification. Saving completed checklists in personal email or local downloads can create uncontrolled copies of sensitive research information.
Security controls for signed checklists
TLS protection:
AES-256 at rest:
HIPAA with BAA:
SOC 2 Type II:
ISO 27001 certified:
ESIGN and UETA:
Troubleshooting the Emory consent checklist
Resolve field, routing, disclosure, audit-trail, plan, and privacy questions before treating a completed Emory checklist as final evidence.
Upload the official Emory checklist PDF rather than a screenshot or flattened image. In signNow Business, review the detected fields after upload and manually add any missing signature, date, initials, or approval fields before sending.
Use signNow’s recipient routing to assign each field to the correct coordinator, investigator, reviewer, or participant. A field assigned to the wrong recipient can undermine attribution even when the document itself is complete.
For participant-facing workflows, confirm electronic-consent disclosure requirements under 15 U.S.C. §7001(c), including paper-record rights and electronic-access capability. signNow can capture the signing event, but the institution must provide the required disclosure process.
signNow records timestamps, delivery events, signer actions, and document history in an audit trail. Export that evidence with the completed checklist and retain it under the applicable Emory research-record policy.
signNow Business includes audit trails, templates, and mobile apps at $8 per user per month when billed annually. Business Premium adds bulk send at $15 per user per month annually; choose it only if repeated checklist routing requires bulk distribution.
signNow is HIPAA compliant when a business associate agreement is required, and it uses TLS 1.2/1.3 in transit and AES-256 at rest. Confirm whether the Emory workflow contains protected health information and complete institutional review before deployment.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.