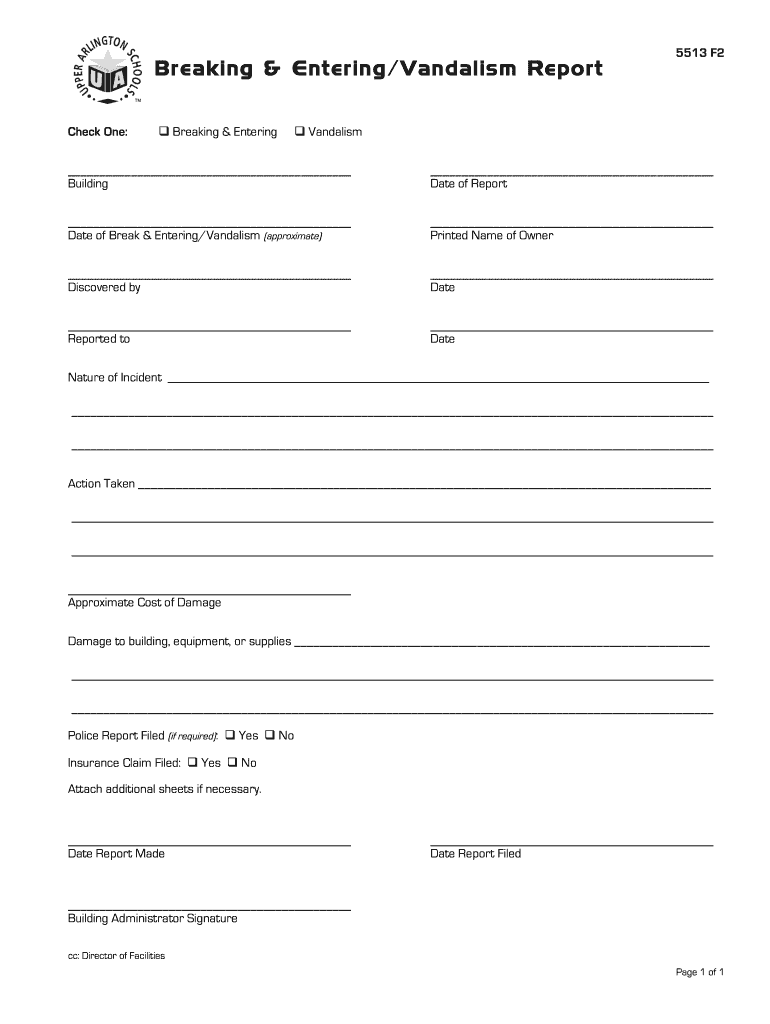
Breaking & Enteringvandalism Report Neola Form
Use a Breaking & EnteringVandalism Report Neola 0 template to make your document workflow more streamlined.
What the Neola vandalism report records
The Breaking & Enteringvandalism Report Neola Form is an incident record for documenting suspected unauthorized entry, property damage, or vandalism at a location. A preparer records the event details, observations, affected property, and supporting information, then routes the report to authorized reviewers or signers. With signNow, the form can be uploaded, its fillable fields reviewed, and signature requests sent by email or link. The completed report can be downloaded with an audit trail, helping an organization preserve who signed, when, and which document was completed.
Who uses the Neola vandalism report
Property management
Property managers, landlords, and facility teams can complete the report with incident dates, locations, damage descriptions, witness details, and supporting observations. signNow lets an authorized preparer route the document for review and signature, while the audit trail records signing activity for internal investigation, insurance coordination, or communication with the property owner.
Security and investigations
Security teams, business owners, and investigators can use the report to document unauthorized entry or vandalism before preserving related evidence. A controlled signNow workflow helps identify who prepared and signed the report, limits distribution, and stores the completed PDF with its audit trail for later organizational review.
How to complete the Neola report
Complete the incident details first, then route the report to authorized reviewers through signNow.
Upload the report:
Upload the completed incident report and let signNow detect its fillable fields. Check the fields:
Review each detected field and correct labels, dates, and narrative details. Assign reviewers:
Assign the report to the investigator, property owner, or authorized reviewer. Send for signature:
Send the report for signature when the incident details are complete. Store the record:
Download the signed report and audit trail for secure case records.
Recommended report workflow setup
Configure the Neola report around signer attribution, review evidence, secure transmission, and the organization’s incident-record policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable downloadable audit trail |
| Document retention | Follow state incident policy |
| Encryption | TLS 1.2 or 1.3 in transit |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the signNow audit trail captures
The audit trail preserves the signing evidence needed to review who handled the Neola report and when each action occurred.
Authenticate signer:
Capture timestamp:
Record document history:
Seal the report:
Export evidence:
Archive securely:
Best practices for completing the report
Accurate incident details, controlled access, and complete records make this report easier to review after a property event.
Verify incident details before sending
Assign authorized reviewers
Separate facts from conclusions
Preserve the signed record
Platform requirements for the Neola report
Open the Breaking & Enteringvandalism Report Neola Form in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow protects data in transit with TLS 1.2 or TLS 1.3 and provides mobile apps for iOS and Android, allowing authorized users to review and sign the report from supported devices.
Browser support Chrome, Firefox, Safari, and Edge on Windows or macOS Mobile apps signNow mobile apps for iOS and Android devices Connection security TLS 1.2 or TLS 1.3 for transmitted data
Organizations using managed Windows, macOS, iOS, or Android devices should permit signNow access, maintain current browser security updates, and control downloaded incident reports through device-management policies. Teams requiring API access, SSO provisioning, or regulated retention should confirm the selected signNow plan and configure certificates, permissions, and archival procedures before deployment.
Security for signed incident reports
Data in transit:
Stored report data:
Security assurance:
Information security:
Electronic signatures:
Controlled access:
Privacy challenges in incident reporting
Including unnecessary tenant, employee, or witness information can expose personal data when the signed report is shared outside the investigation team. Sending the report before confirming signer identity can weaken attribution when property ownership or authorization is later questioned. Granting broad folder access can expose photographs, damage descriptions, and contact details to users unrelated to the incident. Failing to export the audit trail can leave the organization without a complete record of timestamps, signing actions, and document history.
Legal value of the signed report
A completed Breaking & Enteringvandalism Report Neola Form can preserve a dated account of observed damage and review activity. Under ESIGN, 15 U.S.C. chapter 96, and applicable state electronic-transactions law, an electronic signature may support a business record when intent, attribution, consent, and reliable retention are shown. Wills, court orders, and certain family-law records remain excluded.

State rules and document exclusions
State notarization
Wills and codicils
Family-law records
Real-estate deeds
Troubleshooting the Neola report workflow
These answers address signing, privacy, plan, and record-handling questions for a Breaking & Enteringvandalism Report Neola Form workflow.
signNow Business includes templates and audit trails, but bulk sending is listed for Business Premium. For repeated vandalism reports, create a reusable template on Business, or use Business Premium when sending many individualized reports. Confirm current plan limits before assigning a large reporting workflow.
The Business plan includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, SOC 2, and GDPR support. HIPAA workflows require a business associate agreement, and regulated records should be configured with the controls required by the applicable organization and law.
A signer can usually open a signing request from the email link without creating an account. If stronger attribution is required, configure available authentication controls, such as two-factor authentication or SMS verification, and retain the completed audit trail with the report.
signNow records signing timestamps, document history, and audit-trail information for the report. Download the completed PDF and certificate of completion, then preserve them together under the organization’s incident-record policy to support later review or dispute resolution.
The report should contain only information needed to document the breaking-and-entering or vandalism event. Limit access through assigned roles, avoid unnecessary personal details, and apply the organization’s privacy policy before sharing the signed file with insurers, owners, or law enforcement.
The Business plan is listed at $8 per user per month when billed annually, with a seven-day free trial and no credit card required. Month-to-month pricing is higher, and paid plans include 100 signature invites per user annually before overage fees may apply.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.