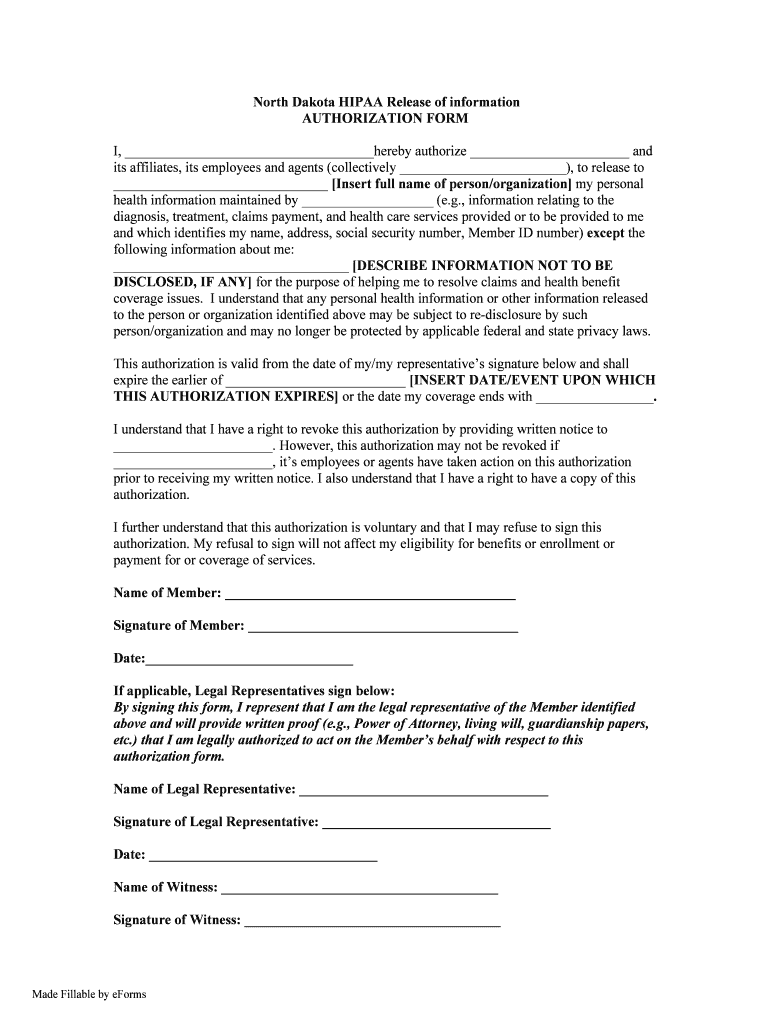
North Dakota HIPAA Release Of Information
Use a North Dakota HIPAA Release Of Information 0 template to make your document workflow more streamlined.
What this North Dakota authorization does
A North Dakota HIPAA Release Of Information authorizes a healthcare provider or covered entity to disclose specified protected health information to a named recipient. The signer identifies the information, purpose, recipient, and expiration or revocation terms required by the authorization. The provider should use its approved form and verify that the release meets HIPAA Privacy Rule requirements before disclosure. signNow can upload the document, detect fillable fields, route it for signatures, and preserve the completed authorization with an audit trail. HIPAA documentation must be retained for six years under 45 CFR §164.530(j).
Who uses this authorization
Healthcare practices
Healthcare practices use North Dakota release authorizations to document a patient’s permission to disclose specified protected health information to a named recipient. Common document categories include medical-record requests, treatment information, billing records, and attorney or insurer requests, subject to the provider’s approved HIPAA form and disclosure policy.
Hospitals and health systems
Hospitals and health systems can route authorizations among patients, representatives, records teams, and approved recipients. Templates should identify the information requested, purpose, expiration, and revocation method, while role-based access and audit evidence help support controlled disclosure decisions.
Who benefits from digital releases
North Dakota healthcare practices, hospitals, and health systems can use structured release workflows when their privacy and records policies permit electronic signatures.
A North Dakota medical practice can collect patient authorizations for records disclosure, route them to named recipients, and preserve signed copies with audit evidence for its HIPAA records process. A regional hospital can standardize release templates across departments, assign access by role, and use controlled workflows when patients authorize disclosure to attorneys, insurers, or other providers. A healthcare enterprise can connect signNow with existing systems, delegate sending, and manage authorization records centrally while requiring a HIPAA business associate agreement and documented privacy controls.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for North Dakota releases
signNow organizes the North Dakota authorization workflow around field accuracy, signer identity, audit evidence, PHI protection, and controlled retention.
Field detection
Upload the North Dakota release and identify its signature, initials, date, recipient, and authorization fields before sending.
Signer routing
Route the authorization to the patient or authorized representative using defined signing order and recipient details.
Signer identity
Use email links or SMS-based authentication to connect the completed release with the intended signer.
Audit evidence
Capture timestamps, signer actions, delivery events, and completion evidence for later records review.
Data protection
Protect PHI in transit with TLS 1.2/1.3 and at rest with AES-256 within signNow’s compliant infrastructure.
Controlled retention
Retain the release and audit evidence under the provider’s HIPAA records policy and six-year documentation rule.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended release workflow settings
Configure the North Dakota authorization around signer identity, protected health information, auditability, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail and retention | Detailed audit trail; six years under 45 CFR §164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
| User provisioning | Role-based access with managed users |



How the authorization audit trail works
The audit trail records identity, timing, document integrity, and retrieval events surrounding each North Dakota release authorization.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Record actions:
Export trail:
Security for protected health information
Encryption:
HIPAA safeguards:
SOC 2 certification:
ISO certification:
Signer authentication:
Audit evidence:
Record-keeping practices for releases
Retain the signed authorization and supporting evidence in a controlled record system that matches HIPAA documentation obligations.
Apply the six-year HIPAA documentation period
Export the completed authorization record
Archive records with restricted access
Check scope before disclosure
Rollout and retention timeline
Use this sequence to move a North Dakota release from field preparation through signing, disclosure review, and documented retention.
Prepare authorization:
Send for signature:
Complete signing:
Retain record:
Start disclosure review:
Manage revocation:
Review access:
Use seven-day trial:
Privacy pitfalls to avoid
A release that omits the recipient, purpose, information scope, expiration, or revocation method may not support the intended disclosure decision. Sending a completed authorization to the wrong email address can expose protected health information and requires documented incident handling. Using a shared account instead of assigned users weakens access control and makes responsibility for patient authorization activity harder to establish. A signed form does not authorize disclosure beyond its stated scope; records staff must compare the request with the patient’s permission.
Risks from incomplete releases
Missing authorization
Unclear recipient
Overbroad disclosure
Incomplete audit trail
Troubleshooting North Dakota releases
Resolve signer, privacy, and plan questions before disclosing protected health information through a completed authorization.
Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, and SOC 2. HIPAA workflows require signNow’s HIPAA-compliant configuration and a business associate agreement, rather than relying on the plan name alone.
HIPAA compliance is listed by signNow as requiring a BAA. Confirm the BAA, permitted data handling, user access controls, and organization-specific configuration before placing protected health information in a North Dakota release workflow.
Upload the North Dakota authorization, use signNow’s field detection, confirm the patient, recipient, scope, purpose, and expiration fields, then send it for signature. Download or store the completed document with its audit trail after signing.
Electronic signatures may satisfy ESIGN and North Dakota’s UETA framework when intent, consent, attribution, and record retention requirements are met. HIPAA still governs the authorization’s content and disclosure process, so legal validity does not replace privacy review.
Business Premium adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication. Business provides audit trails and templates, but the selected plan must match the organization’s authentication, volume, and deployment requirements.
If a patient cannot access the email link, verify the address, resend the invitation, or use an approved authentication method such as SMS OTP. Do not substitute another signer without confirming authority and documenting the change.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.