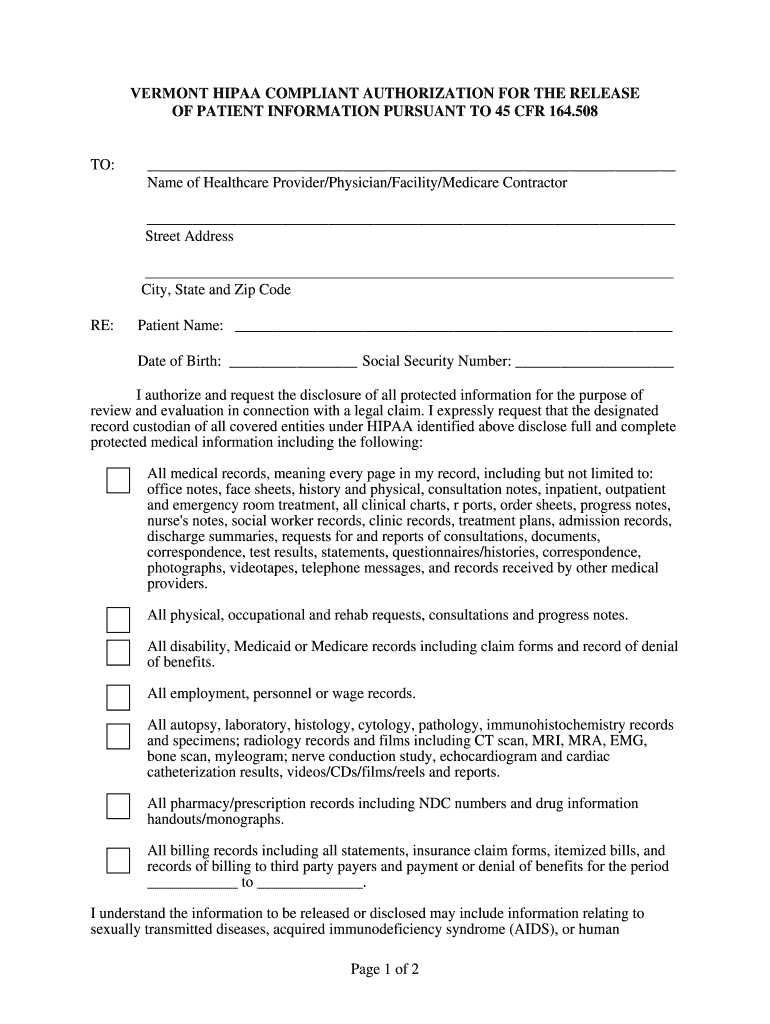
Authorization To Use Or Disclose Patient Information Effective
Use a Authorization To Use Or Disclose Patient Information Effective 0 template to make your document workflow more streamlined.
What this patient authorization does
An Authorization To Use Or Disclose Patient Information Effective records a patient’s permission for a covered entity to use or disclose specified health information to a named recipient for a stated purpose. The form should identify the patient, information categories, recipient, purpose, expiration or revocation terms, and required signatures. Staff should confirm the wording against HIPAA and applicable state privacy law before releasing records. signNow can upload the document, detect fields, route it to signers, capture an audit trail, and preserve the completed authorization.
Who uses this authorization form
Healthcare providers
Healthcare providers and medical practices use this authorization to document a patient’s permission to disclose specified health information to a named person, organization, or professional for a stated purpose.
Patients and representatives
Patients and authorized representatives review the disclosure scope, recipient, purpose, expiration terms, and signature fields before returning the completed form to the covered entity.
Features for patient authorizations
signNow provides document preparation, signer verification, audit evidence, and controlled storage features that map directly to patient-information authorization workflows.
Field detection
Upload this authorization and review auto-detected fields before adding the patient and recipient roles, reducing manual placement errors in repeated healthcare workflows.
Remote signing
Send the authorization to a patient or representative by email, allowing remote review and signature without requiring an office appointment.
Signer controls
Apply SMS verification or another configured signer-control method when organizational policy requires stronger evidence linking the patient to the completed authorization.
Audit trail
Capture timestamps, signer actions, and document history in an audit trail that can accompany the completed authorization during internal review.
Reusable templates
Use templates for approved authorization language while preserving fields for patient identity, disclosure scope, recipient, purpose, and expiration.
Protected records
Store the signed authorization and completion evidence in a controlled workflow, supporting HIPAA documentation practices when the required BAA and configuration are in place.
How this authorization workflow works
The workflow keeps the patient, recipient, purpose, disclosure scope, and effective terms connected to one signed record.
Prepare: Upload the patient authorization. Review: Detect and verify its fields. Send: Route it to signers. Preserve: Store the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete this authorization in signNow
Follow these steps to prepare, sign, and preserve a patient-information authorization with signNow.
Upload:
Upload the authorization PDF. Check fields:
Review detected patient and disclosure fields. Add signers:
Add the patient and recipient signers. Send:
Send the authorization for completion. Archive:
Store the signed PDF and audit trail.
Review the signNow audit trail
The audit trail records technical evidence around this authorization’s signing event, helping staff verify who acted, when they acted, and which document was completed.
Authenticate signer:
Timestamp event:
Hash document:
Seal history:
Record activity:
Export trail:
Configure this authorization workflow
Use controlled authentication, documented consent, and protected retention for patient-information authorizations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export completed audit trail |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption and access | AES-256 storage with managed users |
Protect patient authorization records
HIPAA protection:
Transport encryption:
Stored encryption:
Control assurance:
Security management:
Signing evidence:
Address privacy and consent pitfalls
The form can expose protected health information when recipients or internal users receive copies beyond the authorization’s stated disclosure scope. A patient may sign without a clear electronic-records disclosure explaining access, paper-copy rights, or withdrawal procedures when ESIGN requires that notice. An incomplete expiration date or missing purpose can make staff question whether the requested disclosure remains within the patient’s authorization. Unrestricted templates or shared credentials can let unauthorized staff alter, send, or access a patient-information authorization.
Use disciplined authorization practices
A precise authorization and controlled recordkeeping process reduce disclosure disputes and protect the patient’s privacy interests.
Identify every disclosure element
Verify the patient signer
Archive the signed record
Check scope before disclosure
Retain authorization records by rule
For HIPAA-covered entities, preserve the authorization and related required documentation for the period specified by 45 CFR 164.530(j).
Six years: authorization records
Six years: privacy procedures
Six years: privacy notices
Six years: complaint records
Six years: training records
Check state rules before signing
Notarization rules
State variation
Wills excluded
Family law
Real-estate deeds
Troubleshoot patient authorization workflows
These answers address field detection, HIPAA configuration, signer identity, retention, and electronic-consent questions for this authorization form.
Upload the authorization as a PDF or supported document, then inspect every detected field. signNow can auto-detect fillable fields, but staff should verify patient, recipient, purpose, expiration, and signature locations before sending.
A healthcare workflow requiring HIPAA protections needs signNow’s HIPAA-compliant configuration and a business associate agreement. The ground-truth plan details identify HIPAA and 21 CFR Part 11 as Site License add-ons; confirm the selected plan and BAA before processing PHI.
The Business plan is listed at $8 per user per month with annual billing and includes legally binding eSignatures, audit trails, templates, and mobile apps. It includes 100 signature invites per user annually; overage terms should be reviewed before high-volume use.
Use signNow’s signer authentication options, including SMS-based verification where configured, and review the audit trail after completion. If identity proofing or stronger authentication is required by policy, confirm whether the selected plan supports that control before sending PHI.
A completed authorization should be stored with its audit trail and certificate of completion. HIPAA requires covered entities to retain required documentation for six years from creation or the last effective date under 45 CFR 164.530(j), whichever is later.
Consumer-facing electronic records may require an ESIGN disclosure explaining paper-record rights, electronic access, and withdrawal procedures under 15 U.S.C. §7001(c). Healthcare staff should apply that requirement when the patient is acting as a consumer and organizational policy requires it.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.