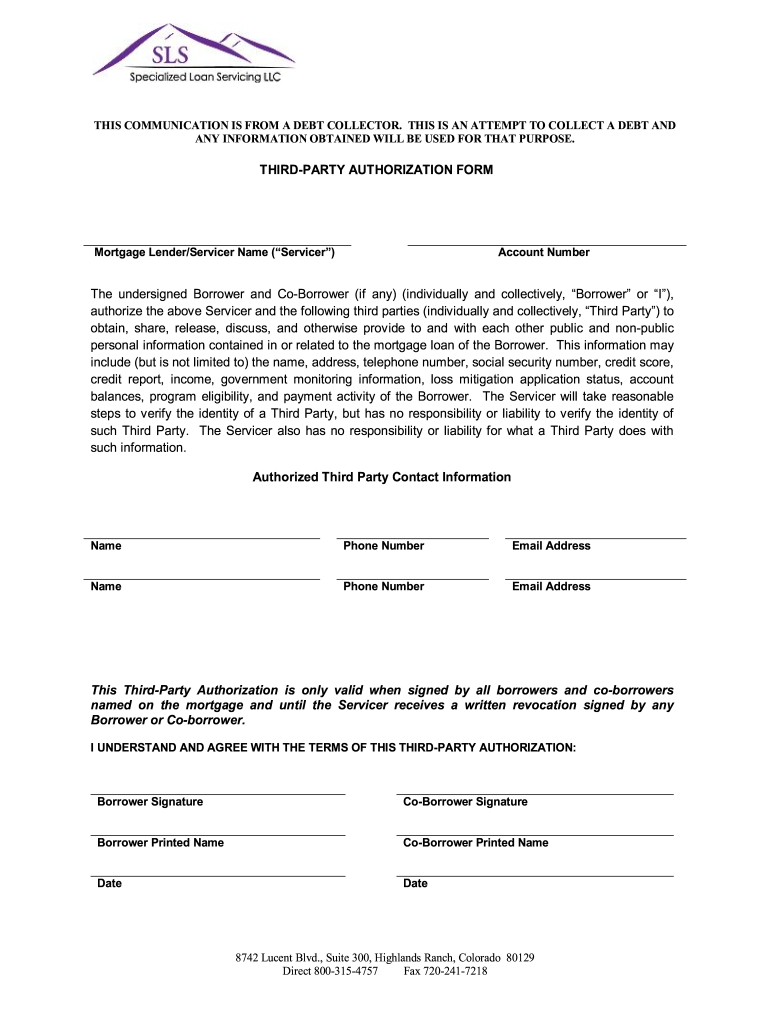
Sls Third Party Authorization Form
Use a Sls Third Party Authorization Form 0 template to make your document workflow more streamlined.
What a third-party authorization form does
A Sls Third Party Authorization Form lets one person or organization authorize another party to act, communicate, or access information on the authorizer’s behalf. The completed form identifies the authorizer, authorized representative, permitted purpose, scope, and signature details. In a U.S. business workflow, the document should state exactly what the third party may do and when that permission ends. signNow can convert an uploaded form into a fillable document, route it to the required signer, capture the signing event, and preserve the completed record with its audit trail.
Legal standing of the authorization
An electronically signed Sls Third Party Authorization Form can support a U.S. transaction when the signer shows intent, consents to electronic records, can be identified, and the record remains accessible and reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA or New York ESRA rules. Wills, court orders, and certain family-law documents remain excluded.

Who uses this authorization form
Business operations
Businesses use the form when a representative must communicate, approve, retrieve records, or complete a defined task for another party. The authorization should identify both parties and limit the permitted action.
Regulated teams
Healthcare, legal, financial, and property teams should match the authorization scope to applicable privacy, professional, and state-law requirements before sending it for signature.
Users, roles, and delegated sending
Administrators can maintain the Sls Third Party Authorization Form template, assign roles, control access, and review audit trails. Delegated senders can initiate requests without changing the approved language or recipient permissions, supporting consistent authorization handling across departments. Operations and compliance teams can use shared templates for recurring authorizations, while reviewing each document’s parties, purpose, scope, expiration, and privacy requirements before the form reaches the authorizer or representative.
How the authorization workflow works
The form moves from document preparation to controlled authorization, signature, and retained evidence.
Upload form: Upload the authorization template to signNow. Detect fields: Auto-detect fillable fields and review placement. Assign parties: Add the authorizer and representative as recipients. Complete record: Send, sign, and store the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete the authorization form
Use this sequence to prepare, route, sign, and retain the Sls Third Party Authorization Form in signNow.
Upload form:
Upload the Sls Third Party Authorization Form. Review fields:
Review automatically detected fillable fields. Assign recipients:
Assign the authorizer and representative roles. Send request:
Send the authorization for electronic signature. Store evidence:
Download the signed form and audit trail.
Recommended authorization form setup
Configure the form around signer identity, delegated authority, evidence, and the retention rule for the underlying transaction.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Follow the underlying record’s legal schedule |
| Encryption | TLS 1.2/1.3 in transit and AES-256 at rest |
Features that support authorization records
A well-configured Sls Third Party Authorization Form connects defined authority with signer identity, evidence, controlled delivery, and record retention.
Defined scope
Place the authorizer, representative, purpose, scope, and expiration fields directly on the Sls Third Party Authorization Form so reviewers can identify the permitted authority.
Clear signers
Assign each signature or acknowledgment field to the correct party, reducing uncertainty about who granted permission and who accepted the responsibility.
Audit evidence
Capture the completed form and signing history together, creating a more useful record for internal review or a later authorization dispute.
Reusable template
Use reusable field placement for recurring authorization requests while reviewing each instance for the correct parties, purpose, and expiration date.
Controlled delivery
Route the form to authorized recipients through email or a controlled signing link, helping keep delegated access limited to the intended workflow.
Organized storage
Store the signed authorization with access controls and retention rules that match the underlying business, healthcare, legal, or financial record.
What the audit trail records
The audit trail connects signer identity, document events, timestamps, and the final Sls Third Party Authorization Form.
Authenticate signer:
Capture timestamp:
Hash document:
Seal evidence:
Track activity:
Export history:
Signer authentication and certificates
PKI:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Document integrity:
Retention practices for authorization records
Retain the signed authorization, audit evidence, and related revocation history as one controlled record.
Match retention to the underlying record
Export the audit trail with the form
Secure the completed authorization
Monitor expiration and revocation
Privacy pitfalls in authorization workflows
Including unnecessary personal information can expose data beyond the authorization’s purpose and complicate privacy review, especially when the form is shared outside the organization. A vague permission statement may fail to show what the representative may access, approve, disclose, or communicate on the authorizer’s behalf. Sending the completed form to an unverified email address can disclose the authorizer’s personal or business information to the wrong recipient. Leaving former representatives active after revocation can permit continued access or create uncertainty about which authorization controls the transaction.
Documents requiring special handling
Notarization rules
Wills and codicils
Family law documents
Real-estate deeds
Troubleshooting authorization form workflows
These answers address signer routing, plan selection, electronic-signature evidence, privacy, notarization, and link security for this authorization workflow.
Check that every required field has an assigned recipient and that the authorizer’s email address is correct. signNow’s field assignment and recipient routing should identify missing ownership before sending. Reopen the document, correct the field roles, and send a new request if the original routing was wrong.
The signNow Business plan includes templates, audit trails, and legally binding eSignatures at $8 per user per month when billed annually. If the workflow needs bulk sending, Business Premium is listed at $15 per user per month annually and includes bulk send.
A typed or drawn signature can document intent, but the record must also identify the signer and preserve the completed document. signNow audit trails record signing events, timestamps, IP information, and actions, supporting evidence under ESIGN and applicable state electronic-transactions law.
HIPAA-covered use requires more than a signature workflow. signNow identifies HIPAA compliance with a business associate agreement requirement. Confirm that a BAA is in place, restrict access to protected health information, and apply the healthcare organization’s retention policy under 45 CFR §164.530(j).
If the authorization requires notarization, a regular electronic signature workflow does not replace the required acknowledgment. State rules control notarial form and recording requirements. Confirm the applicable state notary procedure before sending the document through signNow.
Use a signing link only when the organization can control distribution and identify the intended signer. For stronger attribution, add SMS OTP or another available authentication method, then preserve the audit trail with the signed Sls Third Party Authorization Form.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.