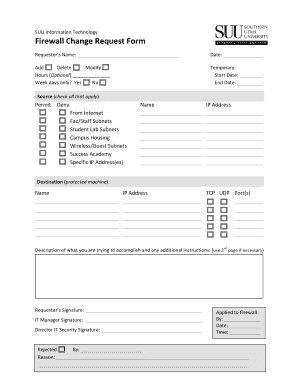
Firewall Change Request Form
Use a Firewall Change Request Form 0 template to make your document workflow more streamlined.
What the Firewall Change Request Form does
The Firewall Change Request Form records a proposed network-perimeter change and obtains documented approval before an administrator implements it. It identifies the affected firewall, environment, source and destination traffic, ports, protocols, requested action, business justification, implementation window, rollback plan, requester, and approver. In signNow, upload the form, map or auto-detect fillable fields, review the completed technical scope, send it to the authorized signer, and retain the signed document with its audit trail. No universal legal filing deadline or issuing agency is specified for this internal business-control document; apply your organization’s change-management policy and contracts.
Business types that benefit from firewall requests
The form gives technical teams and their customers a consistent approval record for firewall changes, from one-person consultancies to regulated enterprises.
Solo IT consultants use the Firewall Change Request Form to document client-approved rule changes, attach technical details, and obtain an auditable signature before modifying a customer’s network perimeter. Managed service providers use the form to coordinate firewall updates across customer environments, preserving approval evidence, implementation notes, and signer identity for later service reviews. Enterprise security teams use the form for controlled change governance, routing requests through infrastructure owners, compliance reviewers, and authorized approvers before production firewall updates.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this firewall change request
IT operations
Network administrators complete firewall change requests for rule additions, removals, address updates, service ports, and implementation windows. SignNow fields and audit trails preserve approval evidence for internal security reviews.
Service providers
Managed service providers use signed requests for customer authorization, infrastructure changes, and maintenance records. The completed document connects technical scope with the customer’s identified approver and requested timing.
Features for controlled firewall changes
A structured Firewall Change Request Form helps technical teams capture precise rule information, obtain authorization, and retain evidence without separating approval from implementation details.
Structured scope
Capture source and destination addresses, ports, protocols, environments, and requested rule actions in one structured request, reducing omissions that can delay security review or implementation.
Approval routing
Route the request to the correct infrastructure owner and approver, keeping technical authorization connected to the exact firewall change described in the document.
Auditable signatures
Collect electronic signatures with signer identity, timestamps, and action history recorded alongside the completed Firewall Change Request Form for later review.
Reusable templates
Use reusable templates for recurring firewall changes while retaining the fields that distinguish production, test, emergency, and customer-specific requests.
Centralized records
Keep approved requests and completion records together in signNow, creating a retrievable record of what changed, who approved it, and when.
Connected workflows
Connect requests to systems such as Microsoft 365, Google Drive, Box, or Procore when teams need documented storage or operational handoffs.
Complete a firewall change request
Prepare the request in signNow, verify its technical scope, and collect approval before the firewall administrator implements the documented change.
Add document:
Upload form Check fields:
Map fields Choose signer:
Route approval Collect signature:
Complete request Save record:
Store evidence
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended firewall request setup
Configure the Firewall Change Request Form to identify the signer, preserve approval evidence, and protect the completed request throughout its operational record lifecycle.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enable completion certificate and action history |
| Document retention | Follow organizational change-control policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
Platform requirements for signing requests
Use a current Chrome, Firefox, Safari, or Edge browser on Windows or macOS to upload, complete, and route the Firewall Change Request Form. signNow also provides iOS and Android mobile apps for reviewing and signing requests.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile apps iOS and Android signNow apps
Organizations should manage access through approved devices, role-based permissions, and documented administrator controls. Where the Firewall Change Request Form connects to operational systems, confirm API, SSO, storage, and retention requirements with the security team before deployment.



Security for firewall request records
Transport encryption:
Stored encryption:
Security certification:
Management standard:
Signature compliance:
Health data option:
How signNow records firewall approvals
The audit trail shows how the Firewall Change Request Form moved from signer verification through completion, preserving technical approval evidence separately from the form’s visible fields.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Build history:
Export evidence:
Challenges when documenting firewall changes
Incomplete source, destination, port, or protocol details can prevent reviewers from evaluating the requested firewall rule accurately. Missing business justification or rollback instructions can delay approval because reviewers cannot assess operational impact or recovery steps. An incorrect approver or signer email can leave the firewall request unauthorized even when the technical fields are complete. Separating the signed approval from implementation evidence makes it difficult to prove which approved request produced the deployed firewall change.
Risks of incomplete firewall requests
Approval gap
Evidence weakness
Scope error
Retention failure
Best practices for firewall change records
Accurate technical scope, controlled approvals, and preserved evidence make the Firewall Change Request Form useful during implementation, review, and incident investigation.
Capture the complete technical scope
Control reusable request templates
Archive approval evidence together
Apply a documented retention policy
Troubleshooting firewall request workflows
Resolve the specific field, approval, plan, and evidence issues that can interrupt a signed Firewall Change Request Form workflow.
signNow Business includes templates, audit trails, mobile apps, and legally binding eSignatures. Confirm that every firewall field is mapped before sending, then review the completed audit trail with the signed request.
Business Premium adds bulk send and kiosk mode, while Business provides the core signing workflow. For a single firewall request, use a reusable template and route it to the required technical approver.
signNow supports audit trails and is compliant with ESIGN and UETA. The record should show intent, signer attribution, consent, and retention; your organization must also follow its security change-control policy.
Use signNow’s signer authentication options, including SMS-based verification where configured, when a firewall request needs stronger identity evidence. Advanced signer authentication is listed for Enterprise plans.
Business plans include 100 signature invites per user per year, with overage fees applying after the included allowance. The Site License uses $1.50 per signature invite for high-volume deployments.
signNow is SOC 2 Type II certified and ISO 27001 certified, and supports encryption in transit with TLS 1.2/1.3 and at rest with AES-256. Apply your own access-control and retention policies to the request.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.