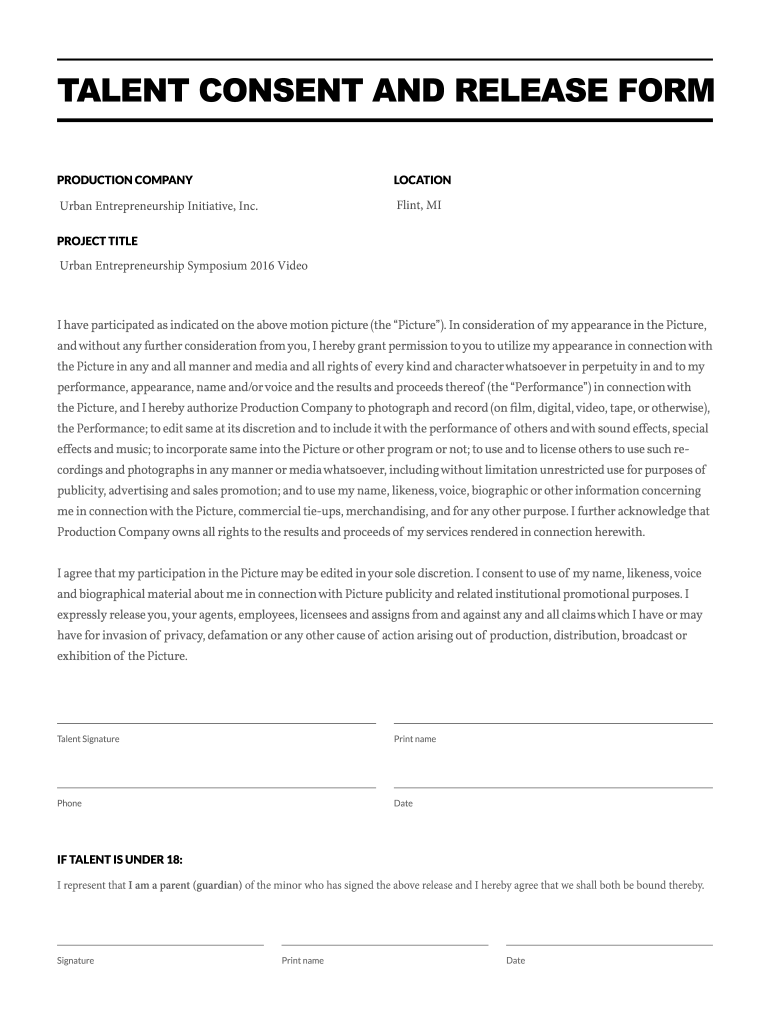
Release Or Obtain Information Consent
Use a Release Or Obtain Information Consent 0 template to make your document workflow more streamlined.
What this information consent does
Release Or Obtain Information Consent is a written authorization that identifies who may obtain or receive specified information and what may be disclosed. The signer reviews the release scope, purpose, recipient, and any expiration terms before signing. In the United States, an electronic version can have legal effect under the ESIGN Act, 15 U.S.C. ch. 96, and applicable UETA or New York ESRA rules when intent, consent, attribution, and reproducible records are established. It does not replace excluded documents such as wills, certain court filings, or family law decrees.
Business types using information consent
Release Or Obtain Information Consent helps organizations document permission before disclosing records, with workflows scaled for individual practices, firms, and enterprise teams.
Solo healthcare practices use Release Or Obtain Information Consent to document patient authorization before sharing records, coordinating signatures through secure email workflows without requiring an in-person visit. Regional legal firms use the form to obtain client permission for targeted information releases, preserving the signed consent and audit trail alongside matter records for later review. Enterprise healthcare networks use standardized consent templates to collect authorization across departments, assign signing roles, and retain completed releases under organization-wide privacy and access policies.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this information consent
Healthcare
Healthcare practices use the release to document patient permission before disclosing specified medical information to named recipients.
Legal and financial services
Legal and financial organizations use the consent to authorize targeted record sharing while preserving signer evidence and disclosure scope.
How information consent works
The signNow workflow converts a completed information release into a traceable electronic signing process, from field preparation through auditable storage.
Upload form: Upload the Release Or Obtain Information Consent file. Add fields: Auto-detect or place authorization and signature fields. Send request: Send the release to designated signers securely. Archive record: Store the completed consent with its audit trail.
Processing stages for information consent
Processing time depends on signer response and the authorization scope, so define every required field before sending Release Or Obtain Information Consent.
Prepare the document
Deliver to signers
Complete signer review
Archive the record
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Inside the consent audit trail
The audit trail records technical evidence around Release Or Obtain Information Consent, helping reviewers connect signer identity, document integrity, and completion history.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log actions:
Export evidence:
Recommended consent workflow setup
Configure Release Or Obtain Information Consent around signer identity, authorization evidence, protected storage, and the retention rule governing the underlying records.
| Setting | Recommendation |
|---|---|
| Authentication and user provisioning | SMS OTP with administrator-managed access |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 |
Legal standing of information consent
A signed Release Or Obtain Information Consent can support admissibility when the signer shows intent, consents to electronic records, can be attributed to the signature, and the record remains reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA law. Wills, codicils, testamentary trusts, certain court orders, and family law decrees remain excluded.

Record-keeping practices for consent
Preserve the signed release, its audit evidence, and the underlying retention rule together so authorized disclosures remain traceable and reviewable.
Match retention to the underlying record
Export the audit trail with the form
Restrict access to authorized personnel
Verify scope before disclosure
Documents requiring special handling
Notarization requirement
Wills excluded
Court orders
Real-estate deed
Privacy pitfalls in information releases
Including broader record categories than the signer intended can create an authorization-scope dispute during a later disclosure review. Sending a release to the wrong recipient can expose protected health information or confidential client records beyond the consent terms. Missing expiration language may make staff uncertain whether an older Release Or Obtain Information Consent still authorizes the requested disclosure. Unrestricted access to completed releases can expose sensitive personal information even when the original consent was properly signed.
Signer authentication options
Two-factor authentication:
ID verification:
PKI certificates:
X.509 certificates:
Email authentication:
Audit evidence:
Mobile options for information consent
Release Or Obtain Information Consent can be prepared and signed through signNow mobile apps on iOS 15 or later and Android 9 or later. Mobile workflows support camera-based document capture, while offline signing helps users complete assigned documents when connectivity is unavailable.
iOS app iOS 15 or later Android app Android 9 or later Mobile tools Offline signing and camera capture
Organizations should manage mobile access through approved devices and account controls when the consent contains health, legal, or other sensitive information. After synchronization, authorized administrators can review the completed release and its audit trail, then apply the retention policy required for the underlying record type.



Troubleshooting information consent workflows
Resolve signer, privacy, and compliance questions by checking the Release Or Obtain Information Consent terms, signNow plan features, and the governing U.S. authority.
On the Business plan, upload the Release Or Obtain Information Consent, place signature and date fields, and send it to each signer. If many recipients need the same release, Business Premium includes bulk send for repeated document distribution.
signNow supports legally binding electronic signatures under its ESIGN and UETA compliance framework. Confirm signer intent, electronic-record consent, attribution, and record reproducibility; consumer-facing disclosures may also require the paper-record rights described in 15 U.S.C. §7001(c).
For health information, signNow lists HIPAA compliance with a business associate agreement required. The organization must still define the permitted disclosure, recipient, access controls, and retention policy under HIPAA 45 CFR §164.530(j).
If a signer cannot complete the form, verify the recipient email, resend the invitation, or provide a signing link. The sender should confirm that the link reaches the intended signer before disclosing any records.
Business includes templates and audit trails, while Enterprise adds advanced signer authentication and integrations. Select the plan based on the authentication, routing, and system requirements for the specific information-release workflow.
A digital signature is not required for every U.S. electronic consent. PKI and X.509 certificates provide cryptographic evidence, while an electronic signature supported by intent, attribution, timestamps, and an audit trail may satisfy ESIGN and UETA requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.