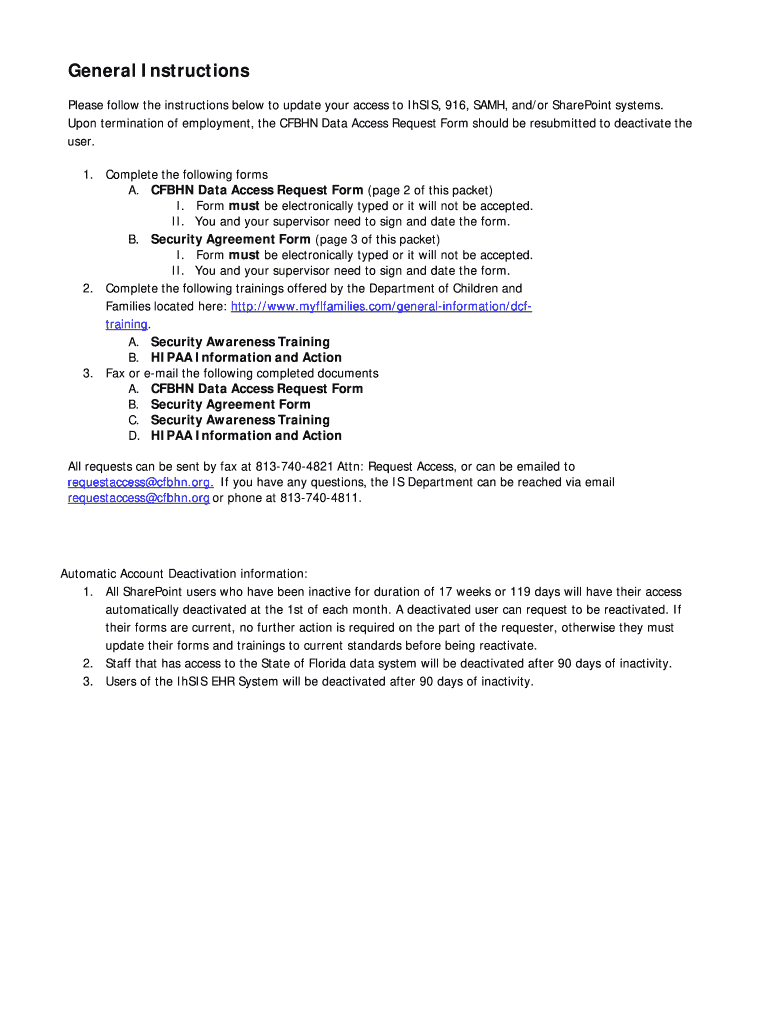
Cfbhn System Access Request Form
Use a Cfbhn System Access Request Form 0 template to make your document workflow more streamlined.
What the access request form does
The Cfbhn System Access Request Form records who needs system access, why access is required, which permissions are requested, and who approved them. In signNow, upload the form, allow automatic field detection, review or add fields, and route it to the requester and approving authority. Each signer completes the assigned fields and signs electronically. The finished form and audit trail provide a single record of the request, approval sequence, timestamps, and signing activity. Organizations should still apply their own identity, provisioning, privacy, and retention policies.
Who benefits from access request workflows
IT service managers use the form to document employee, contractor, and vendor access requests before provisioning accounts. They can route approvals to department owners, preserve authorization evidence, and maintain a consistent record for audits across distributed U.S. operations. Security administrators use it when access involves sensitive systems, regulated data, or elevated permissions. A structured request captures the requester, business justification, approving authority, and requested scope before signNow sends the completed record into the organization’s controlled workflow.
Features for access request records
signNow connects field preparation, signer routing, authentication, audit evidence, reusable templates, and mobile completion to the Cfbhn System Access Request Form.
Field detection
Upload the Cfbhn System Access Request Form and let signNow detect fields before you verify the requested access, business justification, approval, and signature areas.
Role assignment
Assign requester and approver fields to the correct people, preserving the intended authorization order for each Cfbhn System Access Request Form.
Signer authentication
Use SMS-based two-factor authentication when the access request requires stronger evidence that the assigned signer controls the receiving phone.
Audit evidence
Capture the completed request and audit trail together, giving administrators a reviewable record of approval activity and signing timestamps.
Reusable templates
Use reusable templates when the same access request structure applies across employees, contractors, or vendors, while reviewing permission differences individually.
Mobile signing
Complete assigned fields from supported signNow mobile apps when administrators or approvers review access requests away from a desk.
How the access request workflow works
Move the Cfbhn System Access Request Form from an uploaded file to a signed, reviewable authorization record.
Upload form: Upload the request form Review fields: Review detected fields Send request: Route approval requests Store record: Store signed evidence
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Quick steps to complete the form
Prepare the Cfbhn System Access Request Form in signNow, route it to the right people, and verify the completed record.
Upload form:
Upload the Cfbhn System Access Request Form. Check fields:
Review detected fields and add missing fields. Assign recipients:
Assign requester and approver recipients. Send request:
Send the request through signNow. Verify completion:
Review signatures and audit evidence.
What the audit trail records
For the Cfbhn System Access Request Form, the audit trail connects signer identity, document activity, completion evidence, and later review.
Authenticate signer:
Capture timestamp:
Record document hash:
Seal completion:
Review activity:
Export audit trail:
Signer authentication for access requests
PKI authentication:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signer attribution:
Recommended access request setup
Use documented identity checks, signed approvals, audit evidence, and approved retention controls for every access request.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication with SMS OTP |
| Signature type | Electronic signature with signer attribution |
| Audit trail | Retain exported completion records |
| Document retention | Follow the organization’s approved retention schedule |
| Encryption | TLS in transit and AES-256 at rest |
Privacy pitfalls in access requests
Personal data in access requests may appear in completed documents shared with unauthorized recipients or stored outside the approved records system. Missing electronic consent disclosures can weaken evidence that a requester agreed to receive and sign the access request electronically. Broad folder permissions may expose system names, account identifiers, or approval details to employees without a business need. Unsigned approvals can leave administrators unable to prove who authorized access, when approval occurred, or what permission scope was accepted.
Risks of incomplete access requests
Unauthorized access
Weak approval
Privacy disclosure
Access dispute
Troubleshooting access request workflows
Resolve field detection, authentication, plan, evidence, and compliance questions before distributing the completed request.
Upload the original Cfbhn System Access Request Form again and let signNow detect its fillable areas. If fields remain missing, add text, checkbox, date, and signature fields manually before sending the request for approval.
Business includes templates, audit trails, mobile apps, and legally binding eSignatures. Business Premium adds bulk send, kiosk mode, request payments, and quick invite links when the same request must reach many people.
Use signNow’s signer authentication controls, including SMS-based two-factor authentication where configured. For HIPAA-covered workflows, signNow states that HIPAA compliance requires a business associate agreement and appropriate administrative controls.
The completed request can be retained with its audit trail, which records signing activity, timestamps, and signer-related evidence. Export the completion record and follow the organization’s retention policy rather than deleting it after signature.
Electronic signatures can support U.S. transactions under ESIGN and applicable state law when intent, consent, attribution, and record reproduction are established. Consumer-facing records also require the disclosure requirements in 15 U.S.C. §7001(c).
Business Premium includes bulk send, while Business does not include that plan feature. For a small number of individually reviewed access requests, upload the form, place fields, and send each request through the standard workflow.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.