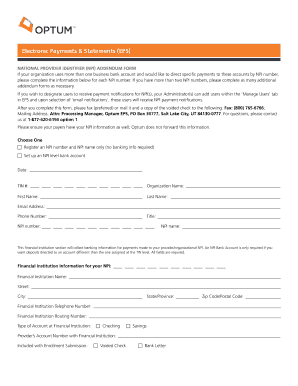
EPS NPI Addendum
Use a EPS NPI Addendum UnitedHealthcareOnline com 0 template to make your document workflow more streamlined.
What the EPS NPI Addendum does
The EPS NPI Addendum is an additional document used with an EPS-related transaction or record, but its issuing authority, required fields, and filing deadline are not identified in the available source material. Treat it as a form-specific record: confirm the accompanying instructions, complete only authorized fields, and verify whether a wet-ink, notarized, or separate submission requirement applies. signNow can upload the document, detect fields, route signatures, and preserve an audit trail; ESIGN and applicable state electronic-transactions law may support electronic execution when no exception applies.
Who uses the EPS NPI Addendum
Business teams
Organizations using EPS NPI Addendum can route the document to designated business, provider, or compliance personnel for review and signature. Because the form’s issuing authority and required fields are not identified here, users should confirm its instructions before submission.
Healthcare organizations
Healthcare organizations may use the addendum when its content concerns provider or network information. Review applicable payer, contract, and privacy requirements before collecting signatures or sharing the completed record.
Features for the EPS NPI Addendum
signNow combines document preparation, signer routing, electronic signatures, and audit evidence for a traceable EPS NPI Addendum workflow.
Field detection
Upload the EPS NPI Addendum and review detected fields before sending, reducing manual preparation while keeping the form’s original structure available for inspection.
Signer routing
Assign each field to a named signer so the required information and signature actions reach the correct participant in sequence.
Online signing
Collect signatures through an email invitation or signing link, allowing authorized participants to complete the addendum without exchanging paper copies.
Audit trail
Capture timestamps, signer actions, and completion history in an audit trail that travels with the completed transaction record.
Reusable template
Use templates when the same EPS NPI Addendum workflow recurs, while reviewing fields whenever the underlying form changes.
Record export
Download the completed PDF and audit trail for controlled storage, internal review, or sharing with authorized recipients.
How to complete the EPS NPI Addendum
Complete the EPS NPI Addendum in signNow by uploading the document, checking detected fields, routing signatures, and preserving the completed record.
Upload the form:
Upload the EPS NPI Addendum file to signNow. Review fields:
Let signNow detect fillable fields, then review every field. Assign signers:
Assign each required field to the correct signer. Send for signature:
Send the completed workflow and monitor its signing status. Store records:
Download the signed document and audit trail together.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended EPS NPI Addendum setup
Configure the workflow around signer attribution, document integrity, access control, and the retention obligation applicable to the EPS NPI Addendum.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with optional SMS authentication |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enabled with completion certificate |
| Document retention | Apply the governing records rule |
| Encryption | TLS in transit and AES-256 at rest |
What the audit trail records
The signNow audit trail documents signer identity, event timing, document integrity, and completion history for the EPS NPI Addendum.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
Privacy and disclosure pitfalls
Personal or provider identifiers may appear in the final PDF; restrict access and share only with authorized recipients. A missing electronic-record consent disclosure can create issues when the signer is a consumer under ESIGN requirements. Assigning a signature field to the wrong person weakens attribution and can delay acceptance of the addendum. Sending the completed EPS NPI Addendum through unapproved channels can expose confidential business or health information.
Security for the EPS NPI Addendum
Data in transit:
Stored data:
Security reporting:
Information security:
Health information:
Electronic records:
Platform requirements for signing
Use signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. Mobile signing is available through signNow apps for iOS and Android, subject to the device’s current supported app requirements.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android signNow apps
Organizations handling sensitive EPS NPI Addendum information should manage access through approved devices and accounts. Confirm browser updates, mobile permissions, identity controls, and storage policies before deploying the workflow to external signers or regulated teams.
Record-keeping practices for the addendum
Preserve the signed EPS NPI Addendum as a complete, reproducible record, and apply the retention rule that actually governs its information and business purpose.
Preserve the complete signed package
Map retention to the governing rule
Export the audit trail
Control archival access
Processing stages for the addendum
The EPS NPI Addendum moves through preparation, delivery, signer completion, and archival; actual timing depends on the parties and any governing instructions.
Document preparation
Delivery to signers
Signer turnaround
Completion and archival
Business types using the addendum
The EPS NPI Addendum is most useful where provider, network, business, or compliance teams must exchange a controlled supplemental record.
Solo healthcare practitioners can prepare and sign an EPS NPI Addendum from a desktop or mobile device, then retain the signed PDF and audit trail with the related provider record. Healthcare operations teams can route the addendum through assigned signers, review completion status, and apply HIPAA controls when the document contains protected health information. Enterprise compliance departments can standardize recurring addendum workflows with templates, controlled permissions, audit exports, and integrations such as Salesforce, NetSuite, or Microsoft 365.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
EPS NPI Addendum troubleshooting
These answers address document preparation, electronic-signature validity, consent, audit evidence, plan selection, and protected information for the EPS NPI Addendum.
Upload the EPS NPI Addendum as a PDF or supported document, then inspect every detected field before sending. If a field is missing, add it manually and confirm its assigned signer, because automatic detection cannot establish the form’s legal requirements.
The Business plan is listed at $8 per user per month with annual billing and includes legally binding eSignatures and audit trails. Confirm the selected plan’s current limits and any required enterprise controls before routing this document.
signNow states that ESIGN and UETA compliance supports electronic transactions, but those frameworks do not remove document-specific exceptions. Confirm that this addendum is not subject to a notarization, wet-ink, or filing rule before using electronic signatures.
For consumer-facing records, ESIGN requires disclosure of the right to paper records, electronic-access capability, and procedures for withdrawing consent under 15 U.S.C. §7001(c). Capture the required disclosure before sending if the signer is a consumer.
Use signNow’s audit trail and completion certificate to preserve signer actions, timestamps, and transaction history. Export them with the signed EPS NPI Addendum; the audit trail supports evidence but does not replace a separate filing obligation.
If the addendum contains protected health information, signNow identifies HIPAA compliance as requiring a BAA. Establish that agreement and apply organizational access controls before sending the document through a healthcare workflow.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.