For Infection Control Policy Form
Use a Template For Infection Control Policy 0 template to make your document workflow more streamlined.
What the infection control policy form does
The For Infection Control Policy Form records an organization’s infection-prevention expectations, responsibilities, and acknowledgments for staff or other affected participants. It gives the signer a defined policy to review and accept, while the organization retains evidence of delivery and completion. With signNow, upload the form, let the editor detect fillable fields, place signer and acknowledgment fields, send it for signature, and store the completed document with its audit trail. The form itself does not replace OSHA, HIPAA, CDC, state health-department, or facility-specific requirements.
Who uses the infection control policy form
Healthcare providers
Healthcare organizations use the form to document staff acknowledgment of infection-prevention policies, training expectations, and facility procedures. HIPAA-covered entities should limit protected health information, apply role-based access, and retain relevant records six years under 45 CFR §164.530(j).
Employers and facilities
Employers and public-facing facilities use the form to distribute workplace infection-control rules and capture employee acknowledgment. Exposure-related records may require thirty-year retention under 29 CFR §1910.1020, separate from the policy acknowledgment itself.
Key features for infection-control policies
signNow connects field preparation, signer routing, electronic acknowledgment, audit evidence, and controlled storage for this infection-control policy workflow.
Field detection
Upload the infection-control policy and let signNow detect fillable areas, reducing manual field placement before staff acknowledgments are requested.
Signer routing
Assign policy acknowledgments to named recipients and route the document in a defined order when multiple staff members must review it.
Electronic signing
Collect typed or drawn electronic signatures while preserving the signer’s intent, completed document, and related event history.
Audit trail
Capture delivery, access, signing, and completion events in an audit trail that supports later policy review.
Protected storage
Use controlled permissions and encrypted storage for completed policies that may contain employee or health-related information.
Record retrieval
Retrieve the signed policy and audit trail together when compliance, quality, or workplace-safety teams need supporting evidence.
How to complete the policy form
Prepare the infection-control policy, identify every required acknowledgment, and use signNow to route the document for review, signature, and controlled storage.
Upload form:
Upload the completed policy form. Check fields:
Review detected fields and add acknowledgments. Assign signers:
Assign each signer and send securely. Archive records:
Download the signed copy and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security controls for signed policy forms
Transport encryption:
Storage encryption:
Health information:
Control assurance:
Security management:
Privacy controls:
What the policy audit trail records
The audit trail documents who received, reviewed, and signed the infection-control policy, creating a reproducible record for compliance review.
Signer authentication:
Timestamp capture:
Document history:
Tamper evidence:
Event logging:
Audit export:
Find and fill out the correct template for infection control policy
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
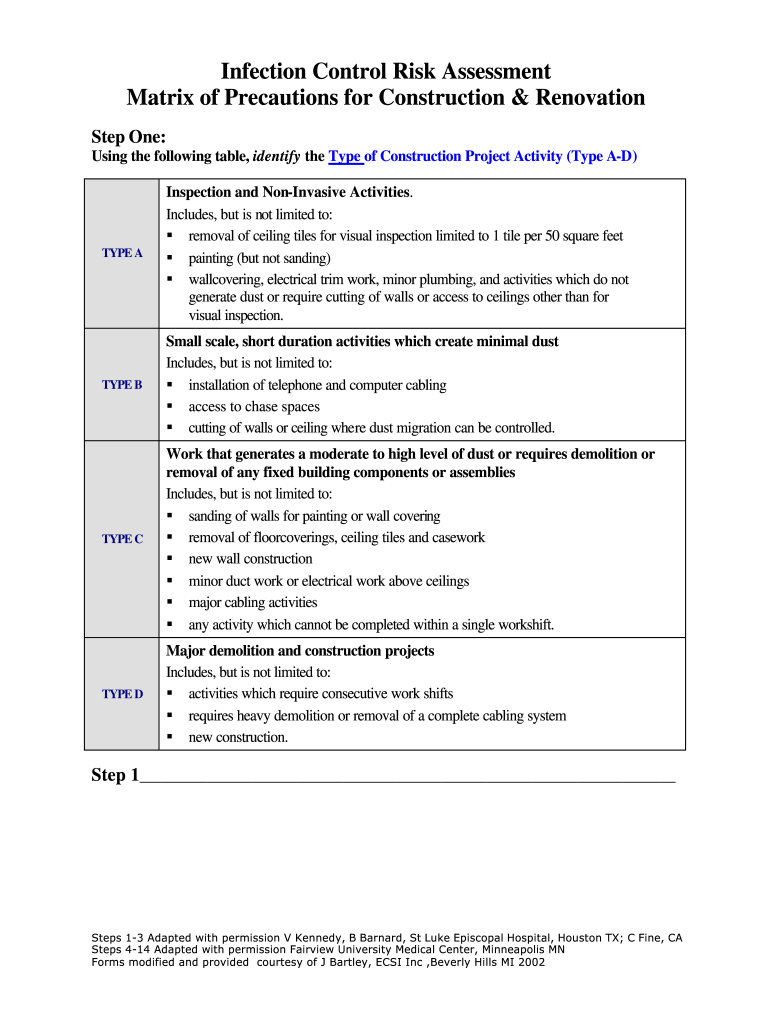
| *Infection Control Risk Assessment Matrix of Precautions for Construction & Renovation 2005 | 4.7 Satisfied (65 Votes) |
Privacy risks when handling infection-control forms
Including employee names, health details, or exposure information in an unnecessarily broad distribution list can disclose sensitive personal data. A missing electronic-record consent disclosure may weaken the workflow when employees or patients receive the policy as consumers. Leaving completed infection-control forms in shared folders can give unauthorized staff access to protected health information. Using one signer identity for multiple staff members makes attribution difficult when the signed policy is later reviewed.
Retention periods for infection control records
Keep each signed policy record according to the applicable federal rule, organizational role, and health-information context.
Six years for HIPAA records
Five years for injury records
Thirty years for exposure records
Three years for payroll records
Seven years for SOX audit records
Record-keeping practices for infection-control forms
Use a documented retention and archival process that connects the signed form, its audit trail, access controls, and applicable federal requirements.
Export audit trails with signed records
Classify records before archival
Restrict access to archived policies
Test retrieval and reproducibility
Recommended infection policy workflow setup
Configure the policy workflow around signer identity, protected information, audit evidence, and the retention rule applicable to the completed record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email delivery with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with the completed policy |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 |
Legal standing of signed policy acknowledgments
A signed infection-control policy acknowledgment can be evidence of intent and receipt when the signer is identified, consents to electronic records, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable UETA laws generally recognize electronic signatures, but they do not make the policy itself a substitute for required health, safety, employment, or state-law procedures.

Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting the infection control policy form
Resolve field, signer, compliance, plan, and retention questions before distributing the For Infection Control Policy Form to staff or other participants.
SignNow’s document editor can detect fillable areas after upload, but review every infection-control acknowledgment, date, and initials field manually before sending. Add missing fields yourself, assign each field to the correct employee or supervisor, and test the completed document before production use.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps. Business Premium adds bulk send and kiosk mode, which may help when distributing the same infection-control policy to many staff members.
If the policy contains protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm the BAA and configure access controls before placing PHI in the document or its attachments.
Electronic execution generally depends on intent, consent, attribution, and record reproducibility under ESIGN and UETA. For consumer-facing records, provide the ESIGN disclosure and confirm electronic access before requesting acknowledgment.
Paid subscription plans include 100 signature invites per user per year, with overage fees. Business Premium includes bulk send, while the Site License uses $1.50 per signature invite and unlimited users.
Export the completed policy and audit trail together, then apply the retention rule for the record’s actual contents. HIPAA records generally require six years under 45 CFR §164.530(j); state and industry rules may require longer retention.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.