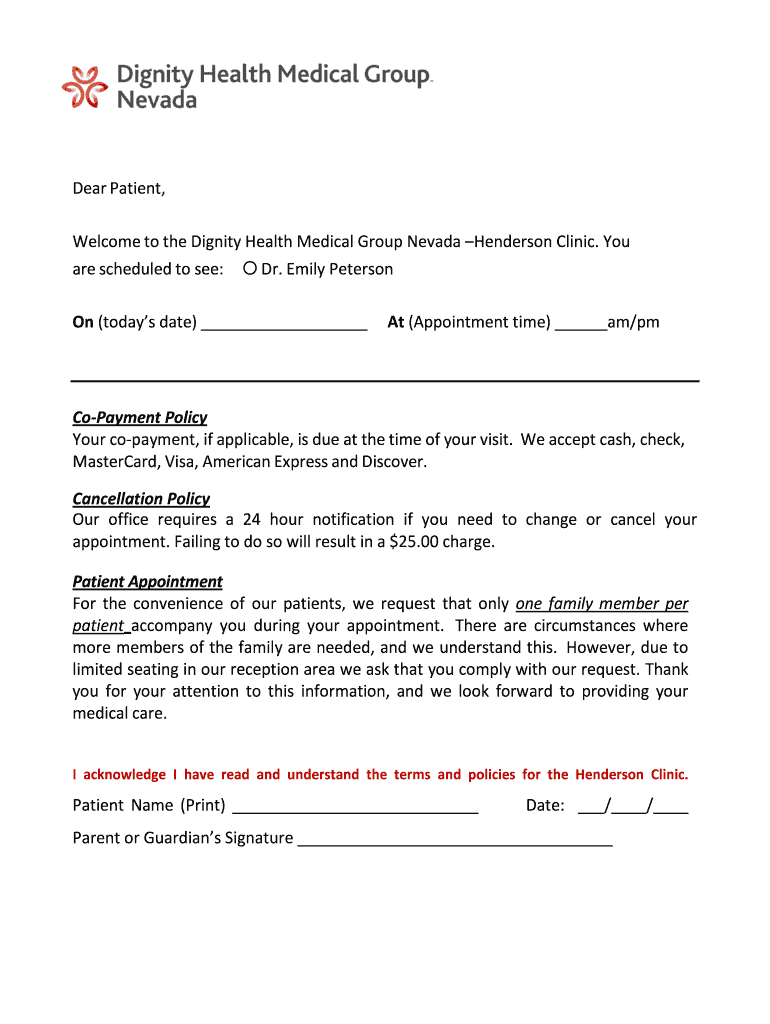
Dignity Health Authorization Form
Use a Dignity Health Authorization Form 0 template to make your document workflow more streamlined.
What the Dignity Health Authorization Form does
The Dignity Health Authorization Form records a patient’s permission for specified health information or healthcare actions to be handled by an authorized organization or representative. In signNow, a sender uploads the form, reviews detected fields, assigns patient and representative roles, and sends the document for electronic signature. The completed PDF is paired with an audit trail showing signer activity and timestamps. Healthcare organizations handling protected health information should use a HIPAA-compliant configuration and business associate agreement, then retain the authorization according to 45 CFR §164.530(j) and applicable state requirements.
Features that support Dignity Health authorizations
signNow combines document preparation, signer routing, evidence capture, and protected storage workflows for organizations processing Dignity Health Authorization Form records.
Field detection
Upload the Dignity Health Authorization Form and let signNow detect fillable fields, reducing manual placement work before staff review the patient-specific information.
Role-based signing
Assign patients, representatives, or organizational signers to defined fields so each person signs the correct portion of the authorization form.
Remote signing
Send the form by email or signing link when a patient or representative is outside the facility and cannot sign at a desk.
Audit trail
Capture timestamps, signer actions, and document history alongside the completed authorization, supporting later review of how consent was obtained.
Mobile completion
Use mobile apps when staff or patients complete the authorization away from a workstation, including supported signing workflows on mobile devices.
HIPAA controls
Protect health information with HIPAA compliance and a required business associate agreement when the workflow handles protected health information.
Recommended setup for health authorizations
Configure the authorization workflow around verified signer identity, protected health information, audit evidence, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication for representatives |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with the completed authorization |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption and provisioning | AES-256 storage with role-based access |
Complete this authorization form in signNow
Use this sequence to prepare the Dignity Health Authorization Form, collect the required signature, and preserve the completed record.
Upload form:
Upload the Dignity Health Authorization Form PDF. Detect fields:
Let signNow detect existing fillable fields automatically. Check details:
Review patient, representative, scope, and date fields. Send request:
Add signer roles, then send the authorization request. Save record:
Store the signed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How signNow records authorization evidence
The audit trail preserves signer identity, timing, document integrity, and retrievable evidence for each completed Dignity Health Authorization Form.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
Security controls for health authorizations
Health data protection:
Transport encryption:
Stored-data encryption:
Operational controls:
Security management:
Signer authentication:



Privacy pitfalls when handling authorizations
Including unnecessary patient details in the authorization increases exposure if the completed document reaches an unintended recipient. Skipping the electronic-records disclosure can weaken evidence that the patient consented to the digital signing process. Assigning broad folder permissions can expose signed authorizations and audit trails beyond staff with a valid business need. Sending an authorization before checking its scope, expiration, or representative details may require a replacement signature.
Legal standing for health authorizations
A completed Dignity Health Authorization Form can provide evidence of consent when the signer demonstrates intent, consents to electronic records, and the record remains attributable and reproducible. ESIGN and UETA support electronic signatures, but wills, certain court orders, and family-law decrees remain excluded under federal law.

Retention schedule for authorization records
Healthcare organizations should align Dignity Health Authorization Form retention with the applicable HIPAA documentation rule and any longer state requirement.
Six years: signed authorization
Six years: patient copy
Six years: representative consent
Six years: disclosure record
Six years: audit evidence
Record-keeping practices for signed authorizations
Apply a documented process for protecting, exporting, and retaining Dignity Health Authorization Form records after signature.
Keep authorization evidence together
Export the audit trail
Restrict patient-record access
Verify scope before sending
Troubleshooting Dignity Health authorizations
These answers address field detection, HIPAA handling, signer authentication, audit evidence, and corrections for this authorization workflow.
Upload the original Dignity Health Authorization Form PDF again and review the detected fields before sending. If a field is missing or misaligned, add or reposition it manually, then verify every patient and representative field in the preview.
The Business plan includes templates, audit trails, and mobile apps, while Business Premium adds bulk send and kiosk mode. Choose the plan based on whether staff process one authorization at a time or repeated patient batches.
A HIPAA workflow requires signNow’s HIPAA-compliant configuration and a business associate agreement. Confirm that the organization has the required BAA before placing protected health information in the Dignity Health Authorization Form workflow.
Use stronger signer authentication, such as two-factor authentication or SMS verification, when email-only access does not adequately connect the authorization to the patient or representative. Document the selected control in your internal procedure.
Review the audit trail for signer identity, timestamps, actions, and the completed document. Export the evidence with the signed authorization, then retain both according to 45 CFR §164.530(j) and applicable state requirements.
If the authorization is incomplete, void or replace the pending request before issuing a corrected version. Do not alter a signed PDF; preserve the original record and document why the replacement was required.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.