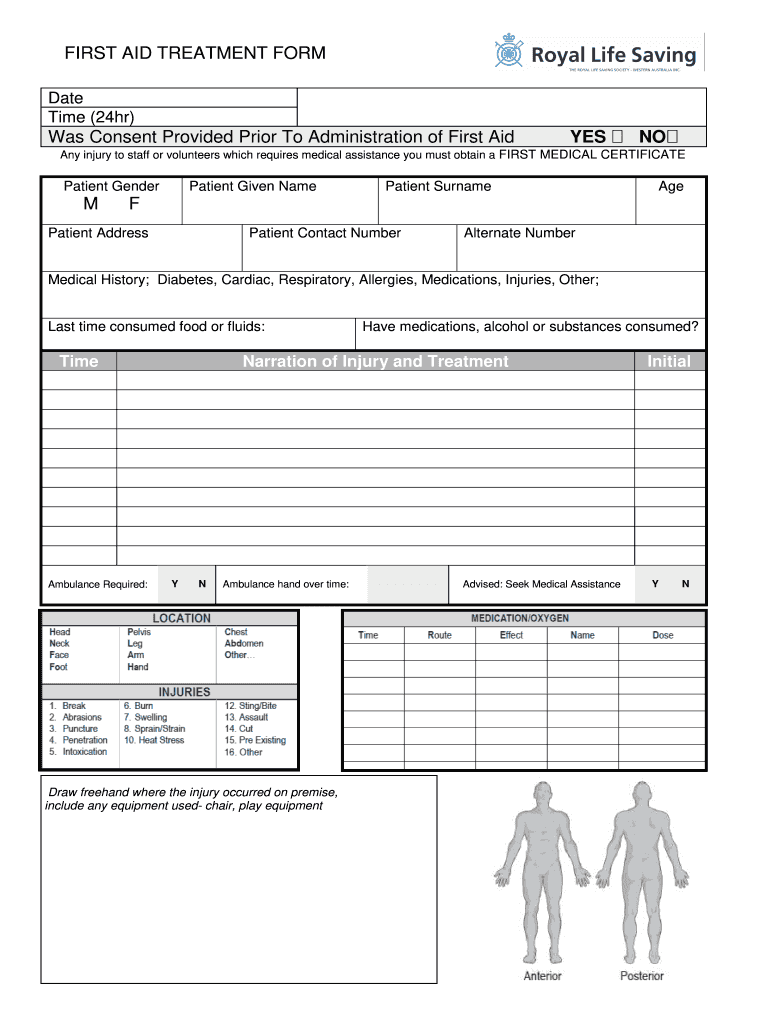
Incident Report Australia Form
Use a Incident Report Template Australia 0 template to make your document workflow more streamlined.
What Incident Report Australia Form does
Incident Report Australia Form is a structured record for documenting an event, the people involved, observed facts, immediate response, and required acknowledgments. In a U.S. workflow, a team can upload the form to signNow, review or add fillable fields, route it to designated signers, and retain the completed PDF with its audit trail. The form itself does not establish a universal U.S. filing deadline or retention period; workplace safety, healthcare, securities, and state rules can change the applicable obligation. Confirm the governing authority before finalizing policy.
Who uses the incident report form
Workplace safety
Safety managers and supervisors document workplace events, identify involved people, and route the Incident Report Australia Form for acknowledgment and review.
Regulated operations
Healthcare and public-sector teams record incidents involving sensitive information, using controlled access, signer authentication, and an auditable completion record.
How the incident report workflow works
The signNow workflow moves the Incident Report Australia Form from upload through field review, signature collection, and auditable storage.
Upload report: Upload the completed incident report. Detect fields: Auto-detect fillable fields for review. Send for signature: Send required fields to designated signers. Store securely: Store the signed report with its audit trail.
What the incident report audit trail records
The audit trail connects signer identity, event timing, document integrity, and retrieval evidence for Incident Report Australia Form.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Deliver completion:
Export audit trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Signer authentication and certificate controls
PKI signatures:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signing evidence:
Platform requirements for incident reports
Complete the Incident Report Australia Form through Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow uses TLS 1.2/1.3 for data in transit, and mobile apps are available for iOS and Android workflows.
Browser support Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Connection security TLS 1.2/1.3 encrypted connection
Organizations handling sensitive incident details should manage device access, assign appropriate signNow roles, and configure identity controls before sending. API, SSO, certificate, and long-term validation requirements depend on the selected plan and the organization’s recordkeeping policy.



Recommended incident report workflow setup
Configure Incident Report Australia Form around signer identity, evidence preservation, encryption, and the retention rule applicable to the incident record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email plus SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP, and action history |
| Document retention | Apply the governing record rule |
| Encryption | TLS 1.2/1.3 and AES-256 |
Best practices for completing incident reports
Accurate facts, deliberate routing, controlled access, and preserved completion evidence make Incident Report Australia Form more useful for review and later records requests.
Record factual incident details before signing
Assign signer fields to accountable reviewers
Retain the signed report and audit trail
Limit unnecessary personal information and recipients
Privacy pitfalls in incident reporting
Including medical details or identification numbers that are unrelated to the incident increases unnecessary disclosure and access-control exposure. Sending the Incident Report Australia Form before obtaining required consent or acknowledgment can weaken evidence that the signer understood the electronic record. Granting every team member access to completed reports can expose personal information beyond the investigation or safety purpose. Sharing a completed report through an unapproved email or storage location can undermine confidentiality controls and retention tracking.
Retention periods for incident records
Retention depends on the incident record’s regulatory context, especially workplace safety, health information, securities, or audit obligations.
Five years: OSHA injury records
Thirty years: OSHA exposure records
Six years: HIPAA incident records
Seven years: SOX audit records
Six years: broker-dealer records
Incident report form troubleshooting
These answers address field detection, signer access, audit evidence, plan capabilities, and regulated handling for Incident Report Australia Form.
Business includes legally binding eSignatures, templates, and audit trails. Upload the report, verify detected fields, and assign recipients before sending. signNow states that Business includes 100 signature invites per user annually; check the account’s usage and overage terms before high-volume deployment.
Use signNow’s field editor to inspect every detected field after upload. Add missing signature, date, initials, or acknowledgment fields manually, then send a test copy to confirm placement before routing the final Incident Report Australia Form.
An audit trail supports attribution and record integrity by documenting actions, timestamps, and signer events. Under ESIGN and UETA, enforceability also depends on intent, consent where required, attribution, and the ability to retain and reproduce the record.
A HIPAA-covered incident report requires an appropriate business associate arrangement with signNow and controlled access to protected health information. HIPAA’s six-year retention rule is in 45 CFR §164.530(j), subject to applicable state requirements.
Business Premium includes bulk send and kiosk mode, while Enterprise adds advanced signer authentication. If the Incident Report Australia Form requires repeated distribution or stronger identity checks, select the plan based on those documented needs.
If a signer cannot open the report, confirm the email address, signing link, browser, and network connection. Retry in Chrome, Firefox, Safari, or Edge, and verify that required fields are assigned to the intended signer.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.