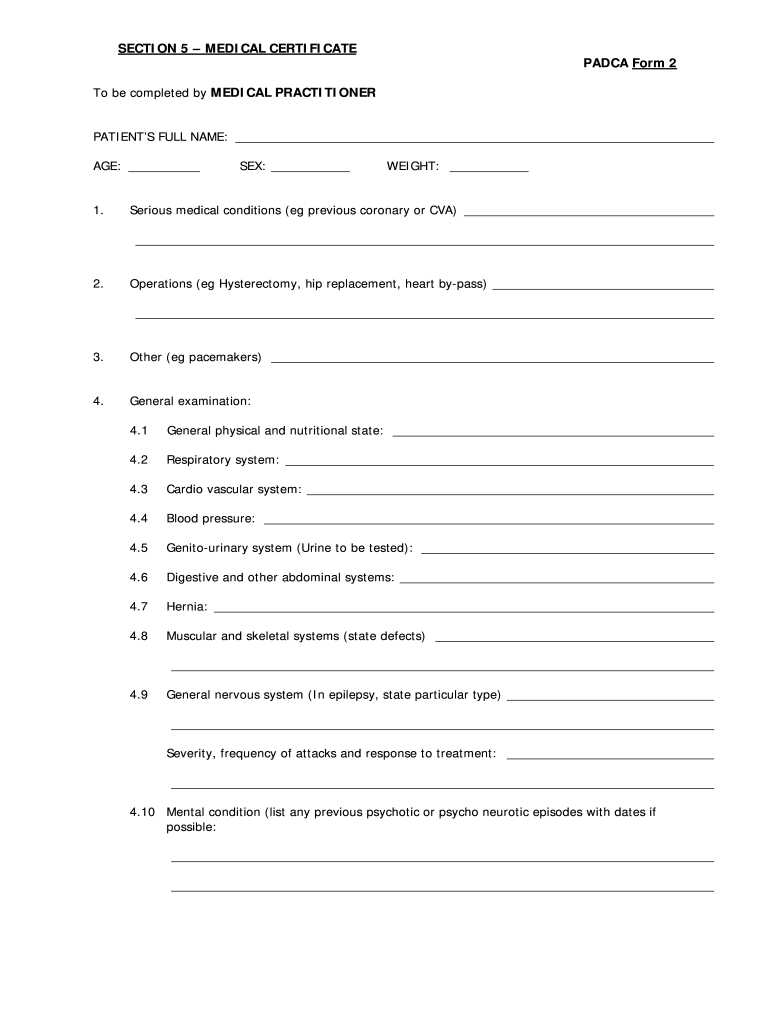
Section 5 Medical Certificate Bpadcab Form 2 Padca Co
Use a SECTION 5 MEDICAL CERTIFICATE BPADCAb Form 2 Padca Co 0 template to make your document workflow more streamlined.
What this medical certificate does
Section 5 Medical Certificate Bpadcab Form 2 Padca Co is a medical certificate form used to document the information requested in its Section 5 record. Because the supplied form name does not identify an issuing agency, deadline, or required medical findings, those details should be confirmed against the source instructions before submission. In signNow, upload the certificate, let the editor detect fillable areas when possible, add any missing fields, assign signers, and send it for completion. The finished PDF and audit trail provide a retained record of the signing event.
Who may use this certificate
Medical offices
A clinic or medical office can use signNow to route the certificate to the appropriate clinician, patient, or authorized representative while limiting access to assigned recipients. The sender should verify that the completed document meets the receiving organization’s submission rules.
Requesting organizations
Employers, schools, insurers, and benefit administrators may request a completed medical certificate, but each recipient controls its required fields and deadline. signNow can collect signatures and retain evidence without deciding whether the underlying medical information is sufficient.
Legal standing and evidentiary value
For a U.S. business transaction, a signed Section 5 Medical Certificate may be evidence when the signer intended to sign, consented to electronic records, can be identified, and the record remains reproducible under ESIGN and applicable UETA provisions. Wills, court orders, and certain family-law documents remain excluded or subject to separate rules.

Key features for this certificate
signNow connects certificate preparation, signer routing, authentication, audit evidence, and controlled storage in one documented workflow.
Field placement
Upload the Section 5 certificate and use signNow’s editor to identify fillable areas, then add missing text, date, initials, or signature fields without recreating the document.
Role assignment
Assign each field to the correct clinician, patient, representative, or recipient so signers see only the information and actions intended for them.
Remote completion
Send the prepared certificate by email or signing link, allowing authorized recipients to review and complete it remotely when the receiving organization permits electronic records.
Audit trail
Capture timestamps, signer actions, and authentication details in an audit trail that can accompany the completed certificate during internal review or records requests.
Controlled access
Use signNow access controls and authentication options to reduce exposure of medical information while preserving a clear record of who completed each assigned field.
Record retention
Keep the final certificate and completion evidence together in an approved repository, applying the organization’s medical-record retention and disclosure policy.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Signer authentication and certificates
PKI support:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signing evidence:
Recommended certificate workflow setup
Configure the certificate workflow around signer identity, protected information, audit evidence, and the receiving organization’s retention requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS two-factor authentication |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with completed certificate |
| Document retention | Six years for HIPAA records |
| Encryption and provisioning | TLS 1.2/1.3, AES-256, role-based access |
Platform requirements for signing
Use an up-to-date version of Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow mobile apps support iOS and Android, while encrypted connections protect certificate data during transmission.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile access iOS and Android mobile apps
Organizations handling medical information should use managed devices, controlled accounts, and approved storage locations. Enterprise deployments may also evaluate SSO, API access, and a HIPAA business associate agreement before routing Section 5 certificates through production workflows.
How to complete the certificate
Use this signNow sequence to prepare, route, complete, and preserve Section 5 Medical Certificate Bpadcab Form 2 Padca Co.
Upload certificate:
Upload the source PDF to signNow. Check fields:
Review detected fields and add missing fields. Assign roles:
Assign each field to its signer. Complete record:
Send, sign, download, and retain evidence.
What the audit trail records
The signNow audit trail documents the signing event separately from the certificate’s medical content, supporting review and record reproduction.
Authenticate signer:
Timestamp event:
Hash document:
Seal document:
Log activity:
Export trail:
Retention and record-keeping practices
Preserve the signed certificate, its audit evidence, and the authorization context under the applicable medical-record policy.
Confirm the applicable retention period
Export the certificate and audit trail
Archive records with restricted access
Record the disclosure context
Privacy pitfalls for medical certificates
Including diagnoses, treatment details, or identifiers that the receiving organization did not request can expose unnecessary protected health information. Sending the certificate to a shared mailbox or unrestricted folder can give unauthorized staff access to sensitive medical information. Skipping electronic-record consent or failing to show a signer how to access the completed certificate can weaken the transaction record. Using one shared signNow account for multiple staff members makes signer attribution and access review less reliable.
Troubleshooting this medical certificate
These answers address certificate preparation, signer access, medical-information protection, and records management in signNow.
If the uploaded certificate is not recognized, confirm that it is a readable PDF, then use signNow’s editor to place fields manually. The Business plan supports templates and audit trails; signer identity, intent, and record retention still must satisfy ESIGN and UETA requirements.
signNow supports SMS-based two-factor authentication and other signer authentication options. For protected health information, use a signNow HIPAA workflow with a business associate agreement, restrict access, and confirm that the certificate contains only necessary information.
A signer can complete the document without creating a signNow account when the sender permits guest signing. The sender can require SMS authentication, review the audit trail, and retain the completed certificate and completion record together.
The Business Premium plan includes bulk send, while Business includes templates and audit trails. If multiple certificates require different recipient data, use separate templates or controlled field mapping rather than reusing one recipient’s information.
Electronic signatures generally receive legal recognition under ESIGN and UETA when intent, consent, attribution, and record reproduction are established. Those laws do not replace medical-record, professional-licensing, or state-specific submission rules for this certificate.
Export the completed document and its signNow audit trail after signing, then store both under the organization’s approved retention policy. A HIPAA-covered record generally requires six years from creation or its last effective date under 45 CFR 164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.