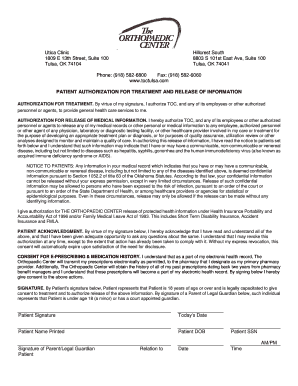
Patient Auth TOC53 The Orthopaedic Center Form
Use a Patient Auth TOC53 The Orthopaedic Center 0 template to make your document workflow more streamlined.
What the Patient Auth TOC53 form does
The Patient Auth TOC53 The Orthopaedic Center Form is a healthcare authorization document used to record a patient’s permission for specified access, communication, or care-related activity. Because the source template’s issuing authority, fields, and filing deadline are not identified here, the practice should confirm those details before use. With signNow, an authorized staff member can upload the form, place or verify fillable fields, assign the patient and staff signer roles, send it securely, and retain the completed document with its audit trail. HIPAA requirements apply when the workflow handles protected health information.
Features that fit patient authorization
Patient Auth TOC53 workflows benefit from controlled field placement, identified signers, documented consent, and secure handling of patient information.
Verified fields
Upload the Patient Auth TOC53 form and verify each patient, provider, date, and authorization field before sending, reducing transcription errors in a healthcare record.
Signer routing
Assign the patient and authorized representative to the correct signature or acknowledgment fields so each consent action is attributed to the intended person.
Audit trail
Use signNow’s audit trail to preserve signer actions, timestamps, and document history alongside the completed authorization for later record review.
HIPAA workflow
Protect patient-related information with a HIPAA-compliant signNow workflow when the organization has the required Business Associate Agreement in place.
Reusable template
Use reusable templates for the approved TOC53 layout, while requiring staff to confirm patient-specific information before every send.
Secure storage
Keep the finalized authorization and completion record together in the organization’s approved storage system for retrieval during care or compliance review.
How to complete TOC53 online
Follow this workflow to prepare, route, sign, and retain the Patient Auth TOC53 form without changing its approved healthcare content.
Upload:
Upload and review the approved Patient Auth TOC53 file. Verify:
Confirm patient-specific fields and authorization language. Route:
Assign patient and staff signature fields. Send:
Send through the approved signNow channel. Archive:
Review completion evidence and store securely.
Choose the right signing method
- Use the signNow web app when staff prepare the Patient Auth TOC53 form, verify its patient-specific fields, and route it to authorized signers from a controlled workstation.
- Use the signNow mobile app when authorized healthcare staff need to review or send the completed authorization from an iOS or Android device.
- Use kiosk mode for an approved in-person intake station, ensuring the patient can review the Patient Auth TOC53 form before signing on the designated device.
- Use a shareable signing link only when the organization controls distribution, identifies the patient securely, and prevents unauthorized access to protected health information.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended TOC53 workflow setup
Use patient identity checks, documented consent, controlled access, and retention aligned with the healthcare organization’s approved policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion history export |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2 or 1.3 and AES-256 at rest |



Security controls for TOC53
HIPAA protection:
Data in transit:
Stored data:
Service controls:
Security management:
Electronic signatures:
What the TOC53 audit trail records
The signNow audit trail documents the events surrounding the Patient Auth TOC53 authorization, separate from the form’s clinical content.
Authenticate signer:
Timestamp action:
Track document:
Seal history:
Confirm completion:
Export trail:
Record-keeping practices for TOC53
Preserve the authorization, its completion evidence, and access history under the healthcare organization’s records policy.
Confirm the governing retention period
Export the audit trail
Restrict protected health information
Apply legal holds first
TOC53 document retention schedule
Retention depends on the record’s healthcare purpose, state requirements, and organizational policy; HIPAA supplies a six-year federal baseline for specified documentation.
Six years for HIPAA records
State schedule may be longer
Until legal hold release
For the approved record period
Before secure disposition
Challenges when processing TOC53
Scanned Patient Auth TOC53 pages may produce misplaced fields, requiring staff to compare every detected field with the approved source template. Sending patient information to the wrong address can expose protected health information and undermine confidence that the intended patient provided authorization. An incomplete representative or witness section can leave the authorization ambiguous, even when the patient’s primary signature is present. Saving the signed form without its audit trail may make it harder to demonstrate signer identity, intent, timestamps, and document history.
Mobile options for TOC53
Staff can work with the Patient Auth TOC53 form through the signNow mobile apps for iOS and Android. Use a supported device, a secure connection, and the organization’s approved controls when viewing or capturing patient-related documents.
iOS app iOS 15 or later Android app Android 10 or later Document capture Camera capture available
Offline signing and camera-based capture should follow the healthcare organization’s device-management, encryption, and protected-health-information policies. Confirm current signNow app requirements before deployment, and avoid storing captured Patient Auth TOC53 images in an unmanaged photo library.
TOC53 signing and compliance questions
These answers address specific upload, routing, authentication, HIPAA, and electronic-record issues for the Patient Auth TOC53 workflow.
Upload the original Patient Auth TOC53 file again and check that it opens correctly before placing fields. signNow Business includes templates and audit trails; confirm that the source PDF is not password-protected or damaged.
Open the document in signNow’s editor and inspect every detected field. Auto-detection can require review, especially for scanned forms, so verify patient names, dates, authorization text, initials, and signature locations before sending.
Use signNow Business Premium when the same Patient Auth TOC53 authorization must be sent to many identified patients or representatives. The plan includes bulk send; do not assume Business includes that feature.
A healthcare workflow involving protected health information requires the appropriate signNow HIPAA configuration and Business Associate Agreement. HIPAA compliance is not created by an electronic signature alone; confirm organizational and contractual controls.
If a patient cannot access the signing request, confirm the email address, resend the invitation, or use a controlled signing link. For sensitive records, verify identity before changing delivery or authentication settings.
Electronic signatures may support admissibility under ESIGN and applicable state law when intent, consent, attribution, and record reproduction are shown. The Patient Auth TOC53 form must still satisfy healthcare, state, and organizational requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.