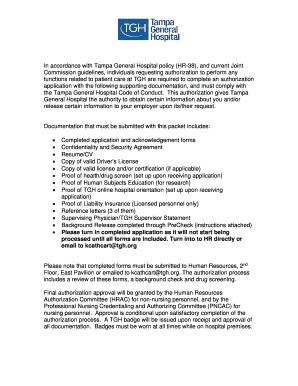
Functions Related To Patient Care At Tgh Are Required To Complete An Authorization Form
Use a Functions Related To Patient Care At TGH Are Required To Complete An Authorization 0 template to make your document workflow more streamlined.
What this patient authorization form does
This form records a patient’s authorization for a defined patient-care purpose and identifies the people or organizations involved. In practice, the requester completes the patient, recipient, purpose, information-scope, expiration, and signature details required by the document. With signNow, staff upload the form, review or add fillable fields, assign them to the patient or authorized representative, and send it for signing. The completed form can be retained with its audit trail. HIPAA-covered records require six-year retention from creation or the last effective date under 45 CFR 164.530(j).
Who uses this patient authorization form
Healthcare providers
Healthcare providers use the authorization to document a patient’s permission for specified patient-care information or activities. Staff can upload the form, assign patient and representative fields, collect signatures, and preserve an auditable record without changing the authorization’s substantive terms.
Patients and representatives
Patients and authorized representatives review the defined scope, complete required identifying details, and sign when they understand the request. The completed copy and audit trail help demonstrate who signed, when the authorization was completed, and which version was presented.
Key features for patient authorizations
signNow combines field preparation, controlled routing, electronic signing, and audit evidence for teams processing this patient-care authorization.
Form preparation
Upload the authorization and review automatically detected fillable fields before adding patient, representative, date, and signature assignments.
Role-based routing
Assign fields to named recipients so each signer completes only the information intended for that person’s role in the authorization.
Audit trail
Capture email verification, timestamps, actions, and completion history with the signed patient authorization for later review.
Mobile signing
Use signNow’s mobile apps when authorized representatives need to review or sign the authorization away from a desktop workstation.
HIPAA controls
Apply HIPAA-compliant workflows with a BAA when the authorization contains protected health information.
Record retention
Store the completed form with its audit trail and maintain access controls aligned with the organization’s health-record policy.
Complete the patient authorization form
Upload the authorization, verify every patient-care field, route it to the correct signer, and preserve the completed record.
Upload document:
Upload the authorization document to signNow. Check fields:
Review detected fields and add missing patient, provider, and signature fields. Assign signers:
Assign each field to the correct patient or authorized representative. Send securely:
Send the authorization for secure electronic signing. Store records:
Download the completed authorization with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Choose a signing method for authorizations
- Use the web app when staff need to upload the authorization, position fields, assign recipients, and monitor completion from a desktop workflow.
- Use the mobile app when clinicians or authorized representatives need to review and sign the patient-care authorization from an iOS or Android device.
- Use kiosk mode when patients complete authorizations at a staffed healthcare location using a shared device and controlled signing session.
- Use a shareable signing link when a known patient population needs access without separate email invitations, while retaining the signing record.
Recommended authorization workflow setup
Use controlled identity checks, traceable signatures, and retention aligned with the authorization’s healthcare record requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS authentication |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retain the complete signing history |
| Document retention | Keep six years for HIPAA records (45 CFR 164.530(j)) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
Security for patient authorizations
HIPAA protection:
Data encryption:
Transport security:
Security certification:
Information security:
Document history:
How signNow records authorization activity
The audit trail connects the patient authorization to signer identity, signing events, document history, and the retained completion record.
Identify signer:
Timestamp event:
Hash document:
Seal history:
Track actions:
Export evidence:
Privacy risks in patient authorizations
Including unrelated diagnoses or treatment details can expose more protected health information than the authorization’s stated purpose requires. A missing expiration date, recipient, or information scope can make the patient’s consent unclear for the requested disclosure. Sending the authorization to an incorrect email address can disclose patient information and undermine signer attribution. Leaving completed authorizations in personal inboxes or shared folders can bypass approved access controls and retention procedures.
Best practices for authorization records
Accurate scope, controlled access, and documented retention help healthcare teams handle patient authorizations consistently.
Confirm the authorization scope before sending
Assign patient and representative fields carefully
Export the signed record and audit trail
Restrict access to authorized healthcare staff



Troubleshoot patient authorization workflows
These answers address signer access, protected health information, plan capabilities, record evidence, and electronic-signature requirements for this authorization.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month with annual billing. Confirm that the selected plan and any invite usage fit the organization’s authorization volume before deployment.
HIPAA use requires signNow’s HIPAA-compliant configuration and a business associate agreement. Healthcare teams should confirm the BAA is in place before processing protected health information through the patient authorization workflow.
If the patient cannot open the signing request, verify the recipient email, resend the invitation, or use a controlled signing link. Do not forward patient information through an unapproved channel while troubleshooting delivery.
If fields are assigned incorrectly, correct the recipient assignment before sending. After sending, avoid altering the substantive authorization; void or restart the workflow according to internal document-control procedures.
signNow’s Business Premium plan includes bulk send, while Business does not list bulk send in the provided plan details. For repeated patient authorization campaigns, confirm the plan’s invite limits and workflow requirements first.
Electronic signatures generally receive legal recognition under ESIGN, 15 U.S.C. chapter 96, and applicable state law such as UETA. The organization must still preserve intent, consent, attribution, and reproducible records, and follow HIPAA requirements for protected health information.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.