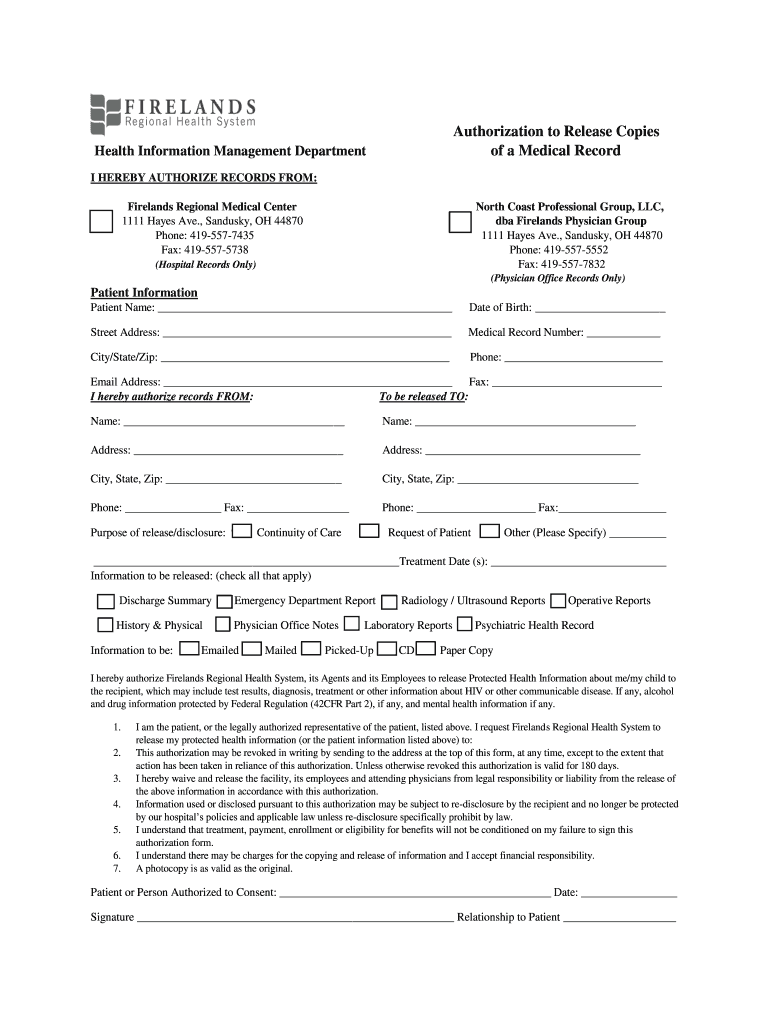
Medical Records Firelands Regional Medical Center Form
Use a Medical Records Firelands Regional Medical Center 0 template to make your document workflow more streamlined.
What the medical records form does
The Medical Records Firelands Regional Medical Center Form is a patient authorization used to request or disclose specified health information held by Firelands Regional Medical Center. It identifies the patient, recipient, records requested, purpose, delivery method, and authorization period. The signer reviews the scope, confirms consent, and signs the form; the medical center then handles the request under its records-release procedures and applicable privacy requirements. A completed form does not itself guarantee disclosure of every record or replace identity verification, provider review, or restrictions required by law.
Who uses the Firelands records form
Patients and representatives
Patients or their authorized representatives use the form to identify the records they want released, name the recipient, state the purpose, select a delivery method, and provide authorization. The signer should review every disclosure field before signing and retain a copy of the completed authorization.
Medical-records staff
Firelands release-of-information staff use the signed form to validate the request, check identity and authorization scope, route records to the named recipient, and preserve evidence of the transaction. Staff must still follow Firelands procedures, HIPAA requirements, and applicable state restrictions.
Teams that manage Firelands authorizations
A medical-records coordinator can maintain the approved Firelands authorization template, restrict editing rights, and send patient-specific requests without exposing unrelated records. Administrators can use role-based permissions to separate template management, sending, and completed-document access across the release-of-information workflow. A compliance administrator can review shared templates, delegated sending, and audit trails while preserving accountability for each patient request. signNow supports team administration and controlled access, but the organization must define which employees may view protected health information and signed authorizations.
Key features for Firelands authorizations
A focused workflow helps patients and medical-records teams complete, verify, and retain the Firelands authorization with fewer manual handoffs.
Structured authorization
Capture the patient’s identifying details, requested record categories, recipient, purpose, and authorization dates in one structured authorization workflow.
Guided signing
Place signature and date fields on the Firelands form so the patient can review the disclosure scope before signing.
Audit trail
Record signer identity, timestamps, IP information, and document events to support review of the completed authorization.
Access control
Use role-based access and controlled templates to limit who can view, send, or manage patient authorizations.
HIPAA safeguards
Protect signed medical-record authorizations with encryption in transit and at rest under signNow’s HIPAA program with a BAA.
Controlled delivery
Send the completed authorization to approved recipients or connected storage while preserving the final signed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the Firelands form workflow works
The signNow workflow moves the Firelands authorization from document preparation through patient signing and controlled record retention.
Upload form: Upload the current Firelands authorization Add fields: Place patient and recipient fields Send request: Send the authorization to the signer Archive record: Store the signed form with evidence
Ways to complete and sign the Firelands form
- Use the signNow web app to upload the Firelands authorization, place patient and recipient fields, review the disclosure scope, and send the request from a controlled workstation.
- Use the signNow mobile app when authorized staff or patients need to review and sign the Firelands form on an iOS or Android device.
- Use kiosk mode for supervised, in-person completion when the organization controls the device and verifies the patient before signing.
- Generate a shareable signing link only when the recipient and access controls are appropriate; avoid public distribution because the form contains sensitive health information.
Recommended setup for medical-record authorizations
Configure the Firelands authorization workflow around patient identity, limited disclosure scope, auditability, and protected health information.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for patient confirmation |
| Signature type | Electronic signature with explicit consent |
| Audit trail | Capture signer, timestamp, IP address, and actions |
| Document retention | Retain six years when HIPAA records apply |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
How the Firelands audit trail works
The audit trail preserves technical evidence around the patient’s authorization without replacing the form’s disclosure review.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Record actions:
Export evidence:
Security and data protection for health records
HIPAA compliance:
SOC 2 Type II:
ISO 27001:
AES-256 encryption:
TLS encryption:
ESIGN and UETA:



Best practices for this medical-record form
Use the Firelands form as a controlled disclosure authorization, not as a general-purpose signature page.
Verify every Firelands field after upload
Limit the disclosure scope before signing
Document electronic consent properly
Archive the authorization and audit trail
Privacy risks in the Firelands workflow
Patient identifiers or recipient information may be exposed when a completed Firelands authorization is emailed to the wrong address or stored without role-based access controls. A broad or incomplete description of requested records can create uncertainty about whether the patient consented to the specific disclosure. Missing electronic-record consent evidence can weaken the record when a patient later disputes the signing process under ESIGN’s consumer-disclosure requirements. A staff member may release records before confirming the signer’s identity, authorization scope, expiration terms, or any provider and state-law restrictions.
Troubleshooting Firelands medical-record requests
Resolve field, consent, authentication, privacy, and retention questions before releasing the completed Firelands authorization.
Upload the Firelands authorization as a PDF, then place fields over the patient, recipient, requested-record, purpose, and signature areas. signNow Business includes templates and audit trails; verify every field against the current medical center form before sending.
A patient may sign electronically when the transaction meets ESIGN and applicable state law requirements, with intent, consent, attribution, and record retention. For consumer-facing health records, provide the electronic-record disclosure required by 15 U.S.C. §7001(c).
HIPAA compliance requires the appropriate signNow configuration and a business associate agreement. The product ground truth states that signNow is HIPAA compliant with a BAA required; confirm the BAA before placing protected health information in the workflow.
Business Premium includes bulk send, but a medical-record authorization should use patient-specific data and recipients. Avoid bulk sending unless each request is independently reviewed, correctly addressed, and limited to the patient’s approved disclosure scope.
Use signNow’s audit trail to review signer identity, timestamps, IP information, and document actions. Export the completed authorization and its audit evidence together so the Firelands request record remains reproducible.
If the authorization covers a court order, family-law decree, will, or another excluded record, electronic signing may not resolve the underlying legal requirement. Apply the relevant state and federal rule before sending the document.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.