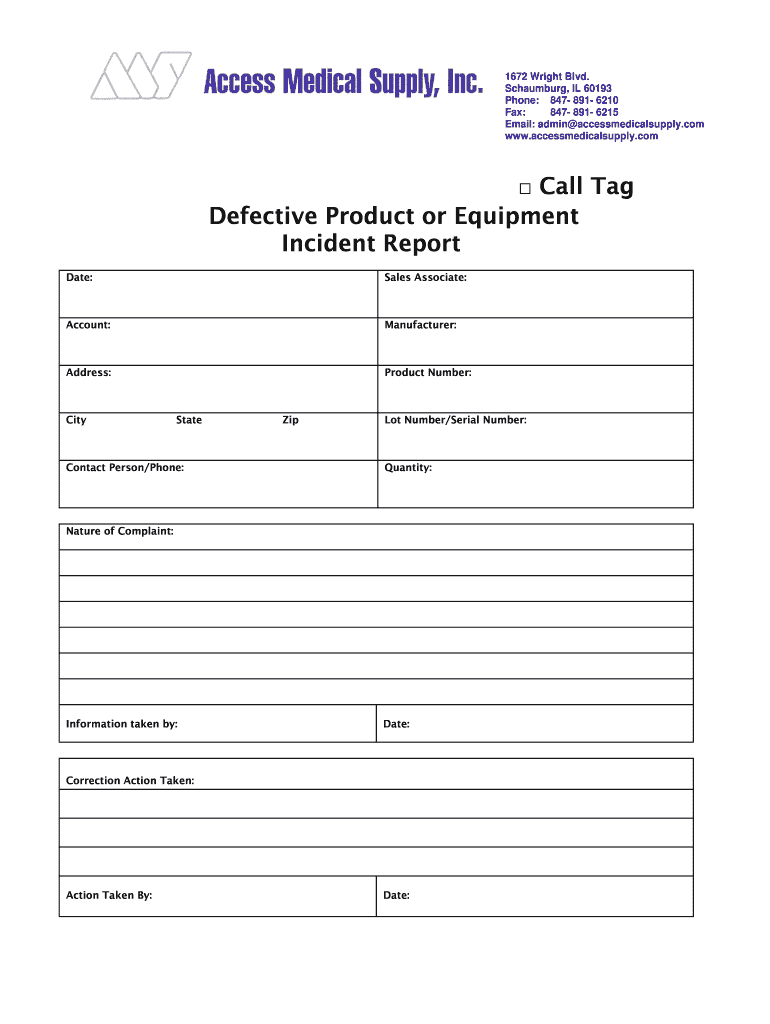
Product Incident Report Form
Use a Product Incident Report 0 template to make your document workflow more streamlined.
What the Product Incident Report Form records
A Product Incident Report Form records what happened, when it happened, which product or release was involved, and how the organization responded. Teams use it to capture the reporter’s identity, incident description, affected users or systems, evidence, business impact, containment actions, corrective measures, review notes, and approval signatures. With signNow, a sender uploads the form, reviews detected fillable fields, assigns fields to responsible participants, sends it for completion, and stores the signed record with an audit trail. The form supports investigation and accountability; it does not replace required agency or regulatory reporting.
Who completes this incident report
Product and quality teams
Product managers and quality teams use the form to document affected products, incident severity, customer impact, evidence, containment steps, root-cause findings, and approvals before closing an investigation.
Control and response teams
Support, security, compliance, and operations teams use the form to coordinate incident ownership, preserve review history, collect corrective-action signatures, and share an auditable record with authorized stakeholders.
Business types that use incident reports
The form fits organizations that need a documented chain from product event through investigation, approval, and corrective action.
A small software company can use the form to record a release-specific incident, assign an investigator, obtain product-owner approval, and preserve a signed corrective-action record without maintaining a paper routing process. A healthcare technology enterprise can route incident details through product, security, privacy, and compliance reviewers, while applying HIPAA controls when the report contains protected health information covered by a business associate agreement. A distributed manufacturing organization can standardize incident intake across plants, use shared templates, delegate sending to local operations, and retain consistent approvals for product-quality investigations across multiple locations.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the incident report workflow works
The signNow workflow keeps incident facts, assigned responsibilities, signatures, and completion evidence together.
Upload form: Upload the blank or partially completed Product Incident Report Form to signNow. Add details: Review auto-detected fields and add incident-specific text, dates, attachments, and signatures. Assign roles: Assign each field to the reporter, investigator, product owner, or approver. Complete record: Send, complete, sign, and store the final report with its audit trail.
What the incident audit trail records
The audit trail supplements the Product Incident Report Form by documenting who acted, when they acted, and how the final record was completed.
Signer authentication:
Timestamp capture:
Document history:
Completion sealing:
Action attribution:
Audit export:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Set up incident reporting securely
Configure the Product Incident Report Form around accurate reporting, controlled access, and reviewable records.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture signer actions and timestamps |
| Encryption and retention | TLS 1.2/1.3, AES-256, policy-controlled storage |
| User provisioning | Assign administrators, senders, and reviewers |
Features for product incident reporting
signNow connects the Product Incident Report Form’s factual intake, role-based review, electronic signatures, and completion evidence in one workflow.
Structured intake
Capture the incident date, product identifier, reporter, affected release, description, impact, and response details in one structured record.
Field detection
Auto-detected fillable fields help convert the uploaded Product Incident Report Form into an assigned digital workflow for each responsible participant.
Role-based routing
Route investigation findings and corrective actions to named reviewers so ownership remains visible throughout the report’s completion.
Electronic signatures
Collect electronic signatures from reporters, investigators, product owners, and approvers without requiring everyone to meet in person.
Audit trail
Record signer actions, timestamps, and document history so reviewers can examine how the completed incident report was finalized.
Record control
Keep the signed report and completion evidence together for authorized investigation, quality, compliance, or management review.
Security for incident records
Encryption:
Security report:
Information security:
Health information:
Electronic records:
Privacy controls:



Protect incident report privacy
Including names, contact details, screenshots, or device identifiers can expose personal information beyond the investigation team. A missing electronic-record consent disclosure can weaken the record when a consumer completes the incident report online. Broad folder permissions may let unrelated employees view incident narratives, attachments, or signed corrective-action approvals. Sending the completed report to external recipients without redaction can disclose confidential product, security, or customer information.
Best practices for this report
Accurate routing, controlled access, and preserved evidence make a Product Incident Report Form more useful during investigation and later review.
Verify incident facts before routing
Separate reporting from approval
Preserve the signed report and audit trail
Limit sensitive incident information
Processing the incident report
Processing time depends on investigation complexity, reviewer availability, and the evidence required for this product incident.
Document preparation
Delivery to signers
Signer turnaround
Completion and archival
Check legal limits before signing
Not required unless state law requires it
Excluded from ESIGN coverage
Court rules may require paper
State recording rules still apply
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting the incident report
These answers address field detection, plan selection, electronic-signature compliance, protected information, routing, and retention for this report.
Upload the Product Incident Report Form again as a clear PDF or supported document, then review signNow’s detected fields before assigning recipients. If fields are misplaced, add or adjust them manually so incident dates, descriptions, evidence references, and signatures map to the correct participants.
A signNow Business subscription includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, SOC 2, and GDPR support. Business Premium adds bulk send, kiosk mode, payments, and quick invite links; choose the plan based on the workflow required.
signNow supports ESIGN and UETA requirements for electronic records and signatures, including intent, consent, attribution, and record retention. For consumer-facing reporting, provide the required electronic-record disclosure under 15 U.S.C. §7001(c) before requesting a signature.
If the Product Incident Report Form contains protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm the organization’s BAA, access controls, retention policy, and permitted disclosures before routing the report.
Use signNow’s assigned fields and signer order to route the report from reporter to investigator, product owner, and approver. If a participant cannot sign, verify the recipient address, authentication method, and required fields before resending the invitation.
The completed report should remain associated with its audit trail and supporting evidence under the organization’s policy. If the record is an OSHA injury record, tax record, or another regulated record, apply that record class’s specific federal and state retention rule.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.