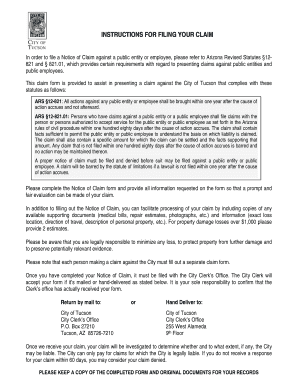
12 821 01 Authorization Of Claim Against Public Entity, Public Form
Use a 12 821 01 Authorization Of Claim Against Public Entity, Public template to make your document workflow more streamlined.
What this public-entity authorization does
12 821 01 Authorization Of Claim Against Public Entity, Public Form is an authorization document used with a claim against a public entity. It identifies the claimant or authorized representative, connects the signer’s approval to the claim, and provides a record for agency review. To complete it, confirm the claim details and receiving entity’s instructions, upload the form to signNow, place or verify fillable fields, route it to the authorized signer, and retain the signed copy with its audit trail. State filing rules, agency procedures, and any notarization requirement control final submission.
Features that support this claim form
signNow organizes the form-specific signing workflow, records completion evidence, and helps staff handle authorization documents without losing the original claim context.
Field placement
Upload the public-entity claim form and place signature, date, and required response fields without recreating the document.
Signer routing
Send the completed claim to the identified signer and preserve the signing sequence for internal review.
Audit trail
Capture signer identity, timestamps, actions, and document history in an audit trail connected to the completed form.
Record storage
Keep the signed authorization and completion record together so staff can retrieve the claim during agency correspondence.
Mobile signing
Use mobile apps to review and sign the claim when authorized staff work away from a desk.
Access control
Apply role-based access and stronger authentication when the claim includes sensitive claimant or incident information.
How to complete this claim authorization
Follow the public entity’s instructions first, then use signNow to prepare, route, sign, and preserve the authorization record.
Review the form:
Confirm the public entity, claimant, claim reference, and required supporting information. Upload and check:
Upload the form to signNow and verify detected fields against the original document. Add signer fields:
Assign signature, date, and required authorization fields to the correct signer. Send and monitor:
Send the authorization, monitor completion, and resolve any returned fields. Store evidence:
Download the signed form and audit trail for the agency record.
Recommended setup for this authorization
Configure the authorization workflow around signer identity, evidence preservation, access controls, and the public entity’s applicable records policy.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Use verified email with administrator-controlled roles |
| Signature type | Use an electronic signature showing signer intent |
| Audit trail | Retain timestamps, signer actions, and completion history |
| Document retention | Apply the public entity’s approved records schedule |
| Encryption | Use TLS 1.2 or TLS 1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Platform requirements for this public claim
To complete 12 821 01 Authorization Of Claim Against Public Entity, Public Form online, use Chrome, Firefox, Safari, or Edge with Windows, macOS, iOS, or Android. Browser connections should use TLS 1.2 or TLS 1.3. signNow mobile apps can support document review and signing where the workflow allows it.
Desktop browsers Use current Chrome, Firefox, Safari, or Edge on Windows or macOS. Mobile access Open the form on iOS or Android using a supported mobile browser. Secure connection Enable TLS 1.2 or TLS 1.3 for encrypted browser connections.
Government claims may contain personal, medical, or incident information, so use organization-managed Windows, macOS, iOS, or Android devices. Administrators should control access through signNow roles, review API or SSO requirements before deployment, and confirm whether the receiving public entity requires a particular signature, notarization, or filing method.



What the audit trail records
The audit trail adds evidence around the authorization itself, helping reviewers connect the signer, document actions, and completed claim record.
Authenticate signer:
Capture timestamp:
Log activity:
Seal record:
Link certificate:
Retrieve evidence:
Processing stages for the claim form
The form moves from factual preparation through signer review, completion evidence, and controlled archival; the receiving entity’s deadline remains controlling.
Prepare the claim
Deliver to signers
Collect signatures
Complete and archive
Privacy and disclosure pitfalls
Including unnecessary medical, financial, or identification details can expose personal information beyond the public entity’s stated claim requirements. Sending the authorization before confirming signer authority can leave the claim attached to an approval from the wrong person. Failing to capture electronic-consent evidence may weaken the record when a claimant later disputes signing intent. Sharing an unrestricted signing link can expose the authorization to an unintended signer or create attribution questions.
Record-keeping practices for this form
Preserve the authorization as a complete claim record, while allowing the public entity’s schedule and applicable state law to control retention.
Maintain one complete claim record
Follow the controlling records schedule
Export the audit trail
Secure the archived authorization
Security for the authorization record
Data in transit:
Stored document encryption:
Security certification:
Information security:
Electronic signatures:
Protected health data:
Rules that can limit electronic signing
Agency requirement
Filing restriction
Official filing
State procedure
Questions about this claim authorization
These answers address preparation, electronic signing, privacy, plan scope, and agency-specific filing requirements for 12 821 01 Authorization Of Claim Against Public Entity, Public Form.
Business plan includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR features. Its documented annual price is $8 per user per month, with 100 signature invites per user per year and overage fees. Confirm current plan terms before deployment.
A public-entity authorization may contain sensitive claimant information. signNow states that it is HIPAA compliant when a BAA is required, encrypts data in transit with TLS 1.2 or TLS 1.3, and encrypts stored data with AES-256. Apply the agency’s privacy rules separately.
Upload the original PDF, review signNow’s detected fields, and compare every field with the source form. Add only the claimant, authorization, date, and signature fields required by the public entity; do not substitute a generic release or claim form.
The signer should review the claim identity, authorization language, dates, and attachments before signing. If the public entity requires notarization, wet ink, or in-person delivery, electronic completion alone does not satisfy that separate requirement.
Business Premium includes bulk send, while the Business plan does not list bulk send in the supplied plan details. For one claim authorization, route the specific document to the named signer instead of using bulk distribution.
Export the signed authorization and audit trail after completion, then store them under the public entity’s approved records policy. ESIGN and UETA support qualifying electronic signatures, but the receiving agency’s filing and retention instructions still govern acceptance.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.