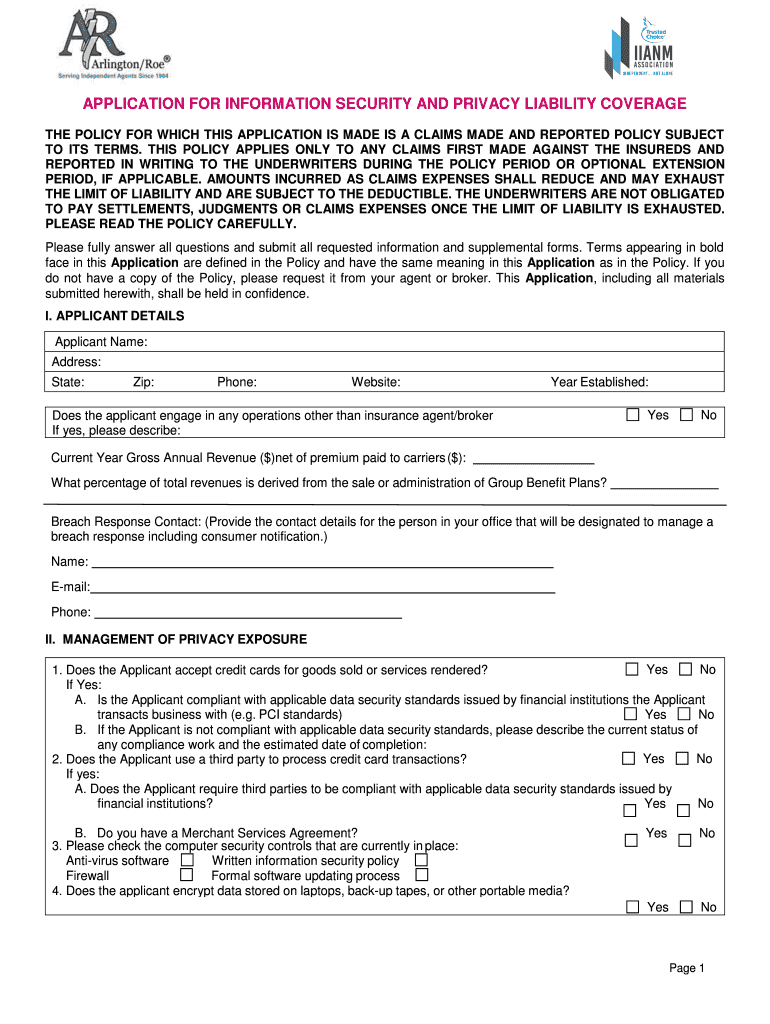
Beazley Application For Information Security, Privacy Liability
Use a Beazley Application For Information Security, Privacy Liability 0 template to make your document workflow more streamlined.
What the Beazley application is
The Beazley Application For Information Security, Privacy Liability is an insurance submission used to collect an organization’s information-security, privacy, technology, and liability details for review. It is completed by the applicant and authorized representatives, then provided with supporting materials to an insurer or broker. With signNow, a sender uploads the application, reviews detected fields, assigns signers, sends it electronically, and retains the signed document and audit trail. ESIGN and UETA can support eligible U.S. electronic transactions, but exclusions and state requirements still apply.
Who benefits from this application workflow
The application is most useful when insurance, privacy, technology, and risk teams must coordinate one signed submission.
Independent insurance brokers can prepare Beazley Application For Information Security, Privacy Liability submissions, collect client and authorized-representative signatures, and preserve the completed application with its audit trail. Cybersecurity consultancies can coordinate application reviews across underwriting, privacy, and technology teams while keeping delegated sending and reusable templates under administrative control. Enterprise risk departments can route applications through controlled approval workflows, apply stronger signer authentication, and retain completed records for underwriting governance and internal review.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this application and why
Insurance teams
Insurance brokers and applicants use the form for cybersecurity, privacy, technology, and risk disclosures requiring authorized review and signature.
Risk departments
Underwriters and enterprise risk groups use the signed application with supporting schedules to document submission history, approvals, and follow-up questions.
How the application workflow works
Prepare the Beazley application in signNow, verify its fields, route it to authorized participants, and preserve the completed record with its audit trail.
Upload document: Upload the Beazley application PDF and supporting schedules to signNow. Map fields: Review auto-detected fields and add missing application, date, and signature fields. Assign recipients: Assign each application section to the authorized signer or reviewer. Complete record: Send the completed package, capture signatures, and store the audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the application in four steps
Use this workflow to prepare the Beazley application, route it to authorized participants, and preserve a complete signed record.
Upload form:
Upload the Beazley application PDF to signNow. Check fields:
Review detected fields and add missing fields. Add signers:
Assign authorized applicants and representatives. Complete workflow:
Send, sign, download, and retain the record.
Features that support this application
signNow provides a structured way to prepare, route, sign, and retain the Beazley application while keeping review steps visible.
Field preparation
Upload the Beazley application PDF, review auto-detected fields, and add missing response, date, initials, or signature fields before sending the approved version.
Signer routing
Assign application sections to named recipients and control signing order so authorized applicants and representatives complete the document in the intended sequence.
Audit trail
Capture signer actions, timestamps, and document history in an audit trail that can accompany the completed application during underwriting or internal review.
Reusable templates
Reuse an approved Beazley application template while preserving controlled field placement and recipient roles for repeated insurance submissions.
Protected records
Keep application information protected with encryption in transit and at rest, supported by signNow’s security and compliance controls.
Business integrations
Connect the workflow with systems such as Salesforce, NetSuite, Google Drive, Box, or Procore when application data must move into approved business repositories.



Security controls for application records
TLS 1.2/1.3 and AES-256:
SOC 2 Type II:
ISO 27001 certified:
GDPR and CCPA:
HIPAA with required BAA:
WCAG 2.0 Level AA:
What the application audit trail records
The audit trail documents how the Beazley application was authenticated, completed, and preserved, rather than merely recording that a file was uploaded.
Authenticate signer:
Timestamp actions:
Record history:
Seal completion:
Attribute actions:
Export evidence:
Recommended setup for the application
Use a controlled signing workflow that protects application information, records signer intent, and preserves evidence for underwriting and governance.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS verification |
| Signature type | Electronic signature with signer intent |
| Audit trail | Export certificate of completion |
| Document retention | Follow policy and state requirements |
| Encryption | TLS in transit and AES-256 at rest |
Record-keeping practices for the application
Preserve the signed application as an auditable insurance record, while setting retention and access rules from the governing policy, contract, and applicable state requirements.
Set retention from the governing obligation
Export the completion record
Archive sensitive records securely
Review attachments before sending
Privacy and disclosure pitfalls
Sending a completed application to the wrong recipient can expose security questionnaires, privacy details, or incident information beyond the intended insurance and underwriting team. A signer may receive the application without a clear electronic-record disclosure or without access to the complete document, weakening evidence of informed consent under ESIGN. Shared accounts and broad folder permissions can let unauthorized personnel view application attachments, change templates, or download signed records without a documented business need. Unreviewed OCR field placement can move a signature or response field onto the wrong page, leaving important application questions unanswered or inaccurately completed.
Troubleshoot Beazley application issues
Resolve upload, signer, authentication, plan, legal-record, and retention questions before sending this insurance application for execution.
Upload the original Beazley application PDF again and confirm that each page renders before placing fields. signNow Business supports templates and audit trails, while OCR or auto-detection should be reviewed manually for text areas, checkboxes, and signature fields.
Check that every required signer has the correct email address and signing order. A signNow email invitation or signing link can deliver the application, but the sender should verify that the authorized insurance representative receives the intended document.
For sensitive application information, use stronger signer authentication where the account configuration supports it, such as SMS verification or advanced authentication. HIPAA compliance requires a BAA when protected health information is involved; the application itself does not create one.
signNow Business is listed at $8 per user per month with annual billing, and paid plans include 100 signature invites per user per year. Confirm current plan limits and overage terms before sending large application batches.
The signed application and audit trail can support evidence of intent, attribution, and record integrity under ESIGN and UETA when the transaction is eligible. Wills, court orders, and other ESIGN exceptions require separate legal handling.
Use signNow’s templates, role-based workflow controls, audit trails, and encrypted storage practices, then apply the retention period required by the governing insurance agreement or applicable state rule. Do not assume signNow’s storage period satisfies every legal obligation.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.