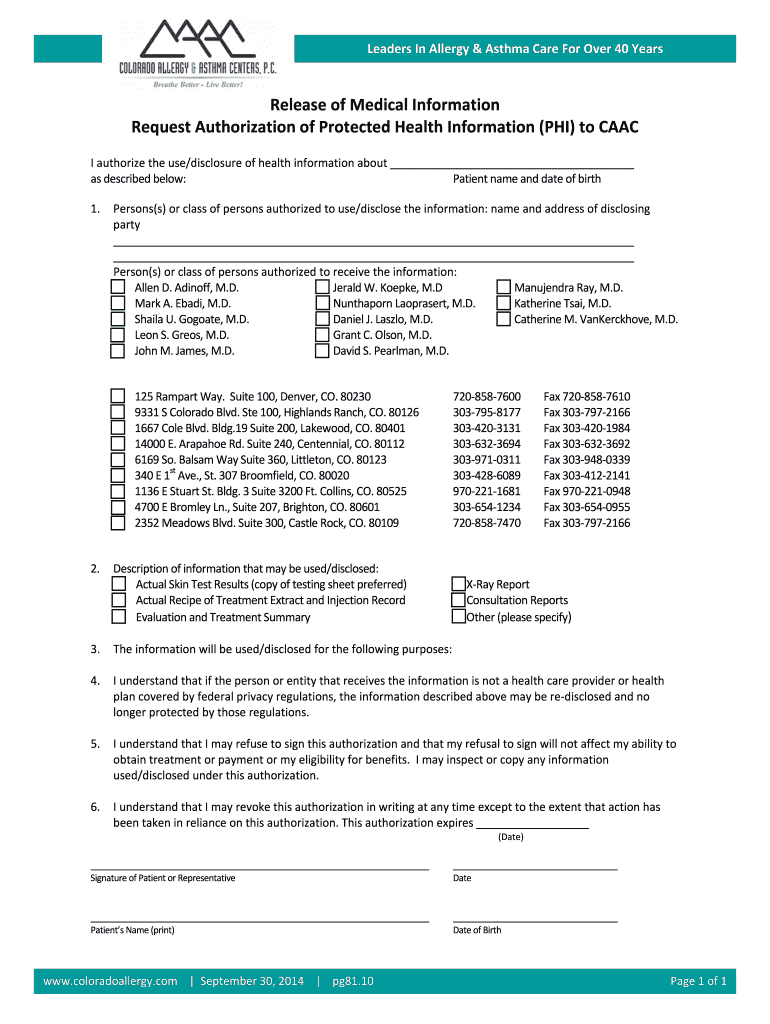
Release Of Medical Information Request Authorization Of
Use a Release Of Medical Information Request Authorization Of 0 template to make your document workflow more streamlined.
What this medical release authorization does
A Release Of Medical Information Request Authorization Of lets a patient authorize a healthcare provider to disclose specified medical records to a named recipient. The form usually identifies the patient, recipient, information categories, purpose, expiration date, and patient signature. With signNow, a sender uploads the authorization, places or confirms fields, sends it to the patient, and preserves the completed record with an audit trail. HIPAA governs permitted disclosures, while ESIGN and applicable state law may support electronic signing when consent and record-access requirements are satisfied.
Who uses this medical release authorization
Healthcare providers
Healthcare providers use the authorization to document a patient’s permission before sending designated records to another provider, insurer, attorney, employer, or personal representative. Staff can identify the recipient, purpose, information categories, and expiration before routing the form for signature.
Patients and representatives
Patients and authorized representatives review the requested disclosure, confirm the recipient and purpose, and sign the authorization. Records teams then compare the completed form against the requested medical information before releasing anything outside the stated scope.
Teams that manage medical authorizations
Healthcare records departments use shared signNow templates for patient, recipient, purpose, scope, and expiration fields. Administrators can control access while delegated staff send the authorization for signature, review the returned record, and archive the audit trail under HIPAA procedures. Fertility Centers of Illinois represents a healthcare use case for API-connected signing workflows. Its founder, John Butler, cited responsive support and a strong API, illustrating how a provider can connect authorization collection with operational systems without abandoning review and retention controls.
Features for signed medical release forms
signNow connects field preparation, patient signing, verification, and recordkeeping for a controlled Release Of Medical Information Request Authorization Of workflow.
Field detection
Upload the Release Of Medical Information Request Authorization Of and confirm detected fields for patient details, recipient information, disclosure purpose, expiration, and signature. This reduces manual setup while keeping the form’s disclosure scope visible for review.
Signer routing
Send the authorization directly to the patient or authorized representative for review and signature. signNow records delivery and signing events, helping the healthcare organization connect consent evidence with the specific medical-information request.
Signer verification
Use SMS-based signer authentication when the disclosure workflow requires more than an email link. Additional verification helps associate the completed authorization with the intended patient or representative before protected information is released.
Audit trail
Keep the signed authorization and completion evidence together. signNow audit trails record timestamps, actions, and signer events, supporting a defensible record of consent under HIPAA-oriented disclosure procedures.
Reusable template
Reuse an approved authorization template with fixed recipient, purpose, and expiration fields. Templates help records departments apply consistent language while allowing patient-specific details to remain controlled and reviewable.
Mobile completion
Complete the authorization on a desktop or mobile device, then retain the signed PDF and audit evidence. The workflow removes unnecessary paper handling without changing the provider’s responsibility to verify scope and identity.
How the authorization workflow works
The signNow workflow moves the authorization from upload through controlled signing and documented retention.
Upload document: Upload the Release Of Medical Information Request Authorization Of. Prepare fields: Auto-detect or place patient and disclosure fields. Route for signing: Send the authorization to its intended signer. Preserve evidence: Store the signed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete this authorization
Follow these steps to prepare, sign, and preserve a Release Of Medical Information Request Authorization Of.
Upload form:
Upload the provider-approved authorization template. Check details:
Confirm patient, recipient, scope, purpose, and expiration fields. Add signer:
Add the patient or representative as signer. Send securely:
Send through signNow for review and signature. Store record:
Download the signed form and audit trail.
Recommended workflow setup
Configure the authorization workflow around patient identity, disclosure scope, audit evidence, and HIPAA recordkeeping obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with completed authorization |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
Processing stages for medical release forms
Processing time depends on field preparation, signer access, identity checks, and the provider’s review before disclosure.
Prepare the authorization
Deliver to signer
Complete signer review
Archive completed record
Recordkeeping practices for medical authorizations
Accurate retention and controlled access help healthcare teams prove exactly what each authorization permitted.
Apply the six-year HIPAA retention rule
Export the completion record
Restrict disclosure workflow access
Archive scope and expiration details
What the audit trail records
The signNow audit trail documents signer activity and record integrity for the completed medical information authorization.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Track events:
Retrieve evidence:
Security for medical release authorizations
Health data protection:
Transport encryption:
Stored data encryption:
Security assurance:
Information security:
Signer authentication:



Privacy pitfalls in medical disclosures
Entering the wrong recipient can disclose protected health information to an unintended person or organization, even when the patient’s signature is valid. A missing expiration date, disclosure purpose, or information category can leave staff unable to determine whether the authorization covers the requested records. Sending a completed authorization through unsecured channels can expose patient identifiers, diagnoses, treatment details, or other protected health information. Overly broad access permissions can let staff view or download signed authorizations without a documented role in the disclosure process.
Platform requirements for medical authorizations
Use a current version of Chrome, Firefox, Safari, or Edge on Windows or macOS. Patients can review and sign the Release Of Medical Information Request Authorization Of through signNow mobile apps for iOS or Android.
Supported browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Mobile access signNow mobile apps available
Healthcare organizations should manage devices that access patient authorizations and configure signNow permissions according to internal policy. Enterprise deployments may require API access, SSO provisioning, and certificate or long-term validation configuration. Confirm browser updates, mobile controls, and BAA requirements before handling protected health information.
Legal standing of signed medical authorizations
A signed authorization can provide evidence of patient intent when the record shows consent, signer attribution, and reliable retention. ESIGN and UETA generally recognize qualifying electronic signatures, but they do not replace HIPAA disclosure requirements. Wills, family law decrees, court orders, and official court filings fall outside ESIGN’s ordinary scope.

Troubleshooting signed medical release forms
Resolve field, identity, plan, and compliance questions before releasing any protected medical information.
On the Business plan, upload the authorization and place required signature, date, patient, recipient, and disclosure-purpose fields manually or through field detection. Before sending, compare every field with the provider’s approved authorization language and confirm the expiration requirement.
HIPAA compliance requires a business associate agreement where applicable; signNow identifies HIPAA compliance as requiring a BAA. Confirm the healthcare organization’s agreement and internal safeguards before routing protected health information or related authorization records.
If the patient cannot access the email link, resend the invitation or use a verified signing link. Business Premium adds quick invite links, while SMS authentication can add an identity check when the organization’s policy requires it.
Business includes audit trails and templates, while Business Premium adds bulk send and kiosk mode. If the workflow needs advanced signer authentication, Enterprise adds that capability; plan availability should match the organization’s documented control requirements.
A completed authorization does not authorize every record automatically. Review the signed patient, recipient, purpose, information categories, expiration, and any revocation before releasing records; HIPAA’s disclosure requirements remain separate from the electronic-signature workflow.
ESIGN and UETA generally support electronic signatures when intent, consent, attribution, and record retention are demonstrated. Consumer-facing healthcare records also require the disclosures and access conditions in 15 U.S.C. §7001(c), subject to applicable exceptions and state law.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.