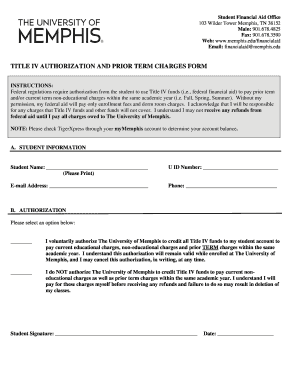
Title Iv Authorization Form University Of Memphis Memphis
Use a Title IV Authorization Form University Of Memphis Memphis 0 template to make your document workflow more streamlined.
What this University authorization form does
The Title IV Authorization Form University of Memphis is a student authorization document used to identify permitted access or communication concerning specified University records. The signer indicates who may receive information and may define the intended scope of disclosure. In a signNow workflow, staff upload the form, review detected fields, assign the student and recipient, collect signatures, and preserve the completed PDF with its audit trail. FERPA governs education-record disclosures; the University’s own instructions control required fields, recipients, and submission procedures.
Who uses this University authorization form
Students
Students use this University of Memphis authorization to identify which person or office may access specified education records, helping the institution document consent and limit disclosures under FERPA.
Authorized recipients
Parents, guardians, or designated representatives use the authorization when a student permits communication about selected academic, financial-aid, or enrollment information through an identified recipient.
Complete the University authorization online
Follow these steps to prepare, route, sign, and retain the Title IV authorization form for University of Memphis records access.
Upload form:
Upload the University of Memphis authorization PDF to signNow. Check fields:
Review detected fields and add missing consent, recipient, and signature fields. Add recipients:
Enter the student and authorized recipient email addresses. Send securely:
Send the authorization for review and signature. Archive record:
Store the completed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Audit trail for the authorization form
The audit trail records the technical events that connect the University authorization to its identified signers and completed document.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Export trail:
Features for this authorization workflow
signNow features can organize the University of Memphis authorization process from document preparation through consent capture, completion, and controlled record storage.
PDF preparation
Upload the University authorization PDF and prepare it without recreating the document’s original structure or consent language.
Field detection
Auto-detected fields help identify places requiring names, dates, consent selections, and signatures before sending.
Role-based routing
Route the authorization to the student and designated recipient using defined signing roles and order.
Audit trail
Capture signing events, timestamps, recipient actions, and completion evidence in an audit trail.
Reusable templates
Use templates for recurring University of Memphis authorization workflows while preserving required document language.
Mobile access
Access the authorization workflow through signNow web and mobile applications when approved by institutional policy.
Recommended authorization workflow setup
Configure the University of Memphis authorization workflow around verified recipients, documented consent, audit evidence, and the institution’s approved FERPA record schedule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with consent evidence |
| Audit trail | Enabled with completion certificate |
| Document retention | University policy and FERPA schedule |
| Encryption | TLS 1.2/1.3 and AES-256 |
Ways to send and sign the authorization
- Use the web app when staff prepare the University authorization, assign recipients, and review the completed record from an institutional workstation.
- Use the mobile app when an authorized student or recipient needs to review and sign the form from an iOS or Android device.
- Use kiosk mode when staff supervise in-person completion on an institution-managed device and need a controlled signing station.
- Use a shareable signing link when the institution’s approved workflow allows recipients to open the prepared authorization without a separate email invitation.



Legal standing and evidentiary value
A completed authorization can document student consent and the intended recipient, while ESIGN and UETA generally recognize electronic records when intent, attribution, consent, and reliable reproduction are established. FERPA requirements still control education-record disclosures, and exclusions such as wills, court orders, and family-law decrees require separate legal handling.

Key performance indicators that demonstrate SignNow's proven track record.
Questions about University authorization workflows
These answers address preparation, electronic consent, recipient control, security, field detection, and retention for the University of Memphis authorization form.
The Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures at $8 per user per month when billed annually. If bulk sending is required for multiple University recipients, Business Premium adds that feature at $15 per user per month annually.
A student may sign electronically when the institution’s process permits electronic consent and the signer demonstrates intent. ESIGN and UETA support electronic records, but FERPA disclosure authority and University policy still determine whether this authorization is sufficient.
Use signNow’s recipient fields and signing order to distinguish the student from an authorized recipient. Confirm every email address before sending, because the audit trail documents actions but cannot correct a disclosure sent to the wrong person.
For sensitive student information, configure stronger signer verification, such as two-factor authentication or SMS OTP, when permitted by the University’s workflow. HIPAA compliance is not a substitute for FERPA requirements unless protected health information is separately involved.
If a field is missing after upload, review signNow’s detected fields and add the required name, consent, date, or signature field manually. Do not change the University’s authorization language without institutional approval.
Completed records should be stored according to the University’s approved retention and access policy. Export the signed PDF and audit trail when required, then restrict access to personnel with a documented educational or administrative need.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.