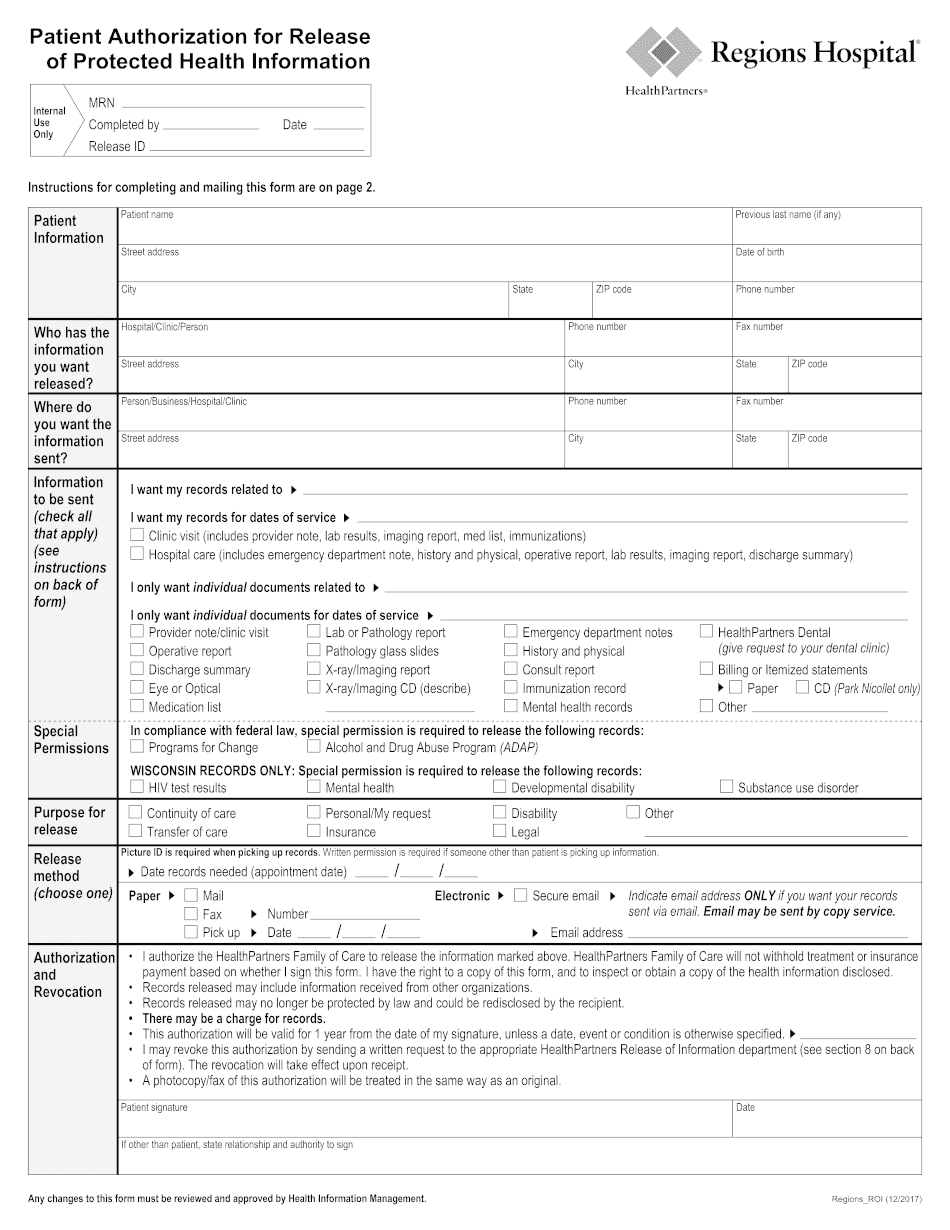
Patient Authorization For Release Of Protected Health Informationregions Hospital
Use a Patient Authorization For Release Of Protected Health InformationRegions Hospital template to make your document workflow more streamlined.
What this hospital authorization does
A Patient Authorization For Release Of Protected Health Informationregions Hospital is a permission record that identifies a patient’s approval for a hospital to disclose specified protected health information to an identified recipient. The patient or authorized representative reviews the requested scope, purpose, and applicable expiration terms, then signs the document. A hospital release team verifies completeness and authority before disclosure. With signNow, staff upload the authorization, review detected fillable fields, send it for signature, and retain the completed document and audit trail under HIPAA procedures.
How this authorization works in signNow
The hospital’s release team can move this authorization from upload to signed, auditable retention in four controlled steps.
Upload form: Upload the hospital authorization into signNow. Check fields: Review auto-detected fields and add signatures. Send request: Send the authorization to the patient or representative. Retain evidence: Store the signed form with its audit trail.
Recommended authorization workflow setup
Use a controlled configuration for patient identity, electronic signing, audit evidence, retention, and protected information handling.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with audit evidence |
| Audit trail | Capture timestamps, actions, and signer identity |
| Document retention | 6 years under HIPAA 45 CFR §164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 |
Features for patient release forms
signNow combines document preparation, remote signing, audit evidence, and controlled storage for hospital teams processing patient release authorizations.
Document preparation
Upload the hospital authorization, identify its fillable areas, and prepare signature fields without recreating the document manually. The completed file preserves the patient’s entered information and signing sequence.
Remote signing
Send the authorization to the patient or representative by email or signing link. signNow records delivery and completion events, giving release-of-information staff a clearer status view.
Audit evidence
Capture signer authentication, timestamps, and document actions in an audit trail. Staff can associate the evidence with the authorization before releasing protected health information.
HIPAA workflow
Apply signNow’s HIPAA compliance framework with a required BAA for covered workflows. Hospitals still control authorization review, workforce access, and disclosure decisions.
Reusable template
Use templates for recurring hospital authorization requests while keeping recipient, purpose, and information-scope fields reviewable for each patient-specific disclosure.
Connected storage
Connect completed authorizations with systems such as Box, Egnyte, Google Drive, or AWS for controlled storage and downstream records management.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for protected health information
Privacy framework:
Control reporting:
Security certification:
Stored data:
Data in transit:
Electronic signatures:
How signNow records this authorization
The signNow audit trail documents identity, timing, document integrity, and retrieval evidence for this patient authorization workflow.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:



Privacy pitfalls in patient releases
Sending the authorization to the wrong patient or representative can expose protected health information and undermine the hospital’s disclosure review. Leaving the recipient, purpose, information scope, or expiration unclear can make the authorization unsuitable for the requested release. Storing signed authorizations in unrestricted email or shared folders can give unauthorized workforce members access to protected health information. Releasing records before confirming the signature, representative authority, and authorization status can create a preventable disclosure-control failure.
Rollout and retention for hospital releases
A hospital can move from document preparation to signed-record retention while keeping authorization review and HIPAA documentation requirements visible.
Prepare document:
Send for signature:
Complete signing:
Retain six years:
Export evidence:
Restrict access:
Review expiration:
Apply longer rules:
Legal standing of electronic authorization
A signed Patient Authorization For Release Of Protected Health Information can provide reproducible evidence of patient intent when identity, consent, attribution, and record retention are established. ESIGN and UETA generally recognize electronic signatures, while HIPAA privacy procedures and any applicable state law still govern whether the hospital may disclose the specified information.

Who benefits from this authorization workflow
The workflow is useful wherever a healthcare organization must collect, verify, and retain patient permission before a defined disclosure.
Solo medical practices can send patient release authorizations remotely, reducing paper handling while retaining a completed form and audit trail for each disclosure request. Hospital release-of-information departments can reuse reviewed templates, route signatures to patients or representatives, and coordinate authorization evidence before sharing protected health information. Healthcare enterprises can connect signNow with storage and operational systems, apply role-based access practices, and standardize signed authorization retention across multiple facilities.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting this hospital authorization
These answers address the signing, privacy, plan, and evidence questions that arise when hospitals process this authorization through signNow.
signNow’s HIPAA compliance requires a business associate agreement for covered workflows. Confirm that the hospital’s signNow arrangement includes the required BAA before routing protected health information, then limit access through organizational controls and documented release procedures.
The signNow Business plan includes audit trails and templates, while Business Premium adds bulk send and kiosk mode. Select a plan based on the hospital’s volume and signing method; verify any HIPAA-specific add-on or configuration before deployment.
If a patient cannot open the signing link, verify the recipient address, resend the invitation, and offer a supported browser or mobile app. Do not forward the document through unsecured email when it contains protected health information.
A missing patient or representative signature means the authorization is incomplete for the hospital’s release process. Return the document for completion, verify representative authority, and retain the declined or incomplete event according to policy.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record reproducibility are established. For consumer-facing records, apply the electronic-record disclosure requirements in 15 U.S.C. §7001(c) and preserve the completed record.
Use signNow’s audit trail to review authentication, timestamps, actions, and the completed file. Export the evidence when closing the release request, then preserve it with the authorization under HIPAA’s six-year documentation rule in 45 CFR §164.530(j).
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.