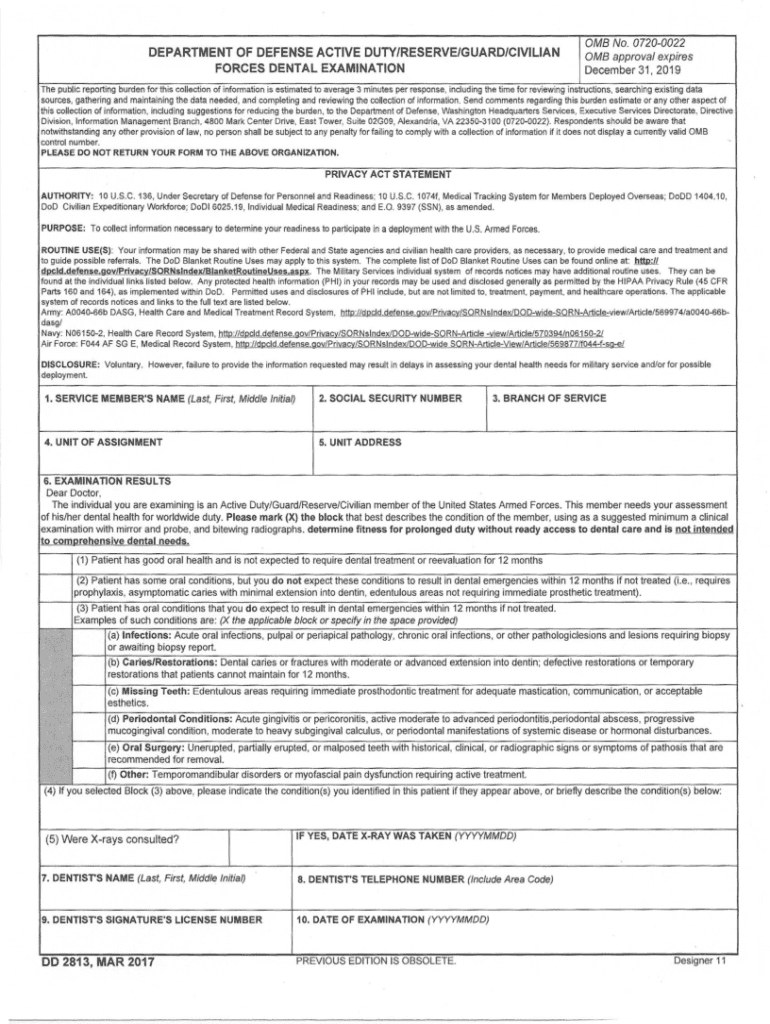
DD2813 Form
Use a Dd2813 template to make your document workflow more streamlined.
What the DD2813 Form does
The DD2813 Form is a Department of Defense dental examination record used to document a service member’s dental evaluation and related readiness information. In practice, the form captures identifying details, examination findings, examiner information, dates, and required signatures for review by an authorized military or medical organization. With signNow, a prepared DD2813 Form can be uploaded, its fillable fields detected, routed to designated signers, and stored with a completion record and audit trail. The receiving organization remains responsible for confirming current DoD instructions and acceptance requirements.
Features for completing DD2813
The workflow focuses on accurate field completion, authorized signatures, traceable routing, and preservation of the completed DD2813 Form record.
Field preparation
Upload a prepared DD2813 Form and identify its fillable areas before routing it to the appropriate examiner or reviewer, reducing manual field placement.
Role-based fields
Assign each DD2813 Form field to the correct participant so identifying information, examination results, dates, and signatures are completed by the responsible person.
Controlled routing
Route the form electronically to designated signers instead of coordinating paper copies, while preserving the signing sequence required by the receiving organization.
Audit trail
Capture signer actions, timestamps, and document events in an audit trail that accompanies the completed DD2813 Form for later review.
Mobile access
Use signNow mobile apps when authorized personnel need to review or sign the DD2813 Form away from a desktop workstation.
Record retrieval
Store the completed form and transaction evidence in a controlled repository, supporting retrieval when dental readiness records must be reviewed.
Complete DD2813 Form in signNow
Use this sequence to prepare, route, sign, and preserve a completed DD2813 Form without losing its transaction evidence.
Upload form:
Upload the prepared DD2813 Form to signNow. Check fields:
Review detected fields and correct their assignments. Add signers:
Add authorized recipients and signing order. Send form:
Send the form through the approved workflow. Verify completion:
Review signatures, dates, and completed entries. Store record:
Download and store the form with its audit trail.
Recommended DD2813 workflow setup
Configure the workflow around authorized identity checks, traceable signatures, protected transmission, and the retention policy governing DD2813 records.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Follow DoD and records policy |
| Encryption | TLS in transit and AES-256 at rest |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the DD2813 audit trail works
A signNow audit trail connects signer identity, document integrity, and recorded events so completed DD2813 Form activity can be reviewed later.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
Verify DD2813 signers securely
Email authentication:
SMS authentication:
ID verification:
PKI certificates:
X.509 identity:
Two-factor authentication:
Retain DD2813 records with control
Record custodians should preserve the completed DD2813 Form, audit evidence, and access history under the rule that governs the record.
Apply the controlling retention rule
Export the completed evidence package
Limit access to authorized personnel
Record disposition decisions clearly
Challenges when completing DD2813
Entering a service member’s identifying or dental information in the wrong field can create an inaccurate readiness record requiring correction and review. A missing examiner signature, date, or required acknowledgment can delay acceptance of the DD2813 Form by the receiving organization. Sending the completed form to an unauthorized recipient can expose protected health information and trigger access-control or privacy review. Saving the signed form without its audit history can make later verification of signer identity, timing, and document integrity more difficult.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Platform requirements for DD2813
Use a current version of Chrome, Firefox, Safari, or Edge on Windows or macOS to upload, review, and route the DD2813 Form. signNow also provides mobile apps for iOS and Android, allowing authorized users to access signing tasks from supported devices.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop systems Mobile apps iOS and Android mobile apps
Organizations should manage access through approved devices, user permissions, and storage controls. Confirm mobile use, offline behavior, API access, SSO provisioning, and any certificate configuration with the organization’s signNow administrator before handling DD2813 records containing protected health information.
DD2813 Form troubleshooting
These answers address field assignment, signer verification, audit evidence, protected health information, electronic consent, and corrections for DD2813 workflows.
Upload the DD2813 Form to signNow, review the detected fillable fields, and manually correct assignments before sending. The Business plan includes templates and audit trails, helping preserve a repeatable preparation process for authorized staff.
Use signNow’s signer authentication options, including SMS OTP where configured, and confirm the recipient’s identity before signing. ESIGN and UETA require intent, attribution, and a retained reproducible record; authentication strength should match organizational policy.
The Business plan includes audit trails, while stronger controls may require a configured enterprise arrangement. Preserve the completed document and audit history together, then confirm the receiving organization accepts electronic records under its policy.
A DD2813 Form may contain health information. signNow identifies HIPAA compliance as requiring a BAA; confirm that the applicable account configuration, users, and storage process meet your organization’s HIPAA obligations before routing PHI.
For consumer-facing electronic records, ESIGN, 15 U.S.C. §7001(c), requires disclosure of the right to paper records, electronic-access capability, and consent-withdrawal procedures. Apply that rule when the transaction involves a consumer rather than assuming every signer has identical obligations.
If a signature or date is missing, reopen the workflow only through the approved correction process and document the change. Do not alter a completed record outside signNow, because the audit trail should explain the final DD2813 transaction history.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.