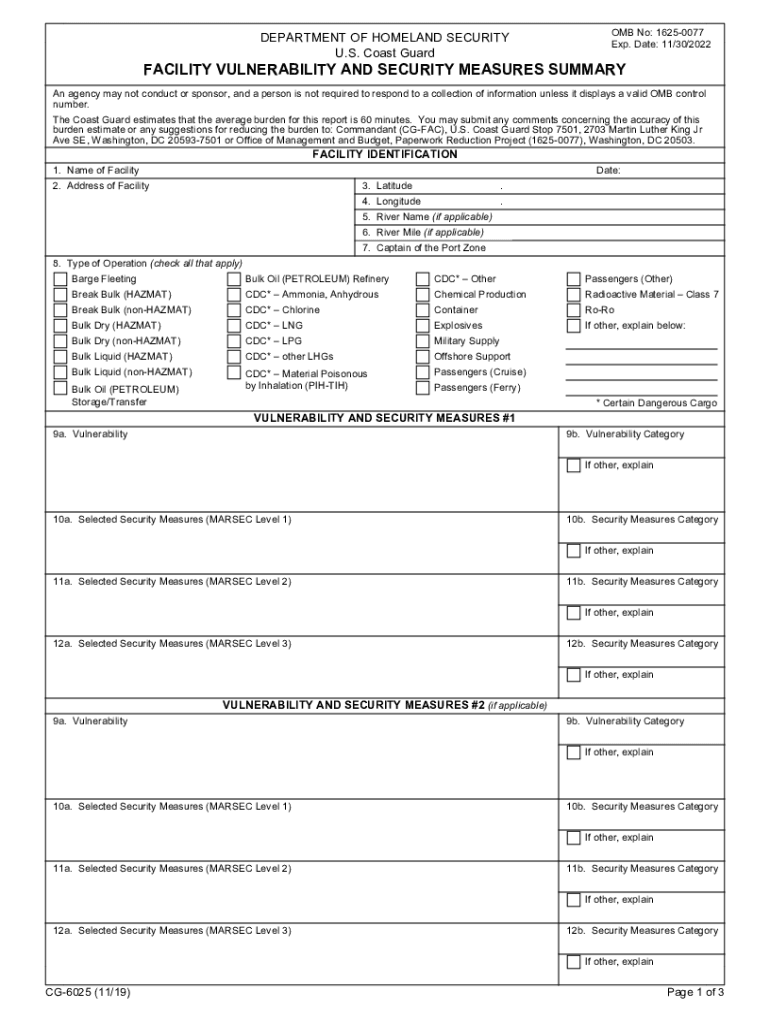
Form Cg 6025 Facility Vulnerability And Security Measures Summary
Use a Form CG 6025 Facility Vulnerability And Security Measures Summary template to make your document workflow more streamlined.
What the CG 6025 summary documents
Form CG 6025 Facility Vulnerability And Security Measures Summary is a facility-security record that organizes information about vulnerabilities and the measures used to address them. It is completed by entering site-specific security information, reviewing the entries with authorized personnel, and obtaining required signatures. In signNow, the workflow begins by uploading the form, detecting or placing fillable fields, assigning reviewers, and sending signature requests. The completed PDF and audit trail can then be stored under the organization’s records policy. The issuing agency, filing deadline, and retention period should be confirmed from the applicable program instructions or contract.
Who uses the CG 6025 summary
Security teams
Facility security personnel use the summary to document vulnerability findings, protective measures, access controls, and corrective actions for a specific site.
Facility administrators
Government, transportation, and regulated facility administrators use the signed record to coordinate reviews, approvals, and secure retention.
Complete the CG 6025 summary online
Use signNow to prepare the Facility Vulnerability And Security Measures Summary, route required approvals, and preserve the completed record.
Upload form:
Upload the completed CG 6025 summary PDF to signNow. Check fields:
Review detected fields and add missing signer, date, or initials fields. Assign signers:
Assign the summary to the facility representative and security reviewer. Send and store:
Send the form, monitor completion, and save the signed copy.
Features for the CG 6025 workflow
The workflow connects the CG 6025 facility summary with field review, signer assignment, audit evidence, and controlled record storage.
Centralized summary
A structured vulnerability summary keeps facility conditions, security measures, and review decisions together instead of scattering them across separate emails and attachments.
Field detection
Detected fields help convert an existing CG 6025 PDF into a signable workflow while preserving the form’s original structure and wording.
Role assignment
Assigned roles clarify who reviews facility information, who signs the summary, and who receives the completed record.
Audit trail
The audit trail records signer actions, timestamps, and document events, giving reviewers a traceable history for the completed summary.
Mobile review
Mobile access lets authorized personnel review or sign the CG 6025 summary from a controlled desktop or mobile workflow.
Secure storage
Secure storage keeps the signed summary and completion evidence available for later internal review or compliance-related inquiries.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended CG 6025 workflow setup
Configure the workflow around authorized facility reviewers, documented signer identity, audit evidence, and the organization’s approved records policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Export completion evidence with signed PDF |
| Document retention | Apply the facility’s approved retention schedule |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
What the CG 6025 audit trail records
The audit trail documents technical events around the Facility Vulnerability And Security Measures Summary, from signer authentication through retrieval of completion evidence.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper sealing:
Event logging:
Audit export:
Signer authentication for CG 6025
PKI:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signing evidence:
Platform requirements for CG 6025
The CG 6025 workflow can be prepared and signed through supported browsers using Windows or macOS, with mobile access available through iOS and Android applications.
Supported browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile systems iOS and Android mobile access
Organizations should use managed devices, current browser security settings, and controlled access for facility vulnerability information. Enterprise teams may also configure SSO, API access, and approved storage integrations according to internal security policy.
Challenges when preparing the summary
Leaving facility identifiers, vulnerability descriptions, or mitigation details incomplete can prevent reviewers from evaluating the security summary accurately. Assigning the wrong signer can delay approval because the person receiving the request may lack authority over facility security measures. Uploading an outdated CG 6025 version can create inconsistencies between the signed summary and the facility’s current vulnerability assessment. Sharing the completed summary without access controls may expose sensitive facility security information to unauthorized recipients.
Best practices for CG 6025 records
Accurate facility details, restricted access, complete audit evidence, and an identified governing records rule make the signed summary easier to review and defend.
Verify every facility detail
Restrict sensitive access
Preserve completion evidence
Confirm the governing retention rule
Legal value of the signed summary
A completed CG 6025 summary can provide an organized record of facility vulnerability information and signer actions. For U.S. electronic transactions, ESIGN and applicable state law such as UETA generally recognize electronic signatures when intent, consent, attribution, and record retention requirements are satisfied.

CG 6025 processing and completion stages
The form’s actual deadline depends on the governing facility program or request; signNow tracks workflow progress but does not establish that deadline.
Document preparation
Delivery to signers
Signer turnaround
Completion and archival
CG 6025 troubleshooting questions
These answers address field detection, signer routing, authentication, audit evidence, plan selection, and compliance classification for the Facility Vulnerability And Security Measures Summary.
Upload the original CG 6025 PDF again and confirm that required fields were not flattened or removed before sending. signNow can detect fillable fields, while missing fields may need manual placement and assignment.
Check that each recipient has the correct email address and assigned role, then resend the request if necessary. Business includes templates and audit trails, but signer routing still depends on accurate workflow assignments.
Use SMS OTP or another configured authentication method when facility policy requires stronger signer verification. signNow supports two-factor authentication options, while the organization must decide which control the CG 6025 workflow requires.
Review the completed PDF and audit trail together. signNow records timestamps and document events, but the organization should confirm that the signed summary contains every required vulnerability and security-measure entry.
Business is listed at $8 per user per month when billed annually; month-to-month pricing is $20 per user per month. Business Premium adds bulk send, while Enterprise adds advanced signer authentication and integrations.
HIPAA compliance requires a BAA when protected health information is involved. A facility-security summary should not be treated as HIPAA-covered merely because it is signed electronically; classify the information and apply the correct compliance policy.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.