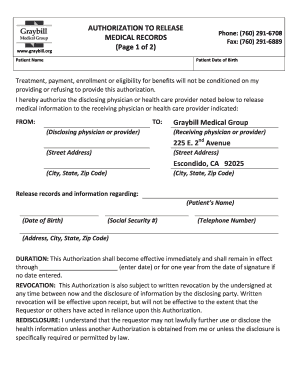
Medical Records Release To Graybill Graybill Form
Use a Medical Records Release To Graybill FILLABLE Graybill template to make your document workflow more streamlined.
What the Graybill medical release form does
The Medical Records Release To Graybill Graybill Form is a written authorization allowing Graybill to disclose specified medical information to an identified recipient. The person completing it reviews the patient details, recipient, records or date range covered, purpose, and authorization terms before signing. A complete authorization helps Graybill determine what may be released and to whom. With signNow, a sender uploads the form, places or confirms fields, sends it to the signer, and stores the completed document with its audit trail. HIPAA requirements and applicable state law still govern disclosure.
Who completes and uses this release
Patients and representatives
Patients or their legally authorized representatives use the release to permit Graybill to send defined medical records to another provider, insurer, attorney, or organization. They should limit the scope and recipient carefully, confirm the purpose, and review any expiration or revocation language before signing.
Healthcare organizations
Graybill staff, receiving providers, insurers, and attorneys use the completed authorization to document permitted disclosure. They can route the signed release with related records while limiting access to personnel involved in the request and following HIPAA privacy procedures.
Organizations that use Graybill releases
The form is most useful wherever a patient’s authorization must connect Graybill records with a named recipient and defined disclosure purpose.
A solo medical practice can use the Graybill release template to collect a patient’s authorization, identify the receiving party, and preserve the completed document before responding to a records request. A multi-provider healthcare organization can route releases through designated staff, use role-based access, and retain audit evidence while limiting disclosure to the approved recipient and record scope. A health-plan or legal-services team can receive signed authorizations through controlled workflows, verify the stated purpose, and coordinate records requests without treating the electronic signature as permission beyond the form.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to complete the Graybill release
Use this sequence to prepare, sign, and retain the Medical Records Release To Graybill Graybill Form in signNow.
Upload form:
Upload the Graybill release PDF to signNow. Check fields:
Review detected fields and add missing fields. Assign signer:
Enter the patient or representative as signer. Send request:
Send the authorization and monitor completion. Store records:
Download the signed release and audit trail.
Ways to send and sign the release
- Use the signNow web app when staff need to upload the Graybill PDF, review fields, assign recipients, and manage the completed authorization from a desktop workspace.
- Use the signNow mobile app when a patient or representative must review and sign the Graybill release from an iOS or Android device.
- Use kiosk mode for supervised, in-person completion when staff control the device and verify the signer before the authorization is submitted.
- Use a shareable signing link when a controlled distribution channel is appropriate, confirming the recipient’s identity before granting access to the medical-records release.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended release-form workflow settings
Configure the Graybill release around signer identity, limited disclosure scope, audit evidence, and HIPAA-related retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for external signers |
| Signature type | Electronic signature with signer intent |
| Audit trail | Export the completion certificate |
| Document retention | 6 years for HIPAA records under 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
What the Graybill audit trail records
After signing, signNow records technical evidence that helps staff review how the Graybill authorization was completed and preserved.
Verify signer:
Capture time:
Record document:
Seal record:
Link evidence:
Export trail:
Authentication and signing security
PKI signatures:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit evidence:
Mobile options for Graybill releases
The signNow workflow supports the signNow iOS and Android apps for reviewing, completing, and signing the Graybill release away from a desktop.
Mobile apps iOS and Android signNow apps Offline signing Offline signing available in app Camera capture Camera captures paper records
Mobile users should verify the patient and recipient details on the device before signing. Organizations handling protected health information should use managed devices, apply access controls, and confirm that their signNow configuration and BAA support the intended HIPAA workflow.
Best practices for Graybill authorizations
Careful field review, limited disclosure, preserved audit evidence, and a documented retention policy reduce errors when processing this medical-records release.
Review every authorization field
Preserve signing evidence
Match disclosure to authorization
Apply the six-year HIPAA rule
Retention periods for related records
Apply the rule matching the record category; a Graybill authorization itself does not automatically create every listed obligation. Confirm state and organization-specific requirements before deletion.
Six years HIPAA documentation
Three years federal tax
Six years tax understatement
Three years payroll records
Five years OSHA injuries
Privacy pitfalls to check before disclosure
Sending the release to an unintended recipient can disclose protected health information beyond the patient’s stated authorization. Leaving the record scope or purpose vague can make it difficult to determine whether a requested disclosure is authorized. Missing signer identity or consent evidence can weaken the organization’s ability to demonstrate valid authorization during a privacy review. Giving broad staff access to completed releases can expose patient information unnecessarily and undermine role-based privacy controls.
Legal standing of the authorization
An electronic Graybill medical-records authorization can provide evidence of intent, consent, signer identity, and record integrity when executed and retained under ESIGN, UETA, HIPAA, and applicable state law. It does not replace special formalities for wills, certain court orders, family-law decrees, or other excluded records.

Graybill release troubleshooting questions
Resolve the named signing, privacy, and document-handling issues before releasing medical information through the Graybill authorization.
Upload the original Graybill PDF again and check that it opens without password protection. In signNow, confirm detected fields before sending, then add missing patient, recipient, date, or signature fields manually. A clean source file prevents incomplete authorization data.
Use signNow’s signer authentication options, including SMS OTP where appropriate, and verify the recipient’s phone number before sending. For HIPAA-covered information, confirm that your organization has the required signNow BAA and follows its access-control procedures.
A Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps. Business Premium adds bulk send and kiosk mode. Choose Enterprise when advanced signer authentication or conditional and formula fields are needed for your workflow.
Limit the authorization to the records, purpose, recipient, and dates the patient approved. HIPAA requires appropriate privacy safeguards, while state law may impose additional authorization rules. Have compliance counsel review unusual requests or sensitive categories before disclosure.
The sender can export signNow’s audit trail and completion certificate after signing. Preserve them with the final Graybill release and restrict access to authorized personnel. The audit record supports evidence of signing but does not expand the authorization’s permitted scope.
If a signer cannot open the request, resend it after confirming the email address and checking the signing link. signNow can send through email or a shareable signing link; use SMS authentication only after confirming the signer’s phone number.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.