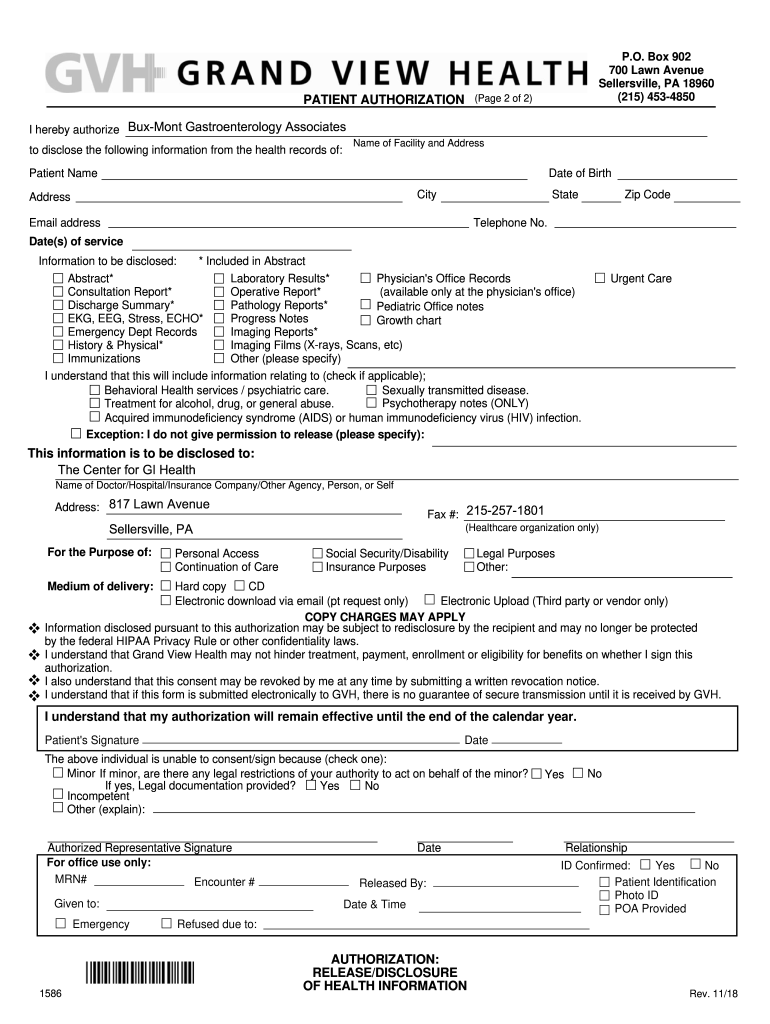
Patient Instructions For Patient Authorization For Release Form
Use a PATIENT INSTRUCTIONS FOR PATIENT AUTHORIZATION FOR RELEASE template to make your document workflow more streamlined.
What this patient authorization form does
The Patient Instructions For Patient Authorization For Release Form records a patient’s permission to disclose specified health information to a named recipient. The patient identifies the requested records, recipient, purpose, expiration, and signature details before release. Healthcare organizations should use the completed authorization according to HIPAA and applicable state privacy law. With signNow, staff can upload the form, auto-detect fillable fields, route it to the patient, capture the signature and audit trail, and store the completed record for controlled retrieval.
Who uses this patient release form
Healthcare providers
Medical practices use the form to obtain patient permission before releasing records to another provider, insurer, attorney, or designated individual.
Patients and representatives
Patients and authorized representatives identify requested records, recipient, purpose, expiration, and signature information before a covered entity discloses protected health information.
Features for patient release authorizations
signNow organizes the exact fields, signatures, access controls, and records needed to process this patient authorization form consistently.
Field detection
Upload the patient authorization form and let signNow identify fillable areas, reducing manual field placement before sending it to the patient.
Patient routing
Route the release authorization to the patient by email, then capture the completed signature and signing activity in one record.
Required information
Use required fields for recipient, purpose, requested records, expiration, and signature so incomplete authorizations are easier to identify.
Audit trail
Keep the signed authorization and certificate of completion together, giving records staff a clearer evidence trail for each disclosure request.
HIPAA controls
Apply HIPAA-compliant workflows with a BAA when the authorization contains protected health information and the healthcare organization requires covered-entity safeguards.
Reusable templates
Use reusable templates for recurring release requests while limiting editing and sending permissions to authorized healthcare staff.
How to complete the patient authorization
Use this sequence to prepare, sign, and retain the Patient Instructions For Patient Authorization For Release Form in signNow.
Upload form:
Upload the blank authorization PDF. Review fields:
Confirm detected fields and add missing recipient, purpose, and expiration fields. Assign signer:
Assign the patient signature and required initials. Send securely:
Send the authorization through signNow. Archive record:
Store the signed copy and audit trail.
Recommended authorization workflow setup
Configure authentication, signing, audit evidence, retention, and encryption around the patient release workflow and applicable HIPAA obligations.
| Setting | Recommendation |
|---|---|
| Patient authentication method | Email verification with SMS code |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable certificate of completion |
| Document retention | Retain six years for HIPAA records |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.



Privacy and disclosure pitfalls to avoid
Including an overly broad record description can disclose more protected health information than the patient intended to authorize. Omitting the recipient, purpose, expiration date, or signature can make the authorization incomplete for the requested release. Sending the signed authorization through an uncontrolled channel can expose patient data outside the approved care or records workflow. Allowing staff to access every signed release increases disclosure risk when role-based permissions are not configured.
What the authorization audit trail records
The audit trail documents identity, timing, document integrity, and retrieval evidence after a patient completes the release authorization.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Track activity:
Retrieve evidence:
Platform requirements for patient signing
Patients can review the authorization form in Chrome, Firefox, Safari, or Edge on Windows 10, Windows 11, or macOS. signNow also provides apps for iOS and Android devices.
Supported browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows 10, Windows 11, macOS Mobile apps iOS and Android signNow apps
Healthcare organizations should use managed devices, current browser security updates, and role-based account provisioning when staff handle protected health information. Teams requiring API access, SSO, or advanced authentication should confirm the selected signNow plan and HIPAA BAA requirements before deployment.
Processing stages for patient release forms
Processing time depends on accurate authorization details and patient response; HIPAA supplies retention requirements, not a universal signing deadline.
Prepare authorization
Deliver to patient
Patient turnaround
Complete and archive
Legal standing of electronic authorization records
For a U.S. business transaction, an electronic authorization can carry legal effect when the signer intends to sign, consents to electronic records, can be identified, and the record remains reproducible. ESIGN and UETA support that framework, but they do not replace HIPAA authorization requirements or cover wills and certain court filings.

Best practices for completing this form
Accurate scope, recipient details, patient consent, and controlled access make this authorization easier to review and safer to process.
Limit the requested record scope
Verify recipient and purpose
Confirm the expiration date
Control staff permissions
Documents outside this authorization workflow
Wills and codicils
Court orders
Family law decrees
Real-estate deeds
Troubleshooting patient authorization workflows
Use these answers to resolve field, signing, HIPAA, access, and record-preservation issues involving this patient release authorization.
Upload the source PDF again and review signNow’s detected fields. Add required recipient, purpose, expiration, and signature fields manually before sending if the form’s printed labels are not recognized.
The Business plan includes templates, audit trails, and legally binding eSignatures. If the healthcare workflow needs bulk send, Business Premium adds that capability; confirm a HIPAA BAA and applicable account configuration separately.
A healthcare organization should use signNow’s HIPAA-compliant offering with a BAA when protected health information is involved. HIPAA’s record-retention rule is six years from creation or the last effective date under 45 CFR §164.530(j).
Check that the patient’s email address is correct, resend the invitation, or provide a controlled signing link. Require SMS authentication when the organization’s release policy calls for stronger signer verification.
Review the authorization before sending and confirm the recipient, purpose, requested records, and expiration. A signature alone does not correct missing or overly broad authorization details under the organization’s HIPAA release procedure.
Export the completed PDF and certificate of completion from signNow, then store them under the organization’s access policy. The audit trail preserves signing events, while the organization remains responsible for legal retention and disclosure decisions.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.