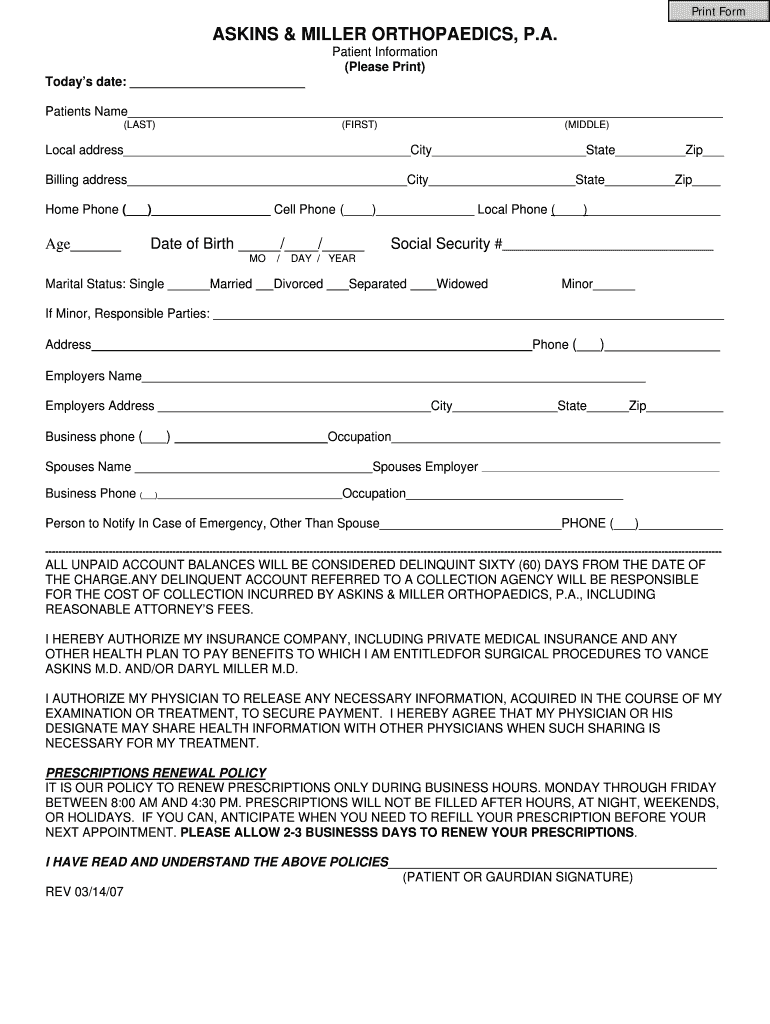
Patient Privacy Act Askins & Miller Orthopedics & Sports Form
Use a Patient Privacy Act Askins & Miller Orthopedics & Sports template to make your document workflow more streamlined.
Patient privacy form overview
The Patient Privacy Act Askins & Miller Orthopedics & Sports Form is a patient-facing privacy document for an orthopedic or sports-medicine setting, based on the form name supplied for this page. Its exact issuing authority, fields, filing deadline, and legal purpose are not provided here, so they should be confirmed against the source document and applicable state requirements. With signNow, an authorized sender uploads the form, reviews detected or manually placed fields, sends it to designated signers, captures the signing record, and stores the completed document with its audit trail. HIPAA obligations apply when the workflow handles protected health information.
Who uses this patient privacy form
Orthopedic practices
Orthopedic and sports-medicine practices use the Patient Privacy Act Askins & Miller Orthopedics & Sports Form for patient-facing privacy documentation, routing it to authorized signers and retaining the completed record with its audit trail.
Healthcare operations
Healthcare operations teams use the form when coordinating patient intake, consent, or privacy records across clinicians and administrative staff, subject to HIPAA safeguards, access controls, and the organization’s records policy.
Teams managing patient privacy forms
Orthopedic clinic administrators upload the Patient Privacy Act form, reuse a controlled template, assign required signers, and monitor completion without exposing the document to unrelated staff. Sports medicine intake teams send the form from shared workflows, use role-based access, and preserve the completed record with its audit trail for authorized compliance or records personnel.
How the patient privacy form works
The signNow workflow moves this patient privacy document from upload to verified completion without recreating its information manually.
Upload form: Upload the Patient Privacy Act form. Review fields: Auto-detect and review fillable fields. Send for signature: Send assigned fields to authorized signers. Archive record: Store the signed record and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete this patient form
Follow the document-specific workflow below to prepare, route, sign, and preserve the Patient Privacy Act Askins & Miller Orthopedics & Sports Form.
Upload form:
Upload the exact source PDF. Check fields:
Review detected fields and add missing ones. Assign signers:
Assign patient and staff signers. Send request:
Send the completed request through signNow. Store record:
Store the signed form with its audit trail.
Recommended setup for patient privacy forms
Use a controlled healthcare workflow that verifies signers, records consent, and preserves signed Patient Privacy Act documentation.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture signer, timestamp, IP, and actions |
| Document retention | Six years for HIPAA documentation |
| Encryption | TLS 1.2/1.3 and AES-256 encryption |
What the patient form audit trail records
The audit trail documents technical events around this form’s signing process, creating a reviewable record distinct from field setup.
Authenticate signer:
Timestamp event:
Hash document:
Seal document:
Record activity:
Export evidence:
Security for patient privacy forms
Transport encryption:
Storage encryption:
HIPAA safeguards:
Control assurance:
Security management:
Signer authentication:
Privacy pitfalls in patient form workflows
Patient identifiers can appear in routing emails or downloaded copies when recipients are not limited to staff who need the Patient Privacy Act form. An incomplete signature or missing date can leave the patient privacy record unable to show clear consent or acknowledgment. Using an outdated template can omit required language, fields, or signer assignments from the Askins & Miller Orthopedics & Sports workflow. Uncontrolled downloads can separate the signed form from its audit trail and weaken the organization’s recordkeeping process.
Retention periods for signed patient records
Keep records according to the applicable rule; HIPAA documentation generally requires six years from creation or last effective date.
Six years for privacy documentation
Six years for patient authorizations
Six years for acknowledgment records
Six years for disclosure records
Six years for restriction requests
Record-keeping practices for signed forms
Retain the signed Patient Privacy Act form with its audit evidence, access controls, and applicable HIPAA documentation schedule.
Export the signed form with its audit trail
Apply six-year HIPAA retention correctly
Use controlled archival storage for patient information
Control retrieval throughout the retention period
Troubleshooting patient privacy form workflows
Use these checks when field detection, signer access, HIPAA safeguards, retention, or plan limits interrupt completion of this patient privacy form.
If the Patient Privacy Act form fields are not detected, upload the original PDF again and inspect the field layout. signNow supports templates and fillable fields, but a scanned image may require manual placement before sending.
If a patient cannot open the signing request, verify the email address, resend the invitation, or provide a controlled signing link. The sender should confirm identity and avoid forwarding a link containing protected information.
If the workflow requires HIPAA treatment, confirm a signNow Business Associate Agreement is in place before sending protected health information. signNow identifies HIPAA compliance as requiring a BAA; the organization remains responsible for its workflow controls.
If a signer disputes completion, retrieve the completed document and audit trail. signNow audit trails record signing activity, timestamps, and related events, supporting evidence of the electronic transaction under ESIGN and applicable UETA rules.
If the form must be retained as HIPAA documentation, use six years from creation or last effective date under 45 CFR 164.530(j). A clinic’s broader medical-record policy may impose a longer period.
If a plan limit affects sending, review the selected signNow plan. Business is $8 per user per month billed annually, while Business Premium is $15 and includes bulk send; subscription plans include 100 signature invites per user annually.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.