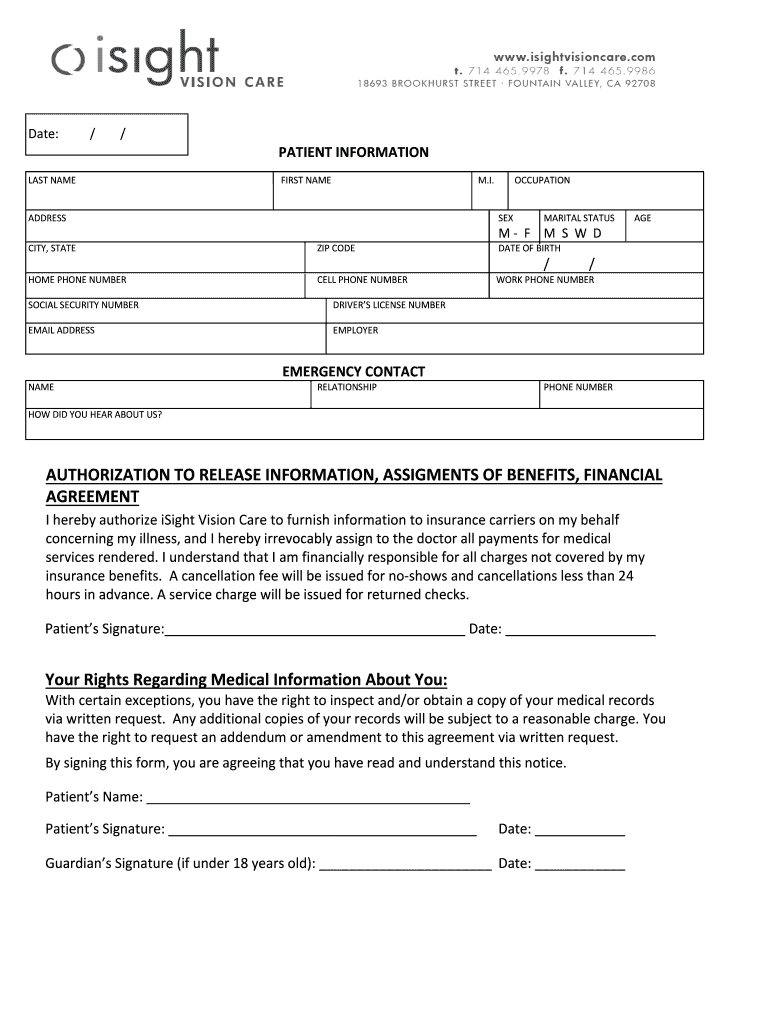
Authorization To Release Information Patientpop
Use a AUTHORIZATION TO RELEASE INFORMATION PatientPop template to make your document workflow more streamlined.
What this Patientpop authorization does
Authorization To Release Information Patientpop is a healthcare permission form that records a patient’s approval to disclose specified information to a named recipient. The signer identifies the information covered, purpose, recipient, and authorization period before signing. In signNow, upload the Patientpop document, place or auto-detect fillable fields, assign signer roles, and send it for review and signature. The completed authorization and audit trail can then be stored together. HIPAA privacy requirements and state law determine whether the proposed disclosure is permitted.
Legal value of the authorization
A completed Patientpop authorization documents a patient’s intent and permission for a defined disclosure, helping healthcare teams apply HIPAA controls consistently. Electronic execution may receive legal recognition under ESIGN and UETA when consent, attribution, intent, and reproducible records are established; state privacy and healthcare rules still govern the release itself.

Who uses this authorization
Healthcare providers
Patientpop healthcare teams use this authorization to capture a patient’s permission before sharing designated medical information with named recipients. They should identify the information, purpose, recipient, expiration, and required signatures before sending through signNow.
Patients and representatives
Patients and authorized representatives review the release scope, confirm recipient details, and sign electronically. Health plans, specialists, attorneys, or other named recipients can receive the completed authorization when disclosure rules permit.
Business types using this authorization
Patientpop authorization workflows suit healthcare organizations that must document permission before releasing specified patient information.
A solo medical practice can send one Patientpop authorization from a reusable signNow template, capture the patient’s electronic signature, and retain the completed release without coordinating an in-person appointment for every disclosure. A multi-specialty clinic can route authorizations to patients, representatives, and designated recipients while limiting access to protected health information. Audit trails document each signature and completed release for internal review. An enterprise healthcare network can standardize Patientpop authorization templates across locations, assign roles, and connect signed records to controlled repositories while applying HIPAA safeguards and organization-specific retention policies.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the Patientpop workflow works
The signNow workflow turns the Patientpop authorization into a controlled sequence from document preparation through signed-record storage.
Upload document: Upload the Patientpop authorization to signNow. Prepare fields: Auto-detect or place required signing fields. Assign signers: Assign the patient and recipient roles. Finalize record: Complete, audit, and store the release.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the Patientpop audit trail records
A completed Patientpop authorization should retain technical evidence showing who signed, when the event occurred, and how the final record was preserved.
Identify signer:
Capture timestamp:
Hash document:
Seal record:
Record activity:
Export evidence:
Recommended Patientpop workflow setup
Configure the Patientpop authorization around signer identity, protected information, audit evidence, and the retention rule for the underlying healthcare record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Electronic signature with intent record |
| Audit trail | Export with completed authorization |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 encryption |
Features for Patientpop authorizations
signNow connects document preparation, signer routing, audit evidence, and protected storage to the specific workflow for releasing Patientpop information.
Fillable fields
Upload the Patientpop authorization to signNow and place signature, date, initials, and required text fields without rebuilding the document manually. Review the completed layout before assigning the patient or representative.
Signer routing
Send the authorization to named signers by email or controlled signing link. signNow records the signing sequence and helps prevent disclosure until required signatures and fields are completed.
Electronic consent
Capture the patient’s intent and consent through an electronic signing workflow. For consumer-facing records, pair the process with the disclosure and access requirements in 15 U.S.C. §7001(c).
Audit trail
Preserve the signed authorization with its signNow audit trail. The record can show signing events, timestamps, document activity, and completion evidence needed for internal healthcare review.
Privacy controls
Protect release records with signNow’s encryption controls and documented compliance capabilities. HIPAA workflows require appropriate safeguards and a business associate agreement where the organization’s role requires one.
Reusable templates
Use reusable Patientpop authorization templates for recurring releases. Standardized recipient, purpose, expiration, and information-scope fields reduce omissions while allowing staff to review each patient-specific disclosure.
Privacy pitfalls to check first
Listing a recipient without defining the permitted information can create an overbroad disclosure and complicate HIPAA privacy review. Omitting the purpose or expiration date can make the Patientpop authorization incomplete for the intended release workflow. Sending protected health information before required signatures are complete can expose data without documented patient permission. Allowing unrestricted staff access to signed authorizations can create an avoidable disclosure risk and weaken internal accountability.
Technical requirements for signing
Use a current version of Chrome, Firefox, Safari, or Edge on Windows 10, macOS, iOS, or Android. signNow provides browser-based access and mobile apps for reviewing and signing the Patientpop authorization. Use an encrypted connection and confirm that the device is managed appropriately before viewing protected health information.
Supported browsers Chrome, Firefox, Safari, Edge Operating systems Windows 10, macOS, iOS, Android Device access Desktop and mobile web access
Healthcare organizations should apply managed-device controls, role-based access, and approved storage locations for completed Patientpop authorizations. Enterprise deployments may also use signNow API access, SSO provisioning, and integrations such as Microsoft 365, Google Drive, Box, or Salesforce. Configure retention and access policies separately from the signing workflow, and confirm that any HIPAA obligations, including a required business associate agreement, are addressed.
Security controls for release records
Data in transit:
Data at rest:
Security reporting:
Information security:
Health information safeguards:
Electronic signature framework:
Retain and protect authorization records
Record retention and audit controls help healthcare teams demonstrate what the patient authorized, when it was signed, and how the document was protected.
Apply the correct retention period
Export the audit trail
Archive signed records securely
Verify every release detail
Retention periods for related records
Keep the signed Patientpop authorization according to the record category it supports, and apply the longer applicable state or organizational requirement when documented.
Six years for HIPAA records
Three years from tax filing
Later of three years or one
Three years for payroll records
Five years after injury year
Authorization troubleshooting questions
Resolve field, privacy, authentication, and recordkeeping questions before releasing patient information through a signed authorization.
The signNow Business plan includes templates, audit trails, and legally binding eSignatures at $8/user/month with annual billing. Place fields on the authorization, assign the patient and recipient, and confirm required fields before sending.
For protected health information, signNow is HIPAA compliant when a business associate agreement is required and in place. Confirm your organization’s BAA, restrict document access, and avoid sending unnecessary medical details through unsecured channels.
The Business plan includes 100 signature invites per user per year, with overage fees. Business Premium adds bulk send at $15/user/month annually; choose it only when repeated patient releases justify batch distribution.
Use signNow’s audit trail to review signer identity events, timestamps, document activity, and completion evidence. Export the audit trail with the signed authorization so the disclosure record can be reviewed independently.
A patient may sign electronically when intent, consent, attribution, and record reproduction requirements are satisfied under ESIGN and applicable state law. For consumer-facing records, provide the electronic-record disclosure required by 15 U.S.C. §7001(c).
If a recipient cannot open the authorization, resend the signNow invitation or use a controlled signing link. Verify the recipient’s email, access permissions, and authentication method before sharing protected health information.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.