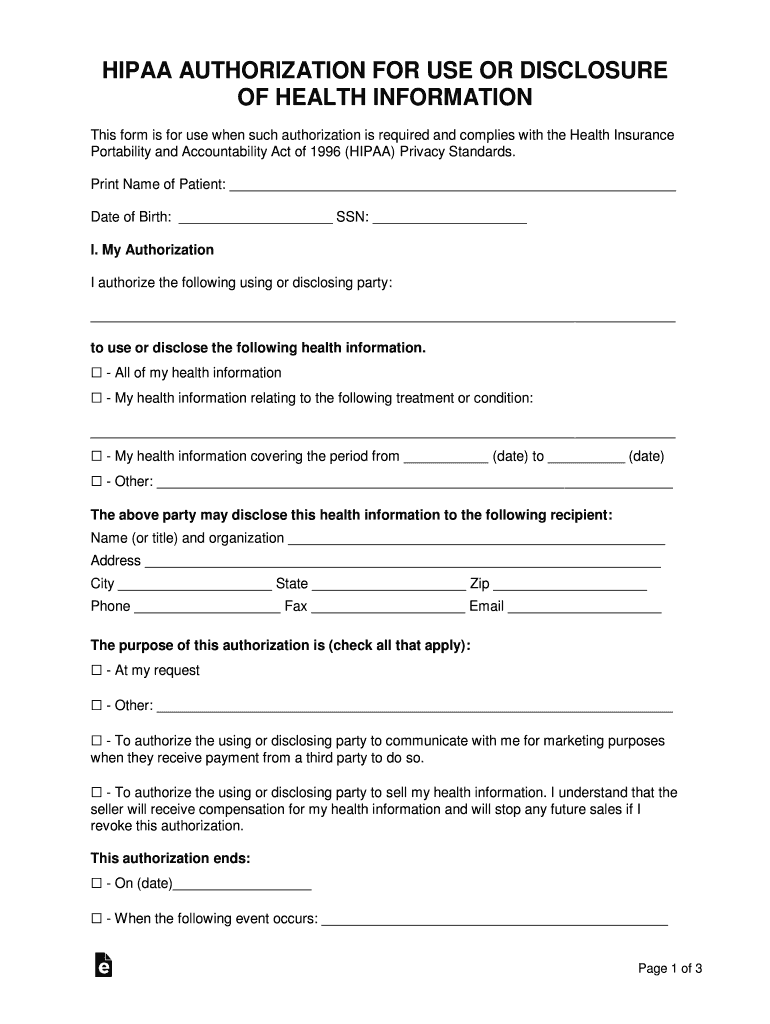
HIPAA Authorization For Use Or Disclosure Form
Use a HIPAA AUTHORIZATION FOR USE OR DISCLOSURE template to make your document workflow more streamlined.
What this HIPAA authorization form does
A HIPAA Authorization For Use Or Disclosure Form gives a patient or personal representative written permission for a covered entity to use or disclose specified protected health information to a named recipient. It identifies the information, purpose, recipient, expiration, and signer. Under 45 CFR §164.508, the authorization must be specific and signed; it is not a blanket release for every record. With signNow, a sender uploads the form, verifies fillable fields, sends it for signature, and stores the completed record with an audit trail.
Key features for HIPAA authorization workflows
A focused workflow helps healthcare organizations collect the required authorization details, obtain consent, and preserve evidence before disclosing protected health information.
Defined scope
Captures the patient, recipient, purpose, information scope, expiration, and signature in one structured authorization record for review before disclosure.
Remote signing
Routes the authorization to the patient or representative for electronic completion and signature without requiring a paper exchange.
Audit trail
Records timestamps, signer activity, delivery events, and completion evidence that can support an internal compliance review.
HIPAA controls
Uses signNow’s HIPAA compliance option with a required Business Associate Agreement for workflows involving protected health information.
Signer verification
Applies SMS authentication or stronger signer verification where the organization requires additional evidence of signer identity.
Centralized records
Keeps the authorization and completion evidence together so staff can confirm the permission before releasing records.
Recommended HIPAA authorization setup
Configure the authorization workflow around signer identity, disclosure evidence, protected information, and the HIPAA retention requirement.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for higher-risk disclosures |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps, IP, and completion events |
| Document retention | 6 years (HIPAA 45 CFR 164.530(j)(2)) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
How to complete this HIPAA authorization
Use this signNow workflow to prepare the authorization, collect informed consent, and preserve evidence for the specific disclosure request.
Upload form:
Upload the HIPAA authorization PDF to signNow. Check fields:
Review auto-detected fields and add missing authorization fields. Assign signer:
Assign the patient or representative as signer. Send securely:
Send the authorization through email or a signing link. Review signature:
Collect the signature and review the completed disclosure scope. Store evidence:
Download the signed form and completion certificate.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the signNow audit trail records authorization
The audit trail preserves technical evidence showing who signed this HIPAA authorization, when each action occurred, and whether the record changed.
Authenticate signer:
Capture timestamps:
Hash document:
Seal document:
Log activity:
Export evidence:
Security controls for protected health information
HIPAA protection:
Data encryption:
Transport security:
Security certification:
Information security:
Electronic signatures:



Retention periods for authorization records
Apply the HIPAA schedule first, then document any longer period required by the record’s separate legal or industry context.
Six years: HIPAA authorizations
Three years: federal tax records
Six years: substantial understatement
Three years: FLSA payroll records
Thirty years: OSHA exposure records
Privacy pitfalls in HIPAA authorization forms
Including an entire medical record instead of identifying the specific information authorized for disclosure can exceed the patient’s intended consent scope. Sending the completed authorization to an unintended recipient exposes protected health information and weakens access-control evidence. Omitting the purpose, expiration date, or signature date can make the authorization incomplete for the intended disclosure. Using a shared sender account obscures individual attribution and makes the audit trail less useful during compliance review.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Team roles for HIPAA authorization workflows
Healthcare administrators can publish a controlled HIPAA authorization template, assign roles, and limit sending permissions so staff use approved disclosure language and recipients. signNow shared templates and administrative controls help separate template maintenance from patient-facing sending while preserving the completed document’s audit trail and access history. Patient-access teams can delegate sending to authorized staff while retaining centralized oversight of the authorization workflow. A clinic can route completed forms for review, restrict protected health information access, and connect signNow with systems such as Salesforce, Microsoft 365, or Google Drive according to its internal policy.
Troubleshooting HIPAA authorization workflows
Resolve the specific field, authentication, plan, and retention issues that can prevent a HIPAA authorization from being reliable evidence.
The Business plan includes legally binding eSignatures and audit trails, while HIPAA compliance requires a Business Associate Agreement. Confirm the required agreement and account configuration before sending protected health information through the workflow.
Business Premium includes bulk send, while the Business plan does not include that feature. For repeated patient authorization requests, use Business Premium or send each prepared document individually after reviewing the recipient and disclosure scope.
Use signNow fields for the patient’s name, requested information, recipient, purpose, expiration, signature, and date. Auto-detection can identify fillable areas, but the sender must verify that every HIPAA-required authorization element is present and accurate.
A typed, drawn, or click-to-sign signature can satisfy ESIGN and UETA when intent, consent, attribution, and record retention are demonstrated. For consumer-facing records, provide the electronic-record disclosure and access information required by 15 U.S.C. §7001(c).
The Enterprise plan adds advanced signer authentication, while signNow supports SMS-based authentication options. Select an authentication level appropriate to the disclosure risk, and retain the resulting event details in the audit trail.
HIPAA compliance is listed as available with a BAA, while Business, Business Premium, and Enterprise plans have signature-invite limits. Confirm the current plan allowance and overage terms before sending large authorization batches.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.