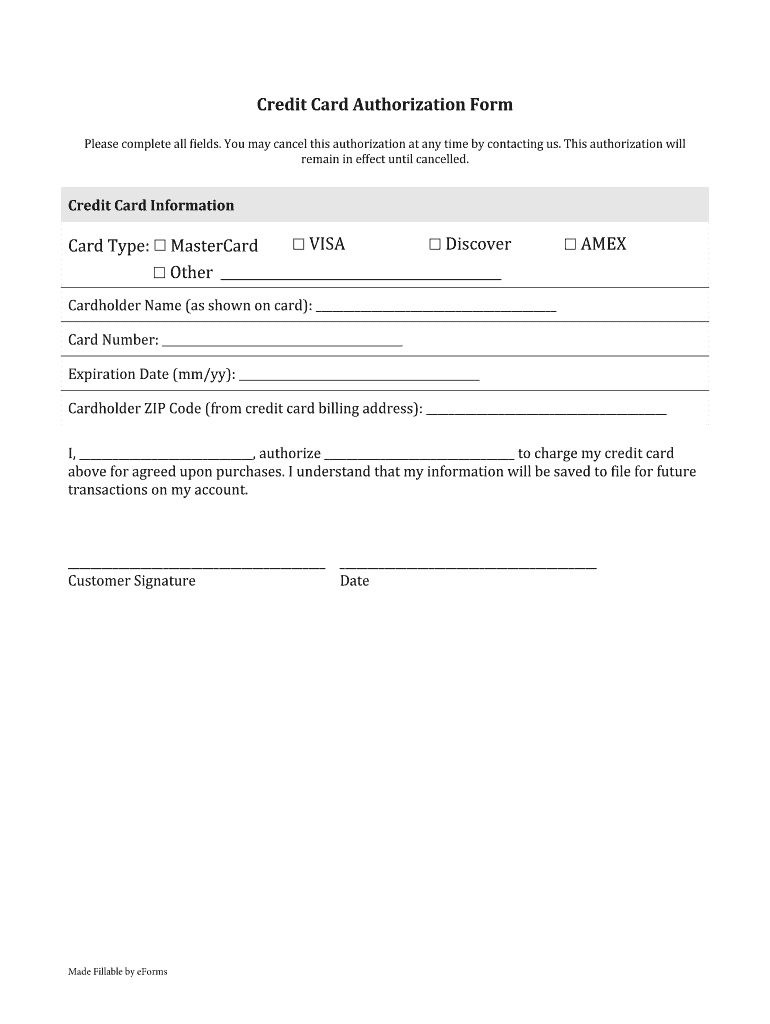
Simple Credit Card Authorization Form
Use a Simple Credit Card Authorization Form template to make your document workflow more streamlined.
What this credit card authorization form does
A Simple Credit Card Authorization Form gives a merchant written permission to charge a customer’s card under stated terms. It normally identifies the customer and business, records card and billing information, specifies the approved transaction or amount, and captures the customer’s signature and date. With signNow, upload the form, review detected fillable fields, add the signer, and send it electronically. The signer reviews the authorization, consents, and signs. The completed PDF and audit trail preserve the transaction record, while PCI DSS controls remain relevant to cardholder data handling.
Who uses this authorization form
Merchants
A merchant or service provider records the customer’s name, card details, authorized amount, billing information, and signature before processing an agreed charge.
Cardholders
A customer reviews the business name, payment scope, expiration information, and authorization terms before signing the completed form.
Features for completing the authorization
The workflow keeps the approved charge, signer action, completed document, and supporting audit evidence together for review.
Defined scope
Capture the customer’s name, billing details, card information, authorized amount, and transaction scope in one signed record.
Fillable fields
Place signature, date, text, and other fillable fields after uploading the authorization form to signNow.
Remote signing
Send the completed authorization to the customer by email or a signNow signing link.
Audit trail
Preserve signer actions, timestamps, and document history alongside the completed authorization.
Mobile access
Review and sign from supported signNow mobile apps on iOS or Android.
Data protection
Protect stored records with TLS in transit, AES-256 at rest, PCI DSS certification, and SOC 2 Type II controls.
How the authorization workflow works
The form moves from payment-detail preparation to signer approval and documented retention in four controlled stages.
Upload: Upload the authorization PDF Check fields: Review detected payment fields Send: Send to the cardholder Retain: Store the signed PDF and audit trail
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Quick steps to complete the form
Prepare the payment authorization, confirm signer fields, and preserve the completed document with its supporting evidence.
Upload:
Upload the authorization PDF. Review:
Confirm fields for payment details. Assign:
Assign the customer as signer. Send:
Send the signing request. Store:
Export the signed record.
Recommended authorization workflow settings
Use field controls and signer verification that match the payment amount, customer relationship, and card-data handling policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP, and action history |
| Document retention | Retain by business and PCI DSS policy |
| Encryption | TLS 1.2 or TLS 1.3 and AES-256 |
Security for card authorization records
Data in transit:
Data at rest:
Cardholder safeguards:
Control assurance:
Security management:
Electronic signatures:
Platform requirements for signing
The Simple Credit Card Authorization Form can be prepared and signed through Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow also provides mobile apps for iOS and Android, allowing authorized signers to review payment details and complete the form from a supported device. Use TLS-protected connections when accessing the document.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS computers Mobile access iOS and Android mobile apps
Organizations handling cardholder information should use managed Windows, macOS, iOS, or Android devices and restrict access to assigned users. Teams can connect signNow through its API, configure SSO where available, and retain the completed authorization with its audit trail. PCI DSS obligations remain applicable to the organization’s payment environment and card-data handling procedures.
Risks of incomplete card authorization
Charge dispute
Weak evidence
Authorization ambiguity
Data exposure
Best practices for this authorization form
Accurate fields, defined charge limits, signer attribution, and controlled storage make the authorization more useful during payment review.
Complete every payment field before sending
Define the permitted charge precisely
Check field assignments before customer signing
Store the signed record with evidence



Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting this authorization workflow
These answers address field setup, electronic-signature validity, signer evidence, plan selection, and cardholder-data responsibilities for this form.
Upload the source PDF again and inspect signNow’s automatically detected fields. Add or resize text, date, and signature fields manually, then assign every required field to the correct signer before sending the authorization.
The Business plan costs $8/user/month when billed annually and includes templates and audit trails. Business Premium costs $15/user/month annually and adds bulk send, while Enterprise costs $30/user/month and adds advanced signer authentication.
signNow supports legally binding electronic signatures under ESIGN and UETA. The signer must show intent, consent to electronic records where required, and receive a reproducible completed record. A card authorization still must satisfy applicable payment and consumer-protection requirements.
For consumer-facing electronic records, ESIGN 15 U.S.C. §7001(c) requires disclosure of the right to paper, access to the electronic format, and procedures for withdrawing consent. Provide those disclosures when the customer transaction falls within that requirement.
signNow’s audit trail records signing activity, timestamps, IP information, and document history. Export the completed authorization and certificate or audit evidence with the signed PDF, then retain them under the organization’s documented card-data and records policy.
PCI DSS certification helps protect cardholder data, but the merchant remains responsible for its payment environment. Avoid unnecessary card-data exposure, restrict access, and coordinate storage and processing practices with the organization’s PCI DSS controls.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.