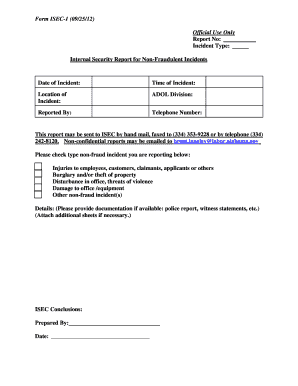
Internal Security Fraudulent Form
Use a Internal Security Fraudulent Form template to make your document workflow more streamlined.
What an internal fraud report does
An Internal Security Fraudulent Form documents suspected fraud inside an organization; it is not a standardized federal, IRS, USCIS, or state filing. The form can capture the reporter’s identity, incident date, affected process, suspected conduct, evidence, and acknowledgment for controlled review. With signNow, a sender uploads the document, auto-detects fillable fields, adds the reporter and reviewers, sends signature requests, and stores the completed report with an audit trail. ESIGN and UETA may support electronic signatures when intent, consent, attribution, and record retention are established.
Who uses internal security fraud reports
Compliance teams
Compliance and internal-audit teams use the form to record suspected control failures, supporting evidence, reviewer assignments, and electronic acknowledgments. They can route reports by role, preserve the completed document with its audit trail, and restrict access to investigation participants.
Review teams
Security, legal, and human-resources teams use the form for employee or system-related allegations requiring documented review. A controlled signNow template can capture statements, approvals, and follow-up actions without presenting the internal report as an official government filing.
How to complete an internal fraud report
Use a controlled sequence that separates document preparation from signature collection and evidence preservation.
Upload document: Upload the internal report template Check fields: Auto-detect and review fillable fields Assign recipients: Add reporters and authorized reviewers Complete record: Collect signatures and preserve audit evidence
How the audit trail preserves fraud evidence
signNow records the signing events surrounding an internal fraud report, helping reviewers connect signer identity, timing, document history, and final evidence.
Authenticate signer:
Timestamp event:
Hash document:
Seal record:
Log activity:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for internal fraud reports
Configure the report around controlled identity checks, documented evidence, and an approved investigation-retention process.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn eSignature |
| Audit trail | Enabled for every signing event |
| Document retention | Organization schedule and legal hold |
| Encryption | TLS in transit and AES-256 at rest |
Security controls for internal fraud reports
Encryption controls:
Healthcare safeguards:
Security certification:
Information security:
Privacy compliance:
Transport and storage:
Privacy pitfalls when completing fraud reports
Sensitive names, account details, and incident evidence may remain visible to recipients who need only part of the report. An internal reporter may sign without documenting consent for electronic records, weakening the evidence trail during later review. Shared links can expose a fraud report when access permissions are broader than the investigators, managers, or counsel handling it. Unrestricted downloads can place signed reports in personal storage, creating uncontrolled copies of confidential investigation material.
Legal standing of internal fraud reports
An Internal Security Fraudulent Form is an internal business record, not a federally issued form. Under ESIGN and UETA, its electronic signature may be admissible when intent, consent, signer attribution, and reliable record retention are shown. Wills, court orders, family-law decrees, and other statutory exclusions remain outside that framework.

Risks of mishandling internal fraud reports
Weak signature proof
Privacy breach
Evidence integrity
Limited enforceability
Best practices for internal fraud reports
Use a controlled template, a documented review path, and an evidence-preservation process so each signed internal fraud report remains understandable and defensible.
Separate facts from allegations
Restrict access by investigation role
Document electronic consent
Preserve the complete evidence package



Troubleshooting internal fraud reports
Resolve signing, access, consent, and evidence questions before distributing an Internal Security Fraudulent Form.
signNow’s Business plan supports templates, audit trails, mobile apps, and legally binding eSignatures. Upload the report, review detected fields, assign the reporter and reviewers, and send the signing request. Confirm that your organization’s access policy permits electronic completion.
Yes, signNow supports SMS OTP and other signer-authentication options, while advanced signer authentication is listed for Enterprise. Select the strength your investigation policy requires and preserve the authentication event in the audit trail.
ESIGN, 15 U.S.C. §7001(c), requires consumer-facing electronic records to address paper access, electronic access, and withdrawal procedures. If the reporter is a consumer, provide the required disclosure before signing and retain it with the report.
A signed report is not automatically an official finding or government filing. Treat it as internal evidence, verify allegations separately, and preserve intent, signer attribution, the completed record, and its audit trail for later review.
Business Premium includes bulk send, while Enterprise adds advanced signer authentication. For a single investigation, send the report directly; use bulk send only for authorized, separate recipients and review confidentiality controls before deployment.
signNow encrypts data in transit with TLS 1.2 or 1.3 and at rest with AES-256. HIPAA compliance requires a BAA, and regulated teams should separately confirm their retention, access, and investigation requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.