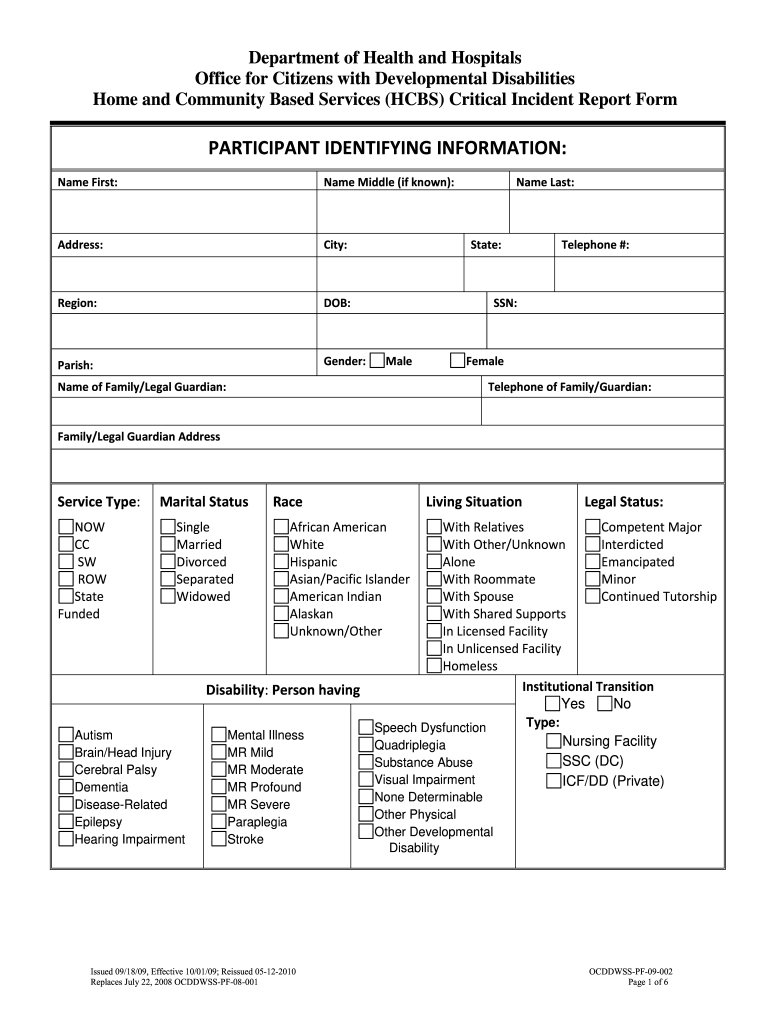
Critical Incident Form
Use a Critical Incident Form template to make your document workflow more streamlined.
What a critical incident form records
A Critical Incident Form is an internal record used to document a serious event, its immediate effects, and the response that followed. It is not one federally standardized U.S. form, so organizations define its fields, approval path, and retention policy. A completed record generally identifies the event, people involved, observed facts, actions taken, notifications, and follow-up requirements. With signNow, an organization can upload its approved form, place or detect fillable fields, route it to authorized reviewers, collect signatures, and preserve the completed document with an audit trail.
How the incident form workflow works
A controlled workflow moves the incident record from initial documentation through review, signature, and retention.
Upload form: Upload the approved incident template to signNow. Prepare fields: Review detected fields and add incident-specific prompts. Route securely: Send the record to assigned reviewers and signers. Archive record: Store the completed form with its audit trail.
Key capabilities for incident reporting
A structured Critical Incident Form workflow helps teams document facts, obtain review, and preserve an accountable record without relying on paper circulation.
Incident details
Capture the event date, location, people involved, observed conditions, and immediate response in one controlled record for later review.
Required fields
Use required fields for facts such as severity, witnesses, notifications, and corrective actions, reducing incomplete submissions during urgent reporting.
Review routing
Route the completed Critical Incident Form to designated supervisors, safety personnel, or compliance reviewers before final approval.
Audit trail
Collect legally attributable electronic signatures and preserve signer actions, timestamps, and document history with the completed incident record.
Access control
Protect sensitive witness, employee, patient, or customer information through controlled access and signNow security controls appropriate to the workflow.
Connected records
Connect incident records with systems such as Microsoft 365, Google Drive, Box, or Procore for organized follow-up and storage.
What the incident audit trail captures
The audit trail shows how the Critical Incident Form moved from preparation through review and completion, supporting later accountability.
Authenticate signer:
Timestamp actions:
Track history:
Bind signature:
Seal document:
Export audit trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Platform requirements for incident forms
Complete the Critical Incident Form through signNow in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing authorized staff to review or sign incident records away from a desk.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile systems iOS and Android mobile apps
Organizations should manage devices, user permissions, and storage destinations before deployment. Enterprise workflows may also require API access, SSO provisioning, or certificate and long-term-validation configuration. Confirm these controls against the organization’s incident-response policy, privacy obligations, and any industry-specific retention rule.



Security for incident records
Data encryption:
Independent assurance:
Security certification:
Health data protection:
Signature compliance:
Privacy frameworks:
Best practices for incident records
A defensible Critical Incident Form process combines accurate event facts, controlled access, documented approval, and retention aligned with the applicable rule.
Set retention from the governing rule
Preserve the audit trail with the form
Restrict sensitive incident information
Control template revisions
Legal standing of a signed incident record
A signed Critical Incident Form can support an organization’s evidence of what was reported, reviewed, and acknowledged when ESIGN or applicable state law requirements are met. Validity depends on intent, consent, attribution, and reliable retention. Wills, court orders, family-law decrees, and other ESIGN exclusions require separate legal handling.

Privacy and disclosure pitfalls
Incident narratives may include names, medical details, or witness statements that should not be visible to every recipient or signer. A missing consent record can weaken the organization’s explanation of how an individual’s electronic incident documentation was obtained. Sending the form to an incorrect email address can expose sensitive facts and undermine confidence in the incident record. Unrestricted template editing can remove required fields, alter approval routing, or create inconsistent records across locations and teams.
Risks from incomplete incident records
Incomplete record
Unauthorized disclosure
Missing escalation
Unclear attribution
Critical incident form questions
These answers separate organizational reporting requirements from signNow workflow, security, and electronic-signature capabilities.
A Critical Incident Form is not a single federally prescribed document. Confirm the organization’s approved template, required fields, reviewer roles, and retention policy before uploading it to signNow. signNow can route and audit the approved record, but it does not determine which incident facts your employer or regulator requires.
Upload the organization’s approved PDF or template, then inspect signNow’s detected fields before sending. Add or correct text, date, checkbox, initials, and signature fields manually when detection does not match the incident-reporting workflow. Do not rely on automatic detection without reviewing every required field.
Use signNow’s routing controls to send the record to the assigned supervisor, safety reviewer, or compliance administrator. If different incidents require different reviewers, create separate approved templates or routing rules rather than allowing the sender to choose an unapproved recipient.
For employee, patient, or customer information, restrict access to authorized recipients and apply the organization’s privacy policy. HIPAA may apply when the incident record contains protected health information; signNow states HIPAA compliance requires a business associate agreement.
Electronic signatures can satisfy ESIGN and UETA requirements when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible. Consumer-facing workflows may also require the ESIGN disclosure and access requirements in 15 U.S.C. §7001(c).
The Business plan is listed at $8 per user per month when billed annually and includes audit trails, templates, and mobile apps. Business Premium is listed at $15 annually and adds bulk send. Confirm plan limits before deploying high-volume incident workflows.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.