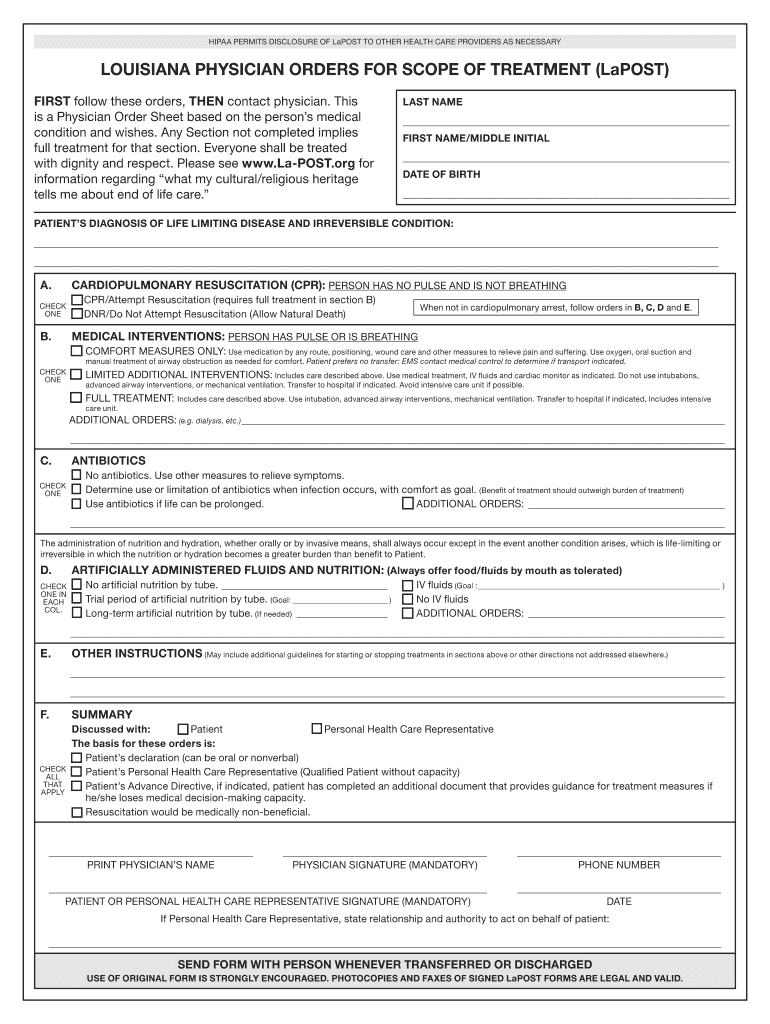
HIPAA Permits Disclosure Of Lapost To Other Health Care Form
Use a HIPAA PERMITS DISCLOSURE OF LaPOST TO OTHER HEALTH CARE template to make your document workflow more streamlined.
What this HIPAA disclosure form does
The HIPAA Permits Disclosure Of Lapost To Other Health Care Form records a patient’s permission to disclose specified health information to another healthcare recipient. The signer identifies the information, recipient, purpose, and authorization terms, then signs the record. In signNow, the sender uploads the form, reviews or adds fillable fields, sends it to the patient or authorized representative, and stores the completed PDF with its audit trail. HIPAA documentation rules under 45 CFR 164.530(j) generally require six-year retention for covered-entity documentation.
Who uses this HIPAA disclosure form
Healthcare providers
Healthcare providers use the form to document a patient’s permission before releasing specified health information to another healthcare provider or authorized recipient. Teams can route signatures electronically, preserve the completed authorization, and apply access controls appropriate to protected health information.
Health information teams
Medical billing, care coordination, and records teams use the form when a disclosure request requires documented patient permission. The workflow identifies the recipient, limits the information released, and preserves a signed record for later compliance review.
How the HIPAA disclosure workflow works
The workflow keeps recipient details, authorization language, signatures, and evidence connected from preparation through retention.
Upload form: Upload the disclosure PDF into signNow. Check fields: Auto-detect fields, then verify authorization details. Send form: Send the form to the identified signer. Preserve record: Store the signed authorization and audit trail.
Complete the HIPAA disclosure form
Follow these steps to prepare, sign, and preserve the HIPAA Permits Disclosure Of Lapost To Other Health Care Form in signNow.
Upload form:
Upload the HIPAA disclosure PDF. Review fields:
Check detected fields and add missing fields. Add signer:
Enter the patient or representative’s email. Send request:
Send the completed form for signature. Save records:
Store the signed PDF and audit trail securely.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for HIPAA disclosure records
HIPAA compliance:
Transport encryption:
Storage encryption:
Security certification:
Information security:
Audit trails:
Review the disclosure audit trail
The audit trail records the events surrounding this HIPAA disclosure form, helping demonstrate who signed, when it happened, and which document was completed.
Authenticate signer:
Record timestamp:
Track actions:
Seal history:
Complete document:
Export evidence:



Platform requirements for this form
Complete the HIPAA Permits Disclosure Of Lapost To Other Health Care Form through signNow on Chrome, Firefox, Safari, or Edge using Windows or macOS. signNow also provides iOS and Android mobile apps for reviewing and signing documents, with secure TLS connections required for online access.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android apps
Healthcare organizations should manage signing devices through their own security policies, restrict access to authorized personnel, and confirm that mobile use follows the organization’s HIPAA procedures. API, SSO, and integration requirements depend on the selected signNow plan and deployment design. A BAA and documented retention process remain necessary when the form contains protected health information.
Record-keeping practices for HIPAA forms
Preserve the authorization, audit evidence, and access controls together so the disclosure can be reviewed throughout its retention period.
Apply the six-year HIPAA retention rule
Export the audit trail with the form
Secure the completed authorization record
Validate scope before releasing information
Retention schedule for disclosure records
Use six years as the HIPAA documentation period, then check state law, legal holds, and organizational policies before deleting this form or its audit evidence.
Six years: HIPAA documentation
Six years: disclosure authorization
Six years: audit evidence
State law: longer period
Legal hold: until released
Pitfalls when preparing this disclosure
Leaving the recipient or permitted information blank can make the authorization unclear and delay disclosure review by the healthcare organization. Sending the completed form through an unmanaged channel can expose protected health information beyond the authorized recipient or internal disclosure team. Failing to capture electronic consent and signer intent can weaken the record supporting an electronic signature under ESIGN and applicable state law. Deleting the authorization before the six-year HIPAA documentation period can leave the covered entity unable to produce required disclosure documentation.
Troubleshooting this HIPAA disclosure form
Resolve field, signer, retention, and compliance questions before sending a HIPAA Permits Disclosure Of Lapost To Other Health Care Form.
Use signNow’s HIPAA-compliant configuration with a signed BAA before processing protected health information. The Business plan includes audit trails, while HIPAA compliance requires the applicable agreement and organizational safeguards beyond the signature transaction.
The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps. For HIPAA workflows, confirm that your account has the required BAA and configure access, retention, and authentication controls before sending this disclosure form.
If auto-detection misses a field, open the uploaded PDF in signNow’s editor and place the required text, date, checkbox, and signature fields manually. Review each field against the HIPAA disclosure language before sending it to the patient or authorized representative.
Use signNow’s audit trail to preserve signer identity information, timestamps, actions, and document history. HIPAA’s six-year documentation rule under 45 CFR 164.530(j) applies to covered-entity documentation, so align platform retention with your records policy.
Business Premium adds bulk send and kiosk mode, but this form still requires careful recipient identification. Use kiosk mode only for supervised in-person completion, and verify the signer’s authority before collecting protected health information.
signNow encrypts data in transit with TLS 1.2/1.3 and at rest with AES-256. Encryption does not replace HIPAA safeguards, so restrict workspace permissions, confirm the BAA, and avoid sending unnecessary health information in the form.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.