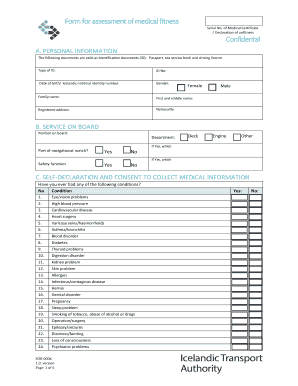
Of Medical Certificate Form
Use a Of Medical Certificate template to make your document workflow more streamlined.
What Of Medical Certificate Form does
Of Medical Certificate Form is a document used to record a healthcare provider’s certification for an authorized recipient, such as an employer, school, insurer, or occupational health program. The form typically identifies the individual, certification dates, provider details, restrictions or clearance statement, and signature. With signNow, a sender uploads the PDF, reviews detected fillable fields, assigns provider or recipient fields, sends the form electronically, and stores the signed record with its completion certificate and audit trail. HIPAA-covered workflows require a BAA and appropriate safeguards for protected health information.
Who benefits from medical certificates
Medical practices, occupational health teams, and healthcare organizations use this form when a signed health certification must reach an authorized recipient.
Solo medical practices can issue work or school certificates from a reusable template, collect the provider’s signature remotely, and preserve the completed record without printing or routing paper between offices. Occupational health clinics can send certificates to patients or employers after review, using controlled access and audit trails to document who signed, when the record changed, and when the completed form was delivered. Enterprise healthcare systems can standardize certificates across locations, delegate sending to authorized staff, and connect signNow workflows with systems such as Salesforce, NetSuite, or cloud storage while applying organization-wide privacy controls.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who completes this medical certificate
Healthcare providers
Healthcare providers use the certificate for signed work, school, or activity documentation. Staff can upload the form, place provider and recipient fields, send it for signature, and retain the completed record with an audit trail. HIPAA-covered workflows require a BAA and appropriate privacy controls.
Authorized recipients
Employers, schools, insurers, and occupational health departments receive certificates when authorized by the patient or required by a lawful process. They should verify required fields, limit access to personnel with a need to know, and retain the record under applicable policy or regulation.
How the medical certificate workflow works
The signNow workflow converts the medical certificate from an uploaded PDF into a controlled record with assigned fields, signatures, and completion evidence.
Upload form: Upload the medical certificate PDF to signNow. Add fields: Review detected fields and add provider, patient, date, and signature fields. Send securely: Send the prepared certificate to the authorized signer. Store evidence: Collect the signature and retain the completed record with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the certificate in signNow
Use this sequence to prepare, route, sign, and preserve Of Medical Certificate Form without losing required fields or completion evidence.
Upload form:
Upload the certificate PDF. Check fields:
Review detected fields and add missing signature or date fields. Assign signer:
Assign the provider or recipient and send the certificate. Save record:
Download the completed certificate and audit trail.
Set up secure certificate handling
Configure authentication, signatures, audit evidence, retention, encryption, and access for medical certificate workflows.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for sensitive certificates |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export completion certificate with signed record |
| Document retention | 6 years (HIPAA 45 CFR 164.530(j)) |
| Encryption | TLS 1.2/1.3 in transit and AES-256 at rest |
Understand the certificate audit trail
The audit trail records the technical events that connect the medical certificate, signer, signature action, and completed electronic record.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Track activity:
Retrieve evidence:
Protect medical certificate records
Protected health information:
Stored record encryption:
Secure transmission:
Independent controls:
Information security:
Privacy frameworks:
Check your device and browser requirements
Of Medical Certificate Form can be prepared in Chrome, Firefox, Safari, or Edge on Windows 10, Windows 11, or macOS. Mobile signing is available through signNow apps for iOS and Android, while TLS 1.2 or TLS 1.3 protects connections.
Desktop browsers Desktop browsers: Chrome, Firefox, Safari, and Edge support secure completion and review. Operating systems Operating systems: Windows 10, Windows 11, macOS, iOS, and Android. Connection security Connection security: TLS 1.2 or TLS 1.3 protects browser traffic during signing.
Organizations handling patient information should use managed Windows, macOS, iOS, or Android devices and confirm access policies before sending. API access, SSO provisioning, and certificate or long-term validation requirements depend on the selected signNow plan and the organization’s compliance design.
Avoid privacy and disclosure mistakes
Including a diagnosis or other unnecessary health detail can expose more protected information than the recipient needs. Sending the certificate before obtaining the signer’s electronic consent can weaken evidence that the signer accepted the transaction. Leaving completed certificates in personal email or unmanaged storage can create unauthorized-access and retention-control problems. Assigning broad workspace permissions may let staff view medical information unrelated to their responsibilities.
Follow a controlled medical certificate workflow
A controlled process reduces disclosure risk while preserving evidence that the medical certificate was completed, signed, and retained properly.
Limit the certificate to necessary information
Confirm recipient requirements before sending
Match authentication to certificate sensitivity
Archive the certificate and audit trail together
Establishing electronic certificate evidence
An electronic medical certificate can support a U.S. business record when the process demonstrates signer intent, electronic consent, attribution, and reliable retention under ESIGN, 15 U.S.C. ch. 96, and applicable UETA rules. Wills, court orders, family-law decrees, and other statutory exceptions remain outside that framework and may require different execution methods.

Resolve medical certificate workflow issues
These answers address field detection, delivery, HIPAA safeguards, plan selection, audit evidence, and electronic-signature validity for this certificate.
Upload the original PDF again and check whether its fields are flattened, locked, or image-only. signNow can detect fillable fields, but an administrator may need to place fields manually when the certificate contains a scanned signature line or unusual layout. Business plans include templates and audit trails.
Confirm that the recipient’s email address is correct, then review the document’s sending status and resend options in signNow. If the recipient needs a reusable access point, Business Premium includes quick invite links. Do not share medical information through an uncontrolled public link.
A medical certificate may contain protected health information. signNow identifies HIPAA compliance as available with a BAA, but the organization must obtain the BAA, configure access controls, and follow its own privacy procedures. Platform compliance does not replace the covered entity’s obligations.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps at $8/user/month with annual billing. Business Premium costs $15/user/month annually and adds bulk send and kiosk mode. Select the plan based on workflow volume and required controls.
The sender can review the signed certificate, completion certificate, timestamps, signer actions, and audit trail after completion. Export those records together and store them under the organization’s retention policy. For HIPAA-covered records, 45 CFR §164.530(j) requires six years.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are demonstrated. Consumer-facing healthcare records also require the disclosures and access procedures described in 15 U.S.C. §7001(c). Recipient, state, and clinical requirements may still demand paper or additional verification.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.