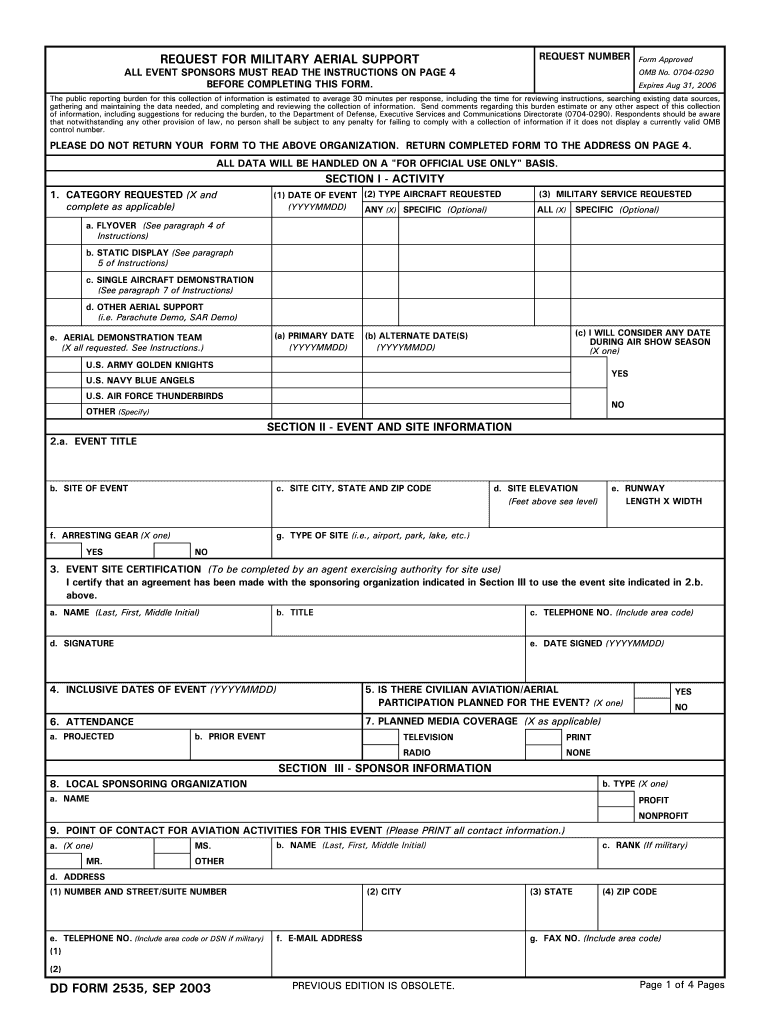
Public Reporting Burden For This Collection Of Information Is Gsa
Use a Public Reporting Burden For This Collection Of Information Is GSA 2016 template to make your document workflow more streamlined.
What this GSA burden statement records
Public Reporting Burden For This Collection Of Information Is Gsa is a government information-collection statement describing the respondent effort associated with a GSA collection. It is not a universal tax return, payroll form, or substitute for the agency’s source instructions. The document identifies the burden context supplied by the issuing materials; the available form name does not provide an agency number, filing deadline, estimated hours, respondent category, or submission address. In signNow, a sender uploads the source, checks fields, routes authorized reviewers, captures signatures, and retains the completed record with its audit trail.
Who benefits from this GSA burden statement
Government affairs specialists and federal program administrators use this statement to document the estimated time and resources required for a GSA information collection. signNow helps route the completed record for review, capture approvals, and preserve the supporting audit trail. GSA contractors and procurement teams use the record when reviewing a collection’s administrative impact before responding to agency requests. They can prepare the document in signNow, assign internal reviewers, and retain the executed version with timestamped activity history.
Who uses this GSA collection statement
GSA program teams
Federal program teams can use the statement for agency review workflows, provided the original GSA instructions remain controlling. signNow supports field preparation, role-based routing, electronic signatures, and audit-trail retention for the completed record.
Contractors and procurement
Contractors and procurement groups can complete assigned burden information and return it through an authorized reviewer. The workflow is useful for preserving the exact source document, signer sequence, completion timestamps, and downloadable evidence.
Complete the GSA statement in signNow
Use the source document as the authority, then prepare, route, sign, and preserve the record in a controlled workflow.
Upload document:
Upload the GSA burden statement to signNow. Review fields:
Check detected fields against the source document. Assign recipients:
Add authorized reviewers and signers. Send securely:
Send the prepared record for completion. Store evidence:
Download the signed PDF and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Best practices for this GSA record
Careful source control, recipient selection, audit-trail retention, and confirmation of missing instructions reduce avoidable errors in this public-reporting document.
Preserve the agency source document
Route reviewers by authorized role
Retain the audit trail
Confirm missing filing instructions
Processing stages for the GSA statement
The source materials do not specify a filing deadline or agency turnaround time, so processing depends on authorized review and signer availability.
Prepare the document
Deliver to signers
Complete signer review
Archive the record
Find and fill out the correct public reporting burden for this collection of information is gsa
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| DD 2535 2023 | 4.8 Satisfied (786 Votes) | |
| DD 2535 2016 | 4.8 Satisfied (9689 Votes) | |
| DD 2535 2010 | 4.7 Satisfied (172 Votes) |
Audit-trail evidence for the GSA statement
The audit trail separates signer activity from document content, creating a reviewable record of authentication, actions, timestamps, and completion.
Authenticate signer:
Capture timestamps:
Protect document:
Seal activity:
Retrieve evidence:
Export records:
Security controls for the GSA record
Data in transit:
Data at rest:
Security reporting:
Information security:
Electronic signatures:
Signing evidence:
Privacy and disclosure pitfalls
The statement may contain agency instructions or respondent information that should not be exposed through an unrestricted signing link. A signer may approve a burden estimate without reviewing the original GSA wording, creating an avoidable source-document discrepancy. Consumer-facing electronic records may require ESIGN consent disclosures and access procedures under 15 U.S.C. §7001(c). Broad workspace permissions can allow an unauthorized user to download the signed statement or its audit trail.
Risks when the record is incomplete
Incomplete record
Attribution dispute
Source mismatch
Weak reproducibility
Legal standing of the electronic record
An electronic GSA burden statement may support a U.S. business transaction when the signer demonstrates intent, consents to electronic records, can be attributed to the signature, and the record remains accurate and reproducible under ESIGN, 15 U.S.C. chapter 96, and applicable UETA law. Wills, codicils, testamentary trusts, court orders, and certain family-law documents remain excluded.

Troubleshooting this GSA burden statement
Resolve field, access, security, and electronic-record questions before submitting the completed GSA burden statement.
The form name does not identify a missing-field error or issuing agency. Upload the source document to signNow, review detected fields, and compare every field against the agency’s original instructions before sending it for signature.
If signNow cannot detect fields, use the editor to add text, date, checkbox, and signature fields manually. The Business plan includes templates and audit trails, helping reviewers distinguish prepared fields from later signer actions.
A completed public-reporting record should preserve signer intent, attribution, timestamps, and a reproducible copy. ESIGN and UETA support electronic records when those requirements are satisfied; signNow audit trails document the signing sequence.
If the document contains federal procurement or agency-sensitive information, confirm the organization’s security requirements before sending. signNow provides TLS 1.2/1.3 in transit, AES-256 at rest, SOC 2 Type II, and ISO 27001 controls.
Business Premium adds bulk send, but this statement should be sent in bulk only when each recipient is authorized to receive the same document. Otherwise, use individual routing and verify recipient identity before delivery.
If a signer cannot open the document, verify the email address, resend the invitation, or provide a signNow signing link through an approved channel. The sender should not alter agency-required language while troubleshooting access.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.