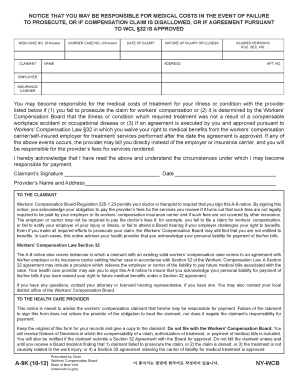
For Medical Orifagreement Form
Use a For Medical Orifagreement Printable template to make your document workflow more streamlined.
What For Medical Orifagreement Form does
For Medical Orifagreement Form is a medical agreement used to document consent, authorization, or another healthcare-related understanding between identified parties. In signNow, the sender uploads the agreement, reviews automatically detected fillable fields, assigns signers, and sends the document through a controlled workflow. Each signer reviews the terms and applies an electronic signature, while signNow records timestamps and document activity in an audit trail. Healthcare organizations should apply HIPAA safeguards and retain the completed record under their applicable policy and 45 CFR §164.530(j).
Who uses medical agreement forms
Healthcare practices
Healthcare practices can use the form for patient agreements, provider acknowledgments, treatment-related consents, and administrative documents requiring an auditable signature process.
Hospitals and centers
Hospitals and specialty centers can route agreements among patients, clinicians, representatives, and administrators while limiting access to authorized participants.
Features that support medical agreements
For Medical Orifagreement Form workflows benefit from structured fields, controlled signer access, audit evidence, and secure handling of completed healthcare documents.
Field detection
Upload the medical agreement and use signNow field detection to identify signature, date, initials, and required completion fields before sending.
Signer routing
Route the agreement to patients, providers, representatives, or administrators in a defined signing order, reducing manual follow-up and misplaced paperwork.
Audit trail
Capture timestamps, signer actions, and document history in an audit trail that helps establish how the agreement was completed.
Signer verification
Use two-factor authentication or SMS OTP when stronger signer attribution is needed for agreements containing protected health information.
Secure storage
Keep completed agreements and their audit records together so authorized teams can retrieve the signed version during review.
System connections
Connect medical agreement workflows with Microsoft 365, Google Drive, Box, or healthcare operations systems through available signNow integrations.
How the medical agreement workflow works
The process moves from document preparation to signer assignment, completion, and organized retention without changing the agreement’s substantive terms.
Upload document: Upload the medical agreement and review detected fields. Map fields: Assign each signature, date, and initials field. Send securely: Send the agreement to the designated signers. Complete record: Store the signed agreement with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete the medical agreement
Prepare For Medical Orifagreement Form in five controlled steps, from upload and field review through signature collection and evidence storage.
Upload form:
Upload the original For Medical Orifagreement Form file. Check fields:
Review detected signature and completion fields. Assign signers:
Assign each field to the correct signer. Send agreement:
Send the agreement through signNow. Store evidence:
Review the completed file and audit trail.
Recommended setup for medical agreements
Use a controlled signing workflow that protects health information, records signer intent, and preserves the completed agreement for the applicable retention period.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication for signers |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled with timestamps and action history |
| Document retention | Six years for HIPAA records |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
Security controls for medical agreements
Stored data:
Transit protection:
HIPAA coverage:
Service controls:
Security management:
Regulated records:
What the audit trail records
The audit trail documents the technical events surrounding completion of For Medical Orifagreement Form, helping reviewers connect signer identity, timing, document integrity, and retrieval history.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log actions:
Export trail:
Retention periods for medical agreement records
Keep the signed agreement and related records according to the rule governing the underlying healthcare, tax, employment, safety, or audit record.
Six years for HIPAA records
Three years for tax records
Three years for payroll records
Five years for injury records
Seven years for audit records
Record-keeping practices for medical agreements
Use a documented retention and access process so each signed medical agreement remains complete, protected, and available for the applicable review period.
Apply the six-year HIPAA retention rule
Export the signed record and audit trail
Protect patient information during storage
Record ownership and legal holds
Risks of mishandling medical agreements
Consent failure
Privacy exposure
Record weakness
Integrity dispute
Retention breach
Key performance indicators that demonstrate SignNow's proven track record.
Questions about completing medical agreements
These answers address field detection, signer verification, healthcare safeguards, electronic-signature validity, and regulated-record requirements for this medical agreement workflow.
signNow Business includes templates, audit trails, mobile apps, and legally binding eSignatures. If the medical agreement requires bulk sending, Business Premium adds bulk send. Confirm the selected plan before preparing repeated patient or provider workflows.
signNow identifies its service as HIPAA compliant, but the product ground truth states that a BAA is required. Confirm that the appropriate BAA and organizational safeguards are in place before sending protected health information through the workflow.
For stronger attribution, use two-factor authentication, SMS OTP, or another available signer-authentication control. Confirm the signer’s identity and preserve the audit trail; an electronic signature alone does not replace identity, consent, or access controls.
Upload the original agreement again, then review detected fields before sending. Check that every signature, date, initials, and required response field is assigned to the correct person. Do not rely on auto-detection without visually reviewing the document.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. Consumer-facing records also require the ESIGN disclosure and access conditions under 15 U.S.C. §7001(c). Review healthcare and state-law requirements separately.
If the agreement is part of a regulated FDA record, confirm whether 21 CFR Part 11 controls apply. signNow identifies 21 CFR Part 11 compliance, but the organization remains responsible for validation, procedures, access controls, and the specific record environment.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.