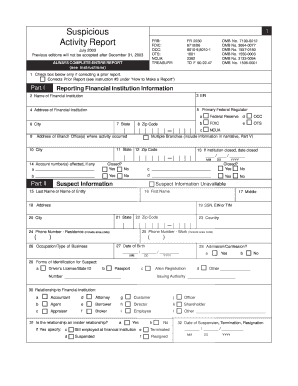
Suspicious Reports Form
Use a Suspicious Reports Form template to make your document workflow more streamlined.
What the Suspicious Reports Form does
The Suspicious Reports Form records facts, supporting details, and review decisions about suspected misconduct or suspicious activity; it is not a universal federal filing form with one nationally defined deadline or issuing agency. In signNow, upload the form, review auto-detected fillable fields, assign investigators and approvers, send it for signatures, and store the completed document with its audit trail. Electronic signatures may be recognized under ESIGN and UETA when intent, consent, attribution, and record retention requirements are met. Confirm the receiving program’s rules before electronic submission.
Who can use this report
Financial services
Compliance teams can route suspicious-activity reports, supporting evidence, and approval records through a controlled signing workflow.
Business operations
Operations and risk teams can collect incident details, reviewer comments, and sign-offs in one auditable document.
Managing report users and permissions
Administrators can publish a controlled Suspicious Reports Form template, assign roles, and limit sending rights so investigators work from an approved document version. Delegated sending helps authorized staff initiate reports without giving every contributor permission to change templates or manage account settings. Reviewers can receive the report in a defined sequence, complete assigned fields, and sign from a browser or mobile app. Admins retain oversight through signNow’s audit trails, shared templates, and user controls, while the organization’s reporting policy determines who may approve or release the final record.
How suspicious reports move through signNow
The signNow workflow turns an uploaded Suspicious Reports Form into a controlled record by preparing fields, routing participants, capturing signatures, and preserving evidence.
Upload report: Upload the report template to signNow. Prepare fields: Review detected fields and add missing assignments. Send securely: Route the report to designated reviewers and signers. Preserve evidence: Store the completed report with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Quick guide to completing the report
Prepare the Suspicious Reports Form in signNow by checking fields, assigning participants, and preserving the final report with its audit evidence.
Upload form:
Upload the current report template to signNow. Check fields:
Review detected fields and add required assignments. Route report:
Send the report to authorized reviewers and signers. Archive evidence:
Download the signed record and audit trail.
Recommended report workflow setup
Configure the Suspicious Reports Form around verified signer identity, traceable review events, controlled access, and a retention policy approved for the applicable reporting program.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail and encryption | Detailed history with AES-256 protection |
| Document retention | 3 years from filing (IRC §6501(a)) |
| User provisioning | Admin-managed roles and shared templates |
How signNow records suspicious reports
The signNow audit trail preserves technical evidence showing who handled the Suspicious Reports Form, when each action occurred, and whether records changed.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Event logging:
Audit retrieval:
Features for suspicious reports
signNow combines field preparation, controlled routing, signer verification, and audit evidence so teams can complete Suspicious Reports Form records consistently.
Field detection
Upload the Suspicious Reports Form and use signNow’s field detection to identify spaces for report details, dates, signatures, and reviewer approvals before sending.
Role-based routing
Assign each signer and reviewer in order so the report reaches the correct people without manually forwarding files or losing version control.
Audit trail
Capture email, authentication, timestamps, actions, and document history in an audit trail that supports internal review and record reproduction.
Secure storage
Keep the completed report and its signing evidence together, reducing the risk of separating an approval from the underlying suspicious-activity record.
Signer verification
Use SMS verification or other available authentication controls when the report contains sensitive financial, personal, or incident information.
Reusable templates
Send a reusable report template to authorized teams, keeping required fields and approval steps consistent across investigations.



Security for suspicious reports
Transport encryption:
Stored data:
Security certification:
Information security:
Health data:
Electronic records:
Processing stages for suspicious reports
Processing time depends on report completeness, reviewer availability, and the reporting authority’s requirements; signNow records each workflow stage.
Document preparation
Delivery to signers
Signer turnaround
Completion and archival
Privacy pitfalls in suspicious reports
Personal identifiers or financial details may appear in report attachments, so limit access and avoid sending completed records through unsecured email threads. A missing consent disclosure can weaken a consumer-facing electronic record under 15 U.S.C. §7001(c), even when the signature event is captured. Incorrect signer roles can leave investigator findings unsigned or route approval to someone without authority under the organization’s reporting policy. Changing a completed report without preserving its audit trail can create uncertainty about which facts and approvals belonged to the original submission.
Suspicious Reports Form troubleshooting
Resolve field, signer, consent, plan, and retention questions before treating a completed Suspicious Reports Form as ready for regulatory or internal use.
signNow’s field-detection workflow can identify fillable areas after upload, but review every detected field against the Suspicious Reports Form before sending. Add missing signature, date, narrative, or reviewer fields manually, then test the completed template with a non-production copy.
Use signNow’s signer roles and routing order to assign the report to the correct investigator, reviewer, and approver. Confirm each recipient’s email address before sending; changing the recipient after dispatch may require a corrected envelope and a new audit trail.
The Business plan includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR features. Business Premium adds bulk send, while Enterprise adds advanced signer authentication and conditional or formula fields.
For consumer-facing electronic records, obtain consent and provide the ESIGN consumer disclosure required by 15 U.S.C. §7001(c). Confirm the signer can access the electronic format and understands how to withdraw consent before relying on electronic delivery.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. They do not automatically authorize electronic filing with a regulator, so verify the receiving agency’s submission rules separately.
Export the completed report and audit trail from signNow, then apply the retention rule for the underlying record. Federal tax records generally use three years from filing under IRC §6501(a), but the applicable suspicious-reporting program may require a different period.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.