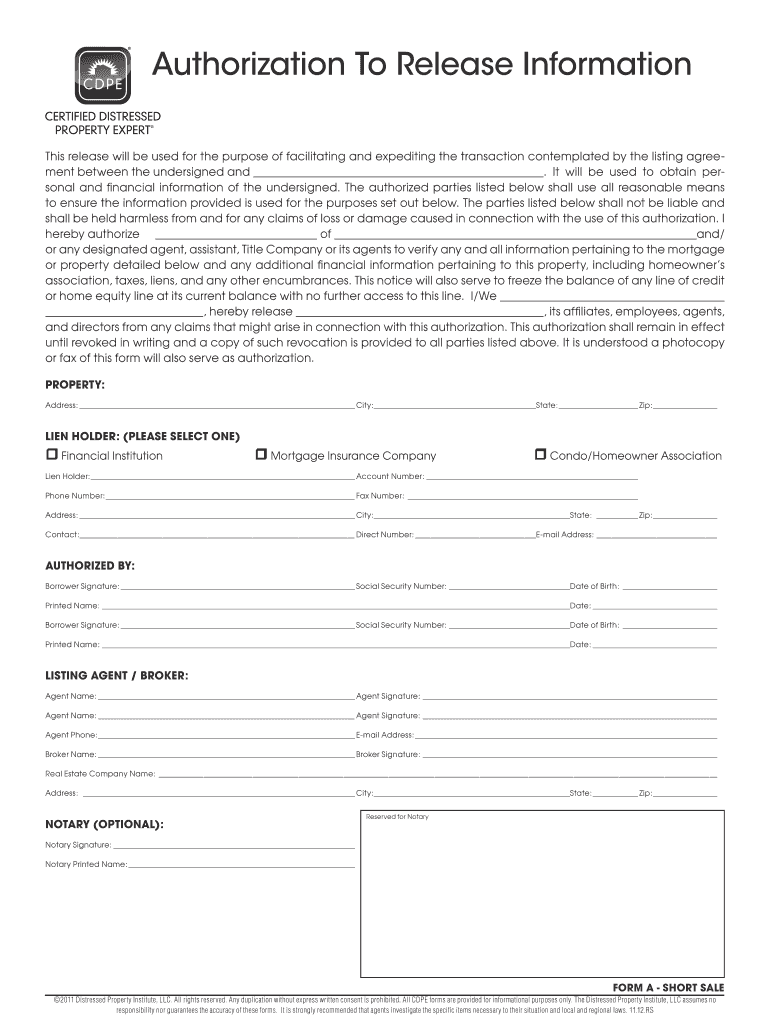
Authorization To Release Information Form Cdpe
Use a Authorization To Release Information Form Cdpe template to make your document workflow more streamlined.
What this authorization form does
An Authorization To Release Information Form Cdpe gives a named person or organization permission to disclose specified information to an identified recipient. The signer should review the information categories, recipient, purpose, expiration or revocation terms, and required signature fields before signing. With signNow, the sender uploads the form, reviews detected fillable fields, adds signer roles, sends it electronically, and retains the completed record with an audit trail. HIPAA, FERPA, contract terms, and state law may impose additional requirements depending on the information released.
Who uses authorization release forms
Healthcare providers
Healthcare providers and medical practices can use Authorization To Release Information Form Cdpe workflows to obtain a patient’s permission before sharing designated records. The form should identify the patient, recipient, information scope, expiration or revocation terms, and signer. HIPAA-covered workflows require appropriate privacy controls and a business associate agreement where applicable.
Business records teams
Attorneys, property managers, and financial services teams can route authorization forms to clients or account holders before releasing records. Templates can standardize recipient details, permitted disclosures, dates, and signatures, while the completed document and audit trail provide a retrievable record for internal review.
How the authorization workflow works
The workflow moves from document preparation to recipient signing, then preserves the completed authorization and signing history.
Upload form: Upload the authorization form into signNow. Check fields: Review detected fields and add missing signature details. Send securely: Send the completed authorization to designated recipients. Archive record: Store the signed form with its audit trail.
Features for authorization release forms
signNow supports the document preparation, recipient routing, signing evidence, and record-handling needs of Authorization To Release Information Form Cdpe workflows.
Field review
Upload the authorization form and review detected fields before adding signer assignments, reducing omissions in names, dates, consent language, and signatures.
Role routing
Route the authorization to the person granting permission and the intended recipient, preserving role order and reducing unauthorized disclosure.
Audit trail
Capture signer actions, timestamps, and document history so reviewers can examine how the authorization was completed.
Reusable templates
Use reusable templates for recurring authorization requests while updating recipient, purpose, information scope, and expiration details for each transaction.
Remote signing
Send signing requests from desktop or mobile workflows when patients, clients, or account holders cannot attend an office appointment.
Record retention
Retain a completed authorization with its associated signing evidence for later privacy, legal, or internal review.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Configure the Authorization To Release Information Form Cdpe workflow around verified signers, controlled access, audit evidence, and the applicable record-retention policy.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Require verified email and role-based access |
| Signature type | Use an electronic signature with signer intent |
| Audit trail | Retain the completed audit trail |
| Document retention | Apply the organization’s approved retention policy |
| Encryption | Use TLS in transit and AES-256 at rest |
What the audit trail records
A signNow audit trail supplements the Authorization To Release Information Form Cdpe with technical evidence about identity, timing, document integrity, and access.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Export trail:
Examples of authorization workflows by industry
Healthcare and property teams use authorization forms to document permission before releasing records or transaction information.
Healthcare authorization
Fertility Centers of Illinois needed a secure way to collect patient authorizations and related healthcare documents remotely.
- Collect patient authorization signatures online
Fertility Centers of Illinois selected airSlate SignNow for its responsive API and healthcare workflows. When an authorization form contains protected health information, the organization should configure a HIPAA-compliant deployment and execute the required business associate agreement before sending records.
Real estate records
Martin Properties handles signed documents across property transactions, where authorization forms may accompany disclosures or records requests.
- Process authorization documents on mobile
Martin Properties reports processing documents online, on mobile, and offline while maintaining built-in security. For an authorization form, a reusable template, clear recipient roles, and a completed audit trail can reduce missing signatures and preserve evidence of the signing event.
Privacy and disclosure pitfalls
Listing a broad information category can authorize disclosure beyond the signer’s intended records or stated purpose. Sending protected health information without confirming the recipient and HIPAA workflow can create an unauthorized disclosure. Failing to capture electronic consent can weaken evidence that the signer agreed to use a digital record. Leaving completed authorizations in unrestricted folders can expose personal information to unauthorized staff or recipients.
Legal standing and evidence
An electronically signed Authorization To Release Information Form Cdpe may be admissible when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible. ESIGN and UETA support electronic transactions, but they exclude wills, certain court filings, and family law decrees. State requirements and the form’s issuing authority still control.

Best practices for completing the form
Accurate scope, verified recipients, appropriate authentication, and controlled retention reduce disclosure errors when Authorization To Release Information Form Cdpe is signed electronically.
Limit the release scope precisely
Review every field before sending
Match authentication to sensitivity
Preserve the signed record securely
Security and data protection
Transport encryption:
Storage encryption:
SOC 2 Type II:
ISO 27001:
HIPAA:
ESIGN and UETA:
Authorization form troubleshooting
These answers address field detection, privacy controls, legal validity, plan capabilities, and recipient access for this authorization workflow.
On the Business plan, upload Authorization To Release Information Form Cdpe, inspect the detected fields, and manually add missing signature, date, or consent fields before sending. The sender remains responsible for confirming that the form’s release scope and recipient details are accurate.
The Business Premium plan includes bulk send, but each authorization should still receive the correct patient, client, recipient, purpose, and expiration information. Use bulk sending only when the form content and routing are genuinely uniform; otherwise, prepare separate document fields.
signNow states that HIPAA compliance is available with a business associate agreement. For an authorization containing protected health information, confirm the applicable covered-entity workflow, execute the required agreement, and limit access to authorized users before sending.
ESIGN and UETA recognize electronic signatures when intent, consent, attribution, and record reproduction are established. For a consumer-facing authorization, provide the required electronic-record disclosure and ensure the signer can access the record before signing.
Business plans include audit trails and templates. If the workflow requires advanced signer authentication, formula fields, conditional fields, SSO, or expanded API controls, review Enterprise or Site License capabilities against the organization’s requirements.
If a recipient cannot access the request, verify the email address, resend the invitation, or provide a signNow signing link when appropriate. Confirm identity and recipient authority before sharing an authorization containing personal or protected information.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.