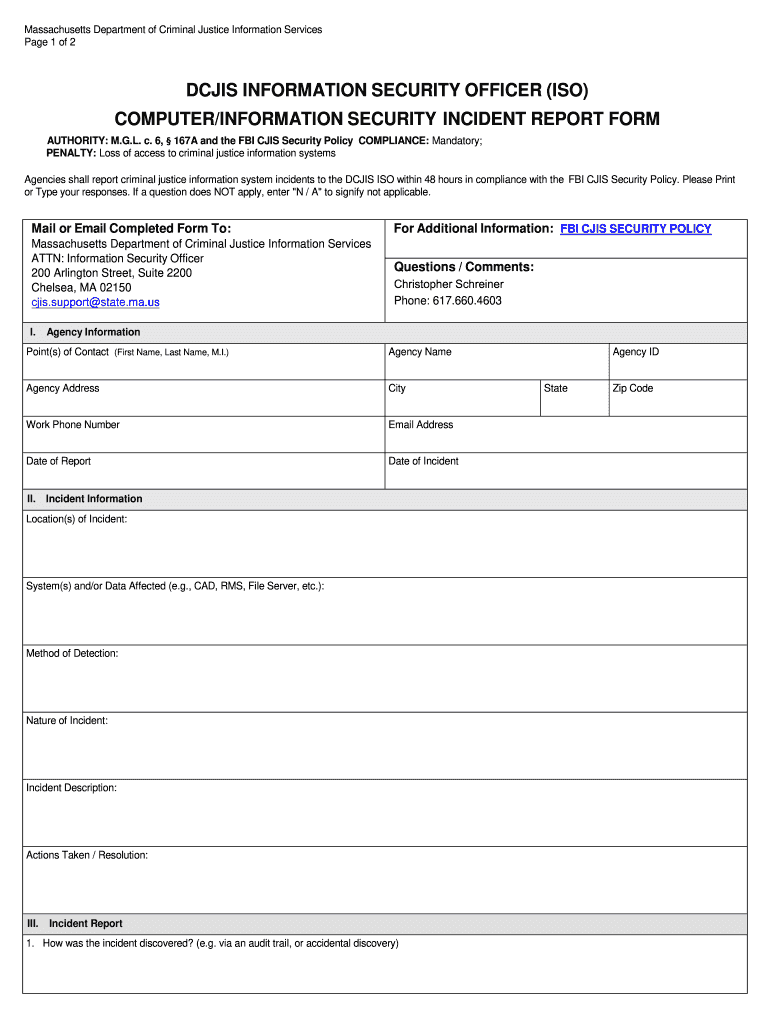
Ncja Security Incident Report Form
Use a NCJA Security Incident Report Form template to make your document workflow more streamlined.
Ncja Security Incident Report Form overview
Ncja Security Incident Report Form records what happened during a security event, who reviewed the facts, which actions were taken, and when responsible participants approved the record. With signNow, a sender uploads the report, reviews auto-detected fillable fields, assigns incident details and signature fields, and sends the document to authorized participants. Signers review and complete their assigned sections, while signNow records actions, timestamps, and authentication details in an Audit Trail. The completed PDF and audit evidence can then be retained under the organization’s incident-response policy.
Who uses this incident report form
Security teams
Security and privacy teams can document suspected incidents, assign review responsibilities, capture acknowledgments, and preserve signed evidence without circulating uncontrolled email attachments.
Regulated organizations
Healthcare, education, finance, and government organizations can adapt the form for sensitive events while applying access controls and sector-specific retention policies to completed records.
Teams managing incident report permissions
Security administrators can create shared incident-report templates, define required fields, and limit editing or sending permissions while preserving a consistent response record across departments. Privacy and legal teams can use delegated sending to route reports for review, require specific signers, and manage access through centralized administrator controls.
Features for completing incident reports
Ncja Security Incident Report Form workflows combine accurate field completion, controlled routing, signer authentication, and preserved evidence for U.S. security-response teams.
Field detection
Upload the incident report and let signNow detect fillable areas, reducing manual field placement before security, privacy, or legal review begins.
Role-based routing
Assign incident details, attestations, and signatures to named participants so each person completes only the information relevant to their role.
Audit Trail
Capture timestamps, signer actions, and authentication details in an Audit Trail that supports internal investigation and later review.
Signer authentication
Use SMS codes or other available authentication controls when incident evidence requires stronger attribution than an email link alone.
Signed records
Preserve the finalized incident report as a signed PDF with its completion evidence, supporting controlled archival and retrieval.
Connected storage
Connect completed reports with services such as Google Drive, Box, or Microsoft 365 for governed storage and downstream response workflows.
How the incident report workflow works
signNow turns the incident report into a controlled workflow from field detection through signatures, audit evidence, and secure record storage.
Upload the form: Upload the incident report template to signNow. Review fields: Auto-detect fields and verify each incident detail. Route for signatures: Send assigned sections to authorized signers. Archive evidence: Store the signed report with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Quick steps for completing the report
Prepare the report in signNow, verify each incident detail, route it to authorized participants, and preserve the completed evidence package.
Upload:
Upload the completed incident report template. Check fields:
Confirm detected fields and required evidence. Assign roles:
Assign each signer and reviewer. Send:
Send the report through signNow. Verify:
Review the signed PDF and Audit Trail.
Recommended incident report setup
Configure the report around signer attribution, evidence preservation, controlled access, and the retention rule attached to the incident data.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for sensitive incidents |
| Signature type | Intent-confirming electronic signature |
| Audit trail | Export with completed signed PDF |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 |
Authentication and certificates for reports
Certificate-based signing:
Digital certificate support:
Stronger signer verification:
One-time code delivery:
Identity proofing options:
Timestamped signing history:
What the incident report audit trail records
The Audit Trail preserves technical evidence around the report’s signing events without replacing the organization’s substantive incident investigation.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Retrieve evidence:
Export audit trail:
Record-keeping practices for incident reports
Preserve the completed report, evidence, and audit history according to the incident’s data category and applicable U.S. retention rule.
Apply the correct retention period
Export the complete audit trail
Archive reports securely
Minimize retained personal information
Privacy pitfalls in incident reporting
Incident reports may expose names, contact details, credentials, or medical information when broad recipients receive the completed PDF. Missing consent language can weaken the record when the report collects information from employees, customers, patients, or witnesses. Sharing a signing link publicly can let an unauthorized person access or complete sensitive incident information. Unrestricted downloads can place signed reports and audit trails in personal storage outside the organization’s security controls.
Risks of incomplete incident records
Unclear signer identity
Electronic-record dispute
Privacy investigation
Unavailable evidence



Legal standing of incident reports
A signed Ncja Security Incident Report Form can support U.S. business records when the signer shows intent, consents to electronic records, can be attributed, and the record remains reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA law. Wills, codicils, testamentary trusts, court filings, and family-law decrees are excluded.

Troubleshooting incident report workflows
Use these answers to resolve field, identity, consent, access, retention, and plan questions before the incident report enters the organization’s official record.
Upload the original incident report PDF to signNow, then review auto-detected fields manually. Detection does not determine whether a field is legally required, so compare every field with your organization’s incident-response policy before sending.
On the Business plan, use available signer authentication and Audit Trail controls to attribute actions. For higher-risk incidents, configure stronger authentication where available and confirm that the selected control fits your internal evidence policy.
signNow supports ESIGN and UETA requirements, but legal validity still depends on intent, consent, attribution, and record retention. For consumer-facing records, provide the electronic-record disclosure required by 15 U.S.C. §7001(c).
A signing link should be shared only with its intended participant. If the link was exposed, cancel or replace the request, verify completed actions in the Audit Trail, and document the access incident separately under your response procedure.
HIPAA-covered documentation must be retained for six years from creation or the last effective date under 45 CFR §164.530(j). The organization must also protect access and verify whether state law requires a longer period.
The Business plan includes templates and Audit Trails; Business Premium adds bulk send, while Enterprise adds advanced signer authentication. Select the plan based on the number of reports, authentication needs, and workflow controls required.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.