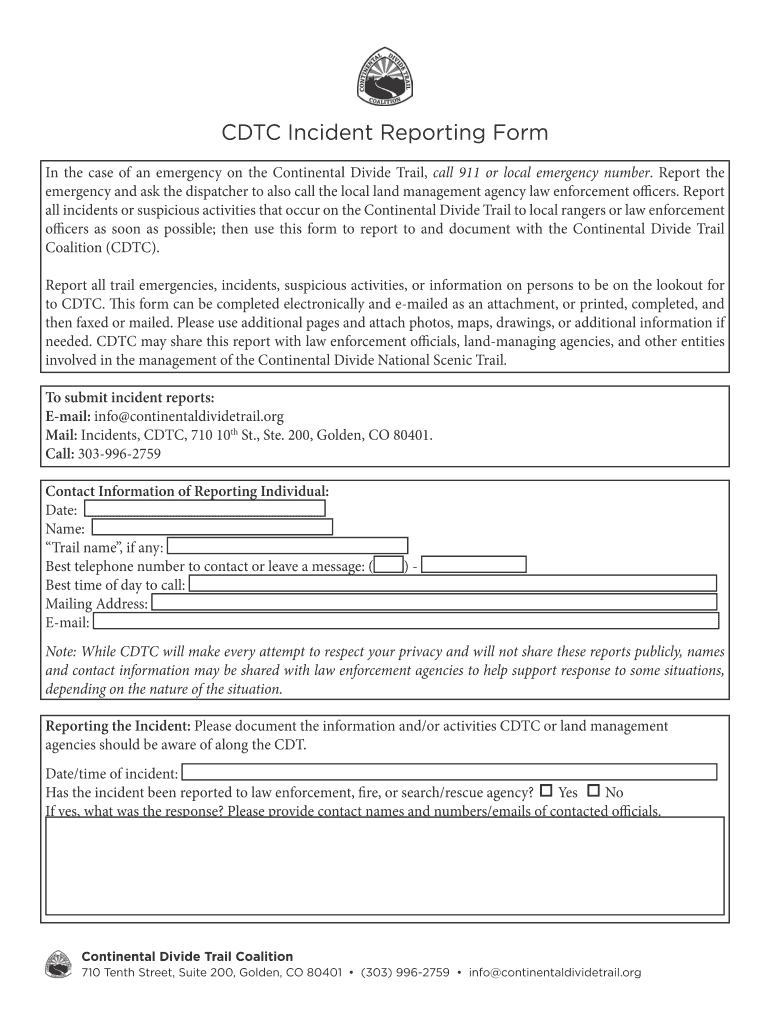
Cdtc Incident Reporting Form
Use a CDTC Incident Reporting Form template to make your document workflow more streamlined.
What the Cdtc Incident Reporting Form records
The Cdtc Incident Reporting Form is a structured record for documenting an incident, the people involved, the relevant date and location, observed facts, immediate actions, and follow-up decisions. Its exact fields depend on the issuing organization’s template, so users should complete every applicable field without guessing missing information. In signNow, a sender uploads the form, reviews detected fillable fields, adds recipients, and routes the report for review or signature. The completed PDF and audit trail can then be retained under the organization’s records policy.
Key features for Cdtc incident reports
signNow connects form preparation, recipient routing, electronic signing, and evidence preservation around the Cdtc Incident Reporting Form.
Field detection
Upload the Cdtc Incident Reporting Form and let signNow identify available fillable areas before routing the report for review or signature.
Recipient routing
Send the report to named recipients in the required order, reducing manual email handling for incident documentation.
Electronic signing
Use typed, drawn, or click-to-sign methods when the organization’s policy permits electronic signatures for the report.
Audit trail
Capture signer identity, timestamps, and activity in an audit trail connected to the completed report.
Mobile access
Review and sign from signNow mobile apps on supported iOS and Android devices when incident work occurs away from a desk.
Record retention
Preserve the finalized report and related audit evidence according to the applicable records policy and legal retention rule.
How to complete the Cdtc Incident Reporting Form
Complete the Cdtc Incident Reporting Form in signNow by preparing the report, routing it for review, and preserving the signed record.
Upload the form: Upload the completed Cdtc Incident Reporting Form template to signNow. Check form fields: Review detected fields and add missing incident details. Send for signature: Send the report to designated reviewers or signers. Archive the record: Store the completed report with its audit trail.
What the Cdtc audit trail records
The audit trail adds evidence around the Cdtc Incident Reporting Form rather than replacing the report’s factual content.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Authentication options for incident reports
Signer authentication:
Two-factor authentication:
Identity verification:
PKI signatures:
X.509 certificates:
Signing evidence:
Recommended Cdtc reporting workflow setup
Configure the Cdtc Incident Reporting Form around verified signer identity, traceable actions, protected transmission, and a documented retention decision.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Export with completed report |
| Document retention | Apply the documented subject-specific rule |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
Platform requirements for Cdtc Incident Reporting Form
Cdtc Incident Reporting Form workflows require an internet-connected device using TLS 1.2 or TLS 1.3, with Chrome, Firefox, Safari, or Edge. signNow also provides mobile apps for iOS and Android, allowing authorized users to review and sign the report from supported phones or tablets.
Browser support Chrome, Firefox, Safari, and Edge on desktop browsers. Operating systems Windows 10, macOS, iOS, and Android devices. Mobile access signNow mobile apps support form review and signing.
Organizations should manage access through approved Windows, macOS, iOS, or Android devices and apply their own controls for sensitive incident information. Enterprise deployments may configure API access, SSO provisioning, managed-device policies, and certificate or long-term-validation requirements according to the organization’s security and records policy.
Common Cdtc reporting challenges
Reporters omit the incident time, location, witnesses, or immediate response, leaving reviewers unable to reconstruct what happened. Narratives mix observed facts with assumptions, opinions, or later conclusions that should be documented separately. Recipients receive the Cdtc Incident Reporting Form before required fields are completed, creating avoidable review cycles. Completed reports are saved without the audit trail, weakening evidence of who signed and when.
Risks of incomplete incident reporting
Incomplete incident record
Weak signer attribution
Insufficient audit evidence
Access control failure
Best practices for Cdtc incident records
Accurate facts, controlled routing, complete evidence, and a documented retention decision make the report easier to review and defend.
Record facts before sending
Assign recipients by responsibility
Preserve the audit package
Document the retention rule
Retention periods for incident reports
The correct retention period depends on what the Cdtc Incident Reporting Form documents and which legal rule applies.
5 years for OSHA injury records
30 years for OSHA exposure records
6 years for HIPAA records
3 years for federal tax records
Policy period for other reports
Cdtc Incident Reporting Form troubleshooting
Use these answers to resolve field, routing, authentication, compliance, and record-preservation questions without altering the original incident evidence.
Upload the original Cdtc Incident Reporting Form again and check whether its PDF contains selectable fields. If fields are not detected, add them manually in signNow before sending. Do not rely on visual boxes that cannot receive typed data or signatures.
The Business plan includes templates, audit trails, and legally binding eSignatures. If the workflow requires bulk sending of the Cdtc Incident Reporting Form, Business Premium adds bulk send and quick invite links.
Use signNow’s recipient routing and signer authentication options to identify the person completing the report. For stronger attribution, enable SMS OTP or another available verification method and retain the resulting audit trail.
Electronic signatures generally receive legal recognition under ESIGN and applicable UETA rules when intent, consent, attribution, and record retention requirements are satisfied. Check the issuing organization’s policy before using an electronic signature for this form.
signNow states that its HIPAA compliance requires a business associate agreement. If the Cdtc report contains protected health information, confirm the BAA, access controls, and six-year HIPAA retention requirement under 45 CFR §164.530(j).
If a report was sent to the wrong recipient, cancel or correct the workflow according to internal policy, restrict access, and preserve the event history. Create a corrected report rather than silently changing a completed record.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.