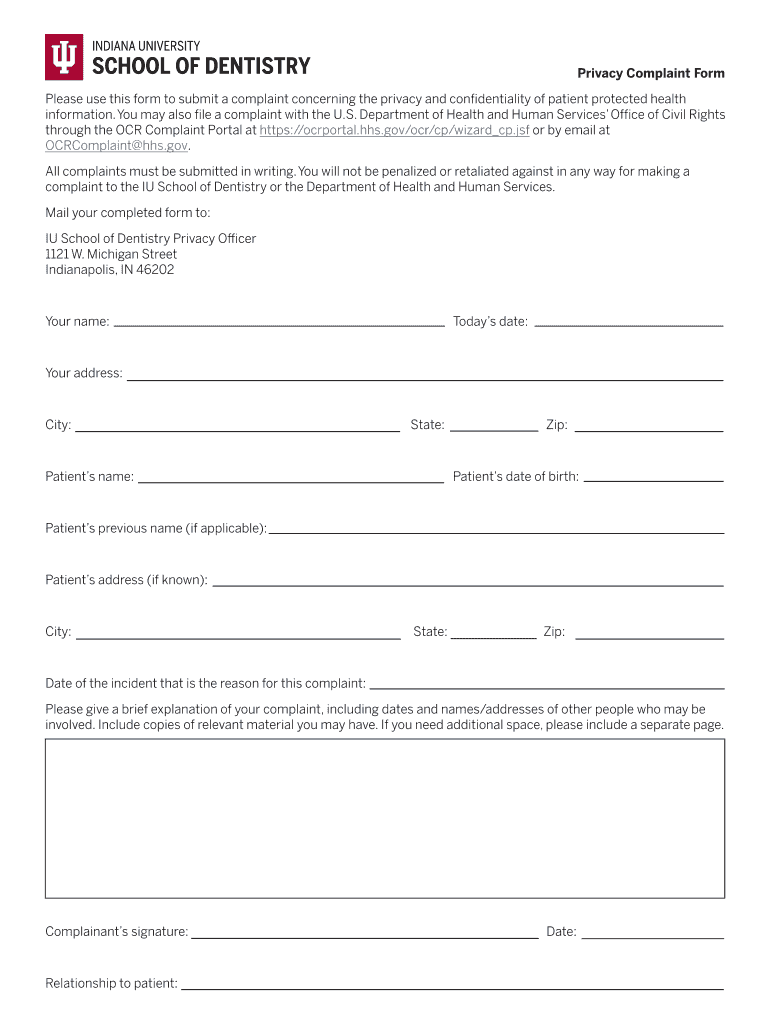
Test Privacy Complaint Form
Use a Test Privacy Complaint Form template to make your document workflow more streamlined.
What the complaint form does
A Test Privacy Complaint Form records a person’s concern about how an organization collected, used, disclosed, stored, or accessed personal information. It gives the complainant a structured place to identify themselves, describe the incident, provide dates and affected data, attach supporting material, and request a response. With signNow, a sender uploads the form, auto-detects fillable fields, adds signer and authentication requirements, sends it for completion, and stores the signed PDF with its audit trail. The form itself does not decide whether a complaint is legally valid; the organization must review it under its privacy policy and applicable U.S. law.
Who benefits from this complaint form
The form supports privacy intake for individuals, regulated teams, and organizations that need a structured, reviewable complaint record.
Solo practitioners can use the form to collect a complainant’s account, requested remedy, and supporting files without building a separate intake workflow. A controlled signNow template keeps the complaint structure consistent while allowing the practitioner to review each submission personally before responding. Healthcare practices can route privacy complaints containing protected health information to designated privacy personnel. A HIPAA-compliant signNow workflow requires a business associate agreement and should limit access, capture consent, and preserve the completed complaint with its audit trail. Enterprises can standardize complaint intake across departments by using shared templates, role-based access, and delegated sending. Privacy teams can separate intake from investigation while retaining a consistent signed record and documented authentication history.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How this complaint workflow works
The signNow workflow turns a blank complaint form into a controlled intake record without changing the organization’s review obligations.
Upload and detect: Upload the Test Privacy Complaint Form and let signNow identify its fillable fields. Configure roles: Assign complaint fields, signature fields, and review access to the correct people. Collect the signature: Send the form by email or signing link; the complainant reviews and signs electronically. Preserve evidence: Store the completed PDF with its audit trail for privacy review and records management.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete the complaint form
Follow these steps to prepare, sign, and preserve a Test Privacy Complaint Form in signNow.
Upload:
Upload the complaint form. Detect fields:
Let signNow detect fillable fields. Assign roles:
Add the complainant and reviewer. Send:
Send for secure completion. Archive:
Review and store the signed record.
Challenges when completing the form
Complaint narratives can include excessive personal information, creating unnecessary disclosure risk when the completed form is shared with reviewers or external recipients. A missing incident date, affected data category, or contact detail can prevent privacy staff from identifying the complaint and requesting an effective response. Sending the form to an unverified email address can expose sensitive allegations and weaken evidence that the identified person authorized the submission. Separating the signed complaint from its audit trail makes later verification harder, especially when reviewers need timestamps, authentication events, or completion history.
Recommended complaint form setup
Use a controlled workflow that verifies the complainant, limits disclosure, preserves evidence, and routes the completed form to designated privacy personnel.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retain completion history and signer events |
| Document retention | Follow the organization’s privacy retention schedule |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
Best practices for privacy complaints
Accurate fields, controlled disclosure, and a preserved audit trail make a Test Privacy Complaint Form easier to review and substantiate.
Confirm complaint details before sending
Match authentication to sensitive information
Preserve the complete complaint record
Review the final record carefully
Security for privacy complaints
Digital certificate support:
Certificate-based identity:
Additional signer verification:
Phone-based confirmation:
Signer identity checks:
Protected signed documents:
Limits and state-specific requirements
State law
Notarization
Wills
Court documents
Real-estate deeds
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting the complaint workflow
These answers address field detection, signer access, plan selection, privacy controls, and the legal handling of completed complaint records.
If signNow does not detect the complaint fields, open the uploaded PDF in the editor and place text, date, attachment, initials, and signature fields manually. Save the corrected template before sending it to a complainant. Avoid asking recipients to type sensitive information into an unprotected email.
The Business plan includes legally binding eSignatures, audit trails, templates, and mobile apps. If the workflow requires bulk sending of identical complaint forms, Business Premium adds bulk send; select the plan based on actual volume and access controls.
Use signNow’s audit trail to preserve timestamps, actions, and signer events with the completed complaint. ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention requirements are satisfied; the organization remains responsible for its privacy procedures.
For complaints containing protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm that agreement and configure access, authentication, and retention controls before routing the form through a healthcare workflow.
If a complainant cannot access the signing email, verify the address, resend the invitation, or use a controlled signing link. Do not forward sensitive complaint details through an unverified address while troubleshooting delivery.
SignNow protects data in transit with TLS 1.2/1.3 and at rest with AES-256, according to its compliance information. Encryption does not replace access governance, accurate recipient selection, consumer disclosures, or the organization’s retention policy.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.