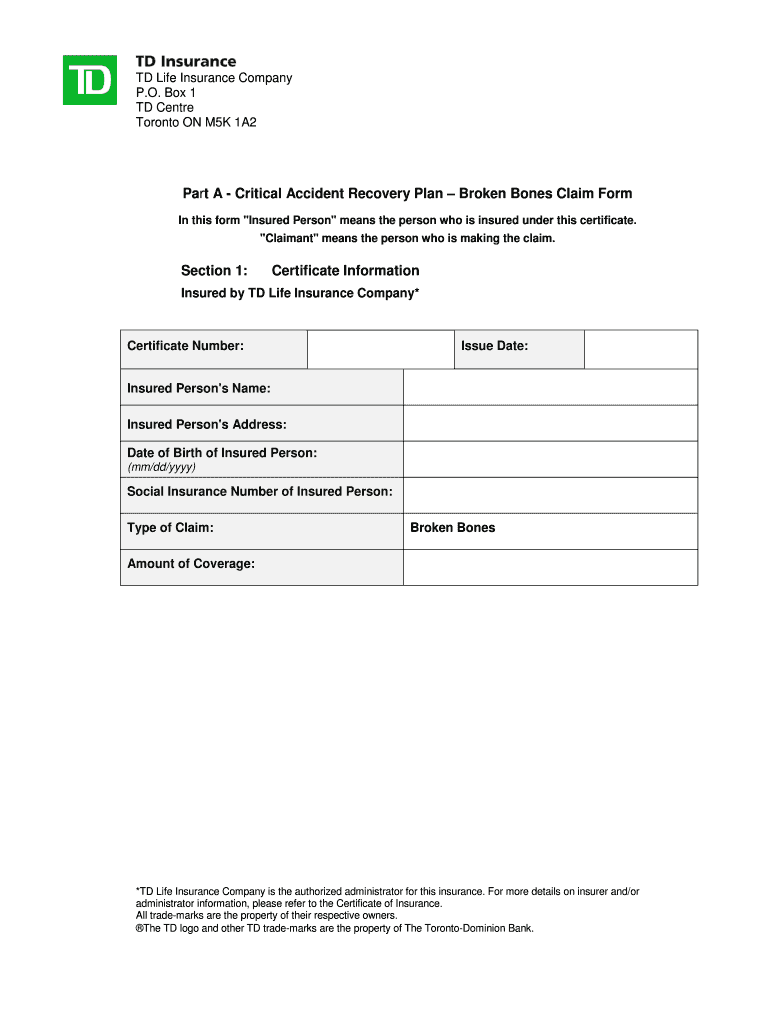
Instructions For Completing The Critical Accident Recovery Plan Form
Use a Instructions For Completing The Critical Accident Recovery Plan template to make your document workflow more streamlined.
What this accident recovery plan does
Instructions For Completing The Critical Accident Recovery Plan Form is a structured record for documenting actions after a critical accident and coordinating the recovery response. Complete the form with the incident facts, responsible people, corrective actions, approvals, and dates required by the organization. Upload the document to signNow, review the detected fields, and assign each signature or acknowledgment to the correct participant. The completed file and audit trail provide a reproducible record of who acted, when, and what version was signed.
How to complete the recovery plan
Complete the plan in signNow by uploading the document, checking detected fields, routing it to participants, and preserving the signed record.
Upload document: Upload the completed accident recovery plan and let signNow detect fillable fields. Review fields: Review detected fields and correct labels, dates, initials, or signature placements. Send for signing: Send the plan to responsible participants in the required signing order. Store record: Store the completed plan with its signNow audit trail and completion certificate.
What the audit trail records
The signNow audit trail documents the identity, timing, document history, and completion evidence associated with this recovery plan.
Authenticate signer:
Capture timestamps:
Seal record:
Export history:
Preserve evidence:
Review trail:
Platform requirements for the plan
Use signNow in Chrome, Firefox, Safari, or Edge on Windows or macOS. The signNow mobile apps support iOS and Android, while TLS 1.2 or 1.3 protects transmitted data.
Browser support Chrome, Firefox, Safari, and Edge on Windows or macOS. Mobile access signNow mobile apps for iOS and Android devices. Secure connection TLS 1.2 or 1.3 protects data during transmission.
Organizations should use managed Windows, macOS, iOS, or Android devices when the plan contains sensitive accident information. Configure access controls, SSO provisioning, API connections, and certificate or long-term validation settings according to internal policy and applicable state requirements.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Privacy and disclosure pitfalls
Including medical details without limiting access can expose sensitive personal information to unintended recipients. Missing participant consent or acknowledgment fields can weaken evidence that each person reviewed the recovery instructions. Assigning a supervisor’s signature field to another participant can create an attribution dispute during later review. Sending the completed plan through an uncontrolled link can prevent reliable access revocation and recipient tracking.
Recommended recovery-plan setup
Configure the workflow around participant identity, signature attribution, audit evidence, secure transmission, and the organization’s approved incident-record policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and event history |
| Document retention | Follow the organization’s incident-record policy |
| Encryption | Use TLS 1.2 or 1.3 and AES-256 |
Recovery-plan processing milestones
The form has no universal federal signing deadline in the supplied authority; use the organization’s incident-response timetable and applicable state requirements.
Prepare the document
Deliver to signers
Obtain acknowledgments
Complete and archive
Best practices for completing the plan
Accurate field assignment, controlled access, and preserved audit evidence make the completed recovery plan easier to review and defend.
Reconcile facts before routing
Assign role-specific fields
Archive the evidence package
Check applicable state rules



Legal standing of the signed plan
For a U.S. business record, an electronic signature may carry the same legal effect as a handwritten signature under ESIGN, 15 U.S.C. chapter 96, and applicable state law such as UETA when intent, consent, attribution, and record retention are established. Those laws exclude wills, certain court filings, and family law decrees.

Troubleshooting the recovery-plan workflow
These answers address field detection, signer identity, plan limits, audit evidence, and compliance questions that arise when completing this specific recovery plan.
Business plan users can upload the recovery plan, place fields, send it for signing, and retrieve the completed document with its audit trail. If the form contains advanced conditional or formula fields, Enterprise adds those capabilities.
Review every automatically detected field before sending. Move signature, date, initials, and acknowledgment fields to the correct lines, then assign each field to the intended participant. Detection accelerates setup but does not replace document-specific review.
Use SMS OTP or another available authentication control when the recovery plan contains sensitive incident information. signNow’s Enterprise plan adds advanced signer authentication; apply internal identity-verification rules consistently.
A signed plan may be admissible under ESIGN and applicable state law when intent, consent, attribution, and record retention are established. The audit trail supports evidence but does not determine whether the underlying accident procedure complied with state law.
Business includes legally binding eSignatures, audit trails, templates, and mobile apps at $8 per user per month with annual billing. Paid plans include 100 signature invites per user per year, with overage fees applying under subscription plans.
If the plan documents protected health information, signNow identifies HIPAA compliance as requiring a BAA. Confirm that the organization has the required BAA and access controls before routing medical information through the workflow.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.