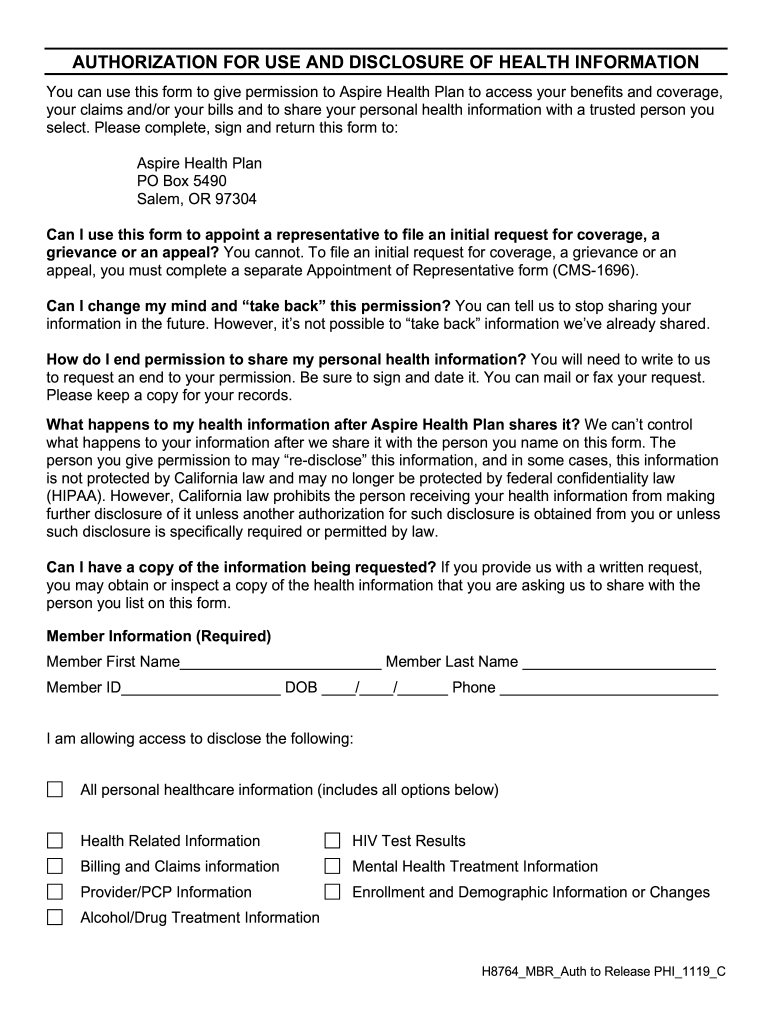
H8764MSAuth To Release PHI1119 Final Authorization To Disclose Health Information
Use a H8764MSAuth To Release PHI1119 FINAL Authorization To Disclose Health Information template to make your document workflow more streamlined.
What this PHI authorization form does
This form authorizes a defined person or organization to disclose specified protected health information to a named recipient. It identifies the patient, records or information covered, disclosure purpose, recipient, signer, and authorization limits. A healthcare organization should review the form for required elements under HIPAA and applicable state law before use. With signNow, the sender uploads the authorization, places or confirms fields, sends it to the patient or representative, captures the signature, and stores the completed document with an audit trail. The signed record supports evidence of consent but does not replace the organization’s privacy, access, and disclosure procedures.
Who uses this PHI authorization form
Healthcare providers
Healthcare providers use this authorization to identify the patient, specify permitted PHI, name recipients, and document the purpose and expiration of disclosure. It supports patient requests involving medical records, treatment coordination, insurance administration, and other authorized healthcare workflows while keeping the release scope clear for reviewers.
Patients and representatives
Patients and authorized representatives use this form to approve a defined release of protected health information. The document helps recipients understand which records may be disclosed, to whom, for what purpose, and for how long, supporting controlled communication between providers, insurers, attorneys, and patients.
How the authorization workflow works
The workflow moves from document preparation to consent capture, signature, and controlled retention for this PHI release authorization.
Upload form: Upload the authorization document to signNow for preparation. Add details: Review detected fields and add patient, recipient, and signer information. Request signature: Send the authorization to the required signer through a secure invitation. Archive record: Store the completed release with its audit trail and signed copy.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete the authorization
Prepare the authorization carefully, then use signNow to collect consent and preserve the completed release record.
Prepare form:
Upload the completed authorization template to signNow. Review scope:
Check patient, recipient, purpose, and expiration fields. Assign signer:
Assign the patient or representative as signer. Complete workflow:
Send, monitor, and download the signed record.
Managing roles and permissions for this form
An administrator can maintain the authorization template, define required fields, and limit editing rights. Delegated senders then prepare patient-specific copies without changing the approved language, while role-based access helps restrict PHI visibility to authorized team members only. The audit trail records each completed transaction for review and retention decisions. These controls support consistent handling across clinics and departments without making every sender a template administrator, reducing accidental changes to the release scope and recipient details. They should be aligned with the organization’s HIPAA security policies and access procedures where applicable. This approach keeps patient authorizations consistent while preserving operational flexibility for authorized staff members who send forms regularly during care coordination and records requests processes each day securely and consistently across participating teams and locations with documented oversight and accountability built into the process for every authorization transaction handled by the organization securely and consistently over time with proper administrative review and access governance controls in place for staff members handling protected health information daily and routinely throughout the organization’s authorized disclosure operations and records management program requirements and procedures for all participants involved in each request and release workflow across departments and service lines with clear role separation and documented approval processes for all users handling this form and its supporting records securely under applicable privacy and security obligations and internal policies for the organization’s healthcare administration operations and patient communications activities involving authorized disclosures and requests from patients representatives providers insurers attorneys and other designated recipients where appropriate and permitted by the signed authorization and applicable law and policy requirements for each case and transaction in practice over time with maintained records and reviewable evidence available to authorized compliance personnel when needed for audits investigations or operational verification purposes and retention management decisions across the covered entity and its business associates as applicable under documented agreements and procedures that govern access, use, disclosure, and preservation of protected health information in electronic workflows managed through signNow and connected systems used by the organization for authorized healthcare records administration and patient service operations with appropriate safeguards and accountability throughout the complete lifecycle of each authorization from preparation through signature completion storage retrieval and eventual disposition according to policy and law requirements applicable to the records and organization involved in the disclosure process at issue for the patient and recipient named in the form and relevant healthcare transaction supporting the request and release of protected health information through authorized channels maintained by the responsible team and designated administrators with documented oversight for every activity performed by authorized users in the workflow and related systems used for its processing and preservation for compliance and operational purposes over time as required by policy and applicable regulation governing healthcare information handling and electronic records in the United States and relevant state law where applicable to the specific authorization and disclosure circumstances presented in the request. Shared templates help healthcare teams preserve the required authorization language while delegated sending lets authorized staff initiate patient-specific requests. Admin controls can separate template management, sending, and review responsibilities. The organization should define permissions before using the form, especially when records contain PHI and multiple departments participate in disclosure workflows. signNow’s role controls, audit trails, and document history can support that operating model when configured according to internal privacy procedures. Supervisors can review access activity, maintain approved templates, and remove permissions when staff change roles or leave the organization. This structure helps keep the form consistent while allowing authorized operational teams to complete routine release requests securely and traceably within established compliance and records-management policies for the organization and its designated healthcare partners and service providers handling authorized PHI disclosure activities across patient support, records administration, care coordination, insurance processing, legal response, and related functions under approved procedures and documented responsibilities established by the covered entity and applicable business associates for each workflow and authorization request processed through the platform and connected systems with appropriate access controls and oversight mechanisms in place for every user and transaction from initiation through completion and archival under the organization’s retention and security requirements for electronic records containing protected health information and related authorization evidence maintained for later review and accountability when appropriate and permitted under policy and applicable law with clear role boundaries and approved administrative processes governing access and use of patient information throughout the workflow and business operation for every completed form and associated audit record retained by the responsible organization and authorized parties as required by their governing procedures and agreements for handling disclosures and preserving records securely through the full lifecycle of the transaction including preparation, signature, delivery, retrieval, review, storage, and disposition decisions made by authorized personnel after applicable retention obligations are satisfied and documented accordingly for the specific patient authorization and release activity in question involving healthcare records or related protected information and designated recipients named in the form by the patient or legally authorized representative under applicable privacy requirements and organizational policy with appropriate safeguards maintained throughout the electronic signing process and subsequent recordkeeping operations conducted by the organization and its approved service providers and staff members with documented accountability and review procedures supporting reliable administration of each authorization request and completed release record for the relevant healthcare transaction and patient communication need over time as managed by authorized administrators and operational teams using signNow’s available controls and features within the configured account and organization’s compliance program for electronic forms and protected information handling in the United States under applicable federal and state requirements as determined by the responsible legal and compliance personnel for each use case and disclosure scenario.
Platform requirements for signing
Use Chrome, Firefox, Safari, or Edge on Windows 10, macOS, iOS, or Android. signNow encrypts data in transit with TLS 1.2 or TLS 1.3 and supports mobile signing through its applications.
Supported browsers Chrome, Firefox, Safari, and Edge Supported systems Windows 10, macOS, iOS, and Android Secure connection TLS 1.2 or TLS 1.3 connection
Healthcare organizations should use managed devices, controlled accounts, and approved access procedures when this authorization contains PHI. Enterprise deployments may also evaluate API access, SSO provisioning, and retention controls with their security and compliance teams before connecting signNow to clinical or records-management systems.
What the signNow audit trail records
The audit trail separates evidence of consent from the authorization’s substantive content and helps reviewers reconstruct how this PHI release was completed.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Retrieve evidence:
Archive files:
Security controls for PHI authorizations
HIPAA safeguards:
SOC 2 certification:
ISO certification:
Transit encryption:
Storage encryption:
Signer authentication:
Retention periods for authorization records
Retention depends on the record’s regulatory classification and the organization’s policy. For PHI-related authorizations, HIPAA documentation requirements are the most directly relevant federal reference.
Six years: HIPAA records
Three years: tax records
Six years: tax understatement
Three years: payroll records
Five years: injury records
Troubleshooting this PHI authorization workflow
These answers address signing, HIPAA, audit-trail, plan, and evidence questions that can arise when processing this authorization through signNow.
signNow Business includes templates, audit trails, and legally binding eSignatures for this authorization. If protected health information is involved, signNow identifies HIPAA compliance as requiring a Business Associate Agreement, so confirm the appropriate account configuration before sending.
A release involving protected health information should use a clear authorization scope, recipient identity, purpose, and expiration. signNow provides audit trails and document history, while HIPAA requirements remain the responsibility of the covered entity and business associate under the applicable agreement.
If the signer cannot open the invitation, verify the email address, resend the request, and try a supported browser. signNow’s Business plan supports document sending and signing; authentication settings may require a higher plan or configured security option.
signNow records signing events, timestamps, and document history in an audit trail. Export the completed authorization and audit record together, then retain them according to the healthcare organization’s policy and HIPAA’s six-year documentation rule under 45 CFR 164.530(j).
Business Premium is listed at $15 per user per month when billed annually and includes bulk send. Bulk send is useful when substantially identical authorizations go to multiple recipients, but each release should still contain the correct patient-specific information.
Electronic signatures generally receive legal recognition under ESIGN and applicable state law when intent, consent, attribution, and record reproducibility are established. A healthcare organization must also evaluate HIPAA safeguards, consumer disclosures, and any state-specific authorization requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.