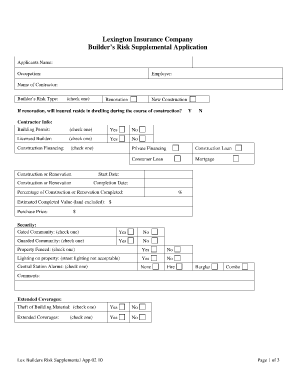
Risk Supplemental Form
Use a Risk Supplemental template to make your document workflow more streamlined.
Risk Supplemental Form overview
Risk Supplemental Form is a business document used to collect additional risk-related information, disclosures, acknowledgments, or approvals before an organization makes or reviews a decision. The supplied form name does not identify an issuing agency, statutory filing deadline, or universal field list, so users should follow the instructions attached to their specific version. With signNow, a sender uploads that version, checks detected fillable fields, routes it to designated recipients, captures signatures, and retains the completed form with its audit trail. ESIGN and applicable state electronic-transactions law may support electronic signing when intent, consent, attribution, and record retention requirements are satisfied.
Who uses Risk Supplemental Form
Business teams
Organizations use Risk Supplemental Form to collect risk-related disclosures, supporting details, acknowledgments, or approvals from employees, contractors, clients, and business partners. Teams should confirm the form’s required fields and intended recipients before sending it for signature.
Review groups
Compliance, legal, healthcare, finance, and operations groups can route Risk Supplemental Form through controlled review processes. The appropriate audience depends on the underlying risk decision, the information requested, and any separate privacy or retention obligations.
Features that support Risk Supplemental Form workflows
Risk Supplemental Form workflows benefit from consistent field placement, controlled signer routing, recorded actions, and accessible records without changing the form’s substantive requirements.
Reusable template
Upload the Risk Supplemental Form once, then place required fields consistently so each recipient receives the same controlled document version.
Field detection
Auto-detected fields reduce manual placement work while preserving space for risk details, acknowledgments, initials, and signatures.
Signer routing
Send the prepared form to specified recipients by email, helping teams track who must review or sign each submission.
Audit trail
A recorded signing history connects signer actions, timestamps, and document status, supporting later review of the completed Risk Supplemental Form.
Mobile access
Mobile apps let authorized users review and sign the Risk Supplemental Form when desktop access is unavailable.
Document records
Completed forms remain organized with related signing records, making retrieval easier during internal review or a documented dispute.
How Risk Supplemental Form works
The signNow workflow turns the Risk Supplemental Form into a controlled signing sequence while leaving its substantive risk questions unchanged.
Upload form: Upload the current Risk Supplemental Form document. Check fields: Auto-detect fields, then verify every required placement. Route for review: Add recipients and send the prepared form. Store securely: Collect signatures and store the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the Risk Supplemental Form audit trail records
The audit trail supplements the Risk Supplemental Form by documenting who acted, when actions occurred, and how the completed record can be reviewed.
Authenticate signer:
Capture timestamp:
Identify document:
Seal record:
Log activity:
Export evidence:
Secure signer authentication for Risk Supplemental Form
PKI authentication:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Authentication records:
Privacy and disclosure pitfalls
Risk details placed in an unrestricted attachment can expose personal or business information to recipients who do not need access. A missing electronic-consent disclosure can weaken evidence that a consumer agreed to receive or sign the Risk Supplemental Form electronically. Shared accounts or unreviewed permissions can make it difficult to attribute a Risk Supplemental Form signature to the intended individual. Using an outdated form version can separate the signed record from the risk criteria the organization intended to evaluate.
Risks of incomplete Risk Supplemental Form records
Incomplete risk record
Attribution challenge
Evidentiary gap
Privacy exposure
Record-keeping practices for Risk Supplemental Form
Keep the completed Risk Supplemental Form, signing evidence, and access controls aligned with the record’s purpose and applicable legal requirements.
Set the retention period before signing
Export the audit trail with the form
Restrict access to completed records
Preserve the signed form version
Retention periods for Risk Supplemental Form records
Retention depends on the record’s content and legal context. Do not apply a schedule from another form without confirming the underlying authority and scope.
Three years from filing
Six years from creation
Three years after hire
State or contract period
Indefinite retention when required
Business types using Risk Supplemental Form
Risk Supplemental Form can support different operating models when its required fields, recipients, privacy controls, and retention rules are defined before sending.
Solo consultants can use Risk Supplemental Form to document client-provided risk information and approvals without maintaining separate paper packets for each engagement. Healthcare practices can route a Risk Supplemental Form containing relevant patient or operational information through controlled access, subject to HIPAA and a required BAA when PHI is involved. Enterprise compliance teams can standardize Risk Supplemental Form routing, preserve audit trails, and apply role-based access across departments handling risk reviews.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Legal standing for Risk Supplemental Form
Risk Supplemental Form may be electronically signed for a U.S. business transaction when the signer intends to sign, consents to electronic records, can be attributed to the signature, and the record can be retained and reproduced. ESIGN and applicable state law support that framework. Wills, codicils, testamentary trusts, court orders, and specified family-law documents are excluded from ESIGN coverage.

Risk Supplemental Form troubleshooting
These answers address field accuracy, electronic-signature evidence, authentication, plan limits, protected information, and retention for Risk Supplemental Form workflows.
Upload the current Risk Supplemental Form as a PDF or supported document, then inspect every auto-detected field before sending. signNow’s Business plan includes templates and audit trails, but field detection still requires human review for accuracy.
Electronic signing can be supported under ESIGN and UETA when intent, consent, attribution, and record retention requirements are met. Consumer-facing transactions also require the disclosures in 15 U.S.C. §7001(c), including paper-access and withdrawal procedures.
Use signNow’s SMS authentication option when the workflow requires an additional access check. For higher-risk decisions, define the identity-verification method in organizational policy and retain the resulting evidence with the completed form.
The Business plan is listed at $8/user/month when billed annually. Paid plans include 100 signature invites per user per year, with overage fees; confirm current plan terms before routing high-volume Risk Supplemental Form requests.
If Risk Supplemental Form contains protected health information, signNow identifies HIPAA compliance as requiring a BAA. Confirm that the organization has the required BAA and appropriate access controls before collecting PHI.
Export the completed document and audit trail from the signing workflow, then preserve them under the organization’s retention policy. HIPAA-covered records require six years under 45 CFR §164.530(j), unless a longer applicable rule applies.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.