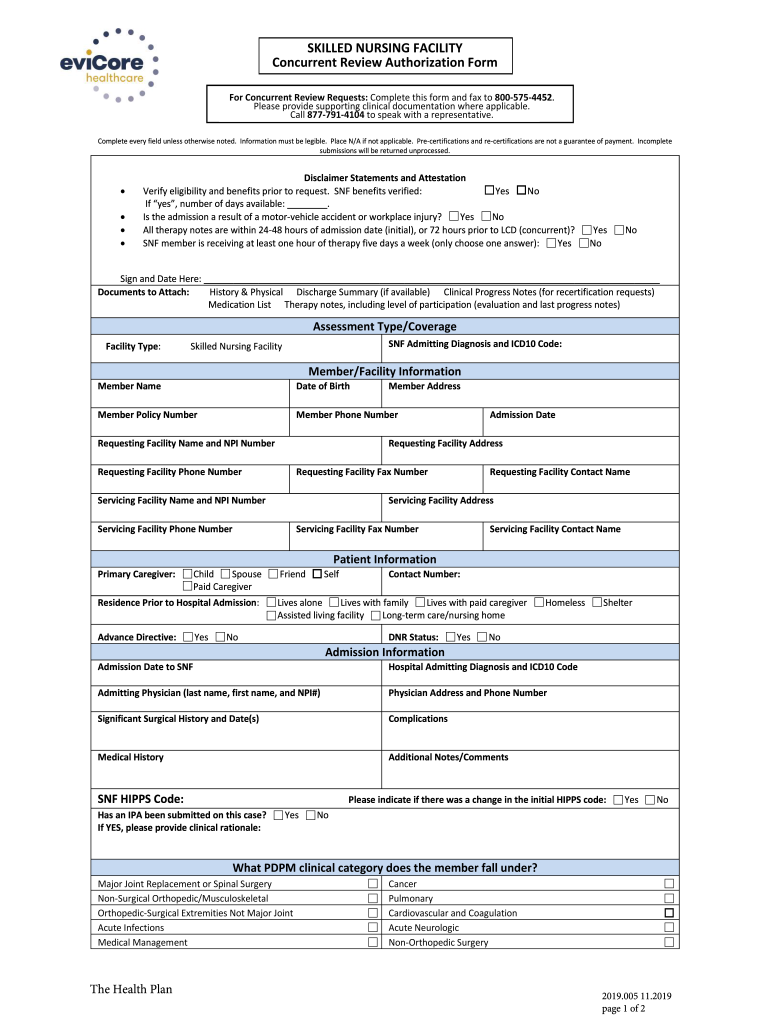
Concurrent Review Authorization Form
Use a Concurrent Review Authorization Form template to make your document workflow more streamlined.
What the authorization form does
A Concurrent Review Authorization Form records permission for designated parties to review information during the same process or review period. It identifies the person granting authorization, the reviewers or recipients, the permitted scope, and the date and signature evidence. In signNow, upload the form, let the platform detect fillable fields, confirm assignments, send it to the required participants, and store the completed copy with its audit trail. No issuing agency, universal deadline, or single nationwide version is specified for this form, so the underlying organization’s policy and applicable state law control.
Who uses this authorization form
Healthcare teams
Healthcare administrators and patient-access teams use the form to document permission for concurrent review of designated records. If protected health information is involved, the workflow should include the required privacy controls and a signNow business associate agreement where applicable.
Regulated review teams
Legal, insurance, and financial-services teams use the form when several authorized reviewers must examine the same matter. They define the permitted scope, assign each reviewer, capture signatures, and retain the completed record with its audit trail.
How to complete the authorization in signNow
Use this sequence to prepare, route, sign, and preserve the Concurrent Review Authorization Form in signNow.
Upload form:
Upload the current Concurrent Review Authorization Form to signNow. Check fields:
Confirm detected fields and assign each reviewer or signer. Send request:
Add required authentication and send the authorization request. Store record:
Collect signatures and store the completed form with audit evidence.
Recommended authorization workflow setup
Configure the Concurrent Review Authorization Form around verified signer identity, complete event evidence, controlled access, and the organization’s applicable record schedule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Follow the organization’s record schedule |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the authorization audit trail works
The signNow audit trail records who handled the Concurrent Review Authorization Form, what happened, and when each event occurred.
Authenticate signer:
Capture timestamps:
Record document hash:
Seal event history:
Review activity:
Export evidence:
Privacy controls for authorization forms
Personal health, employment, or financial details may remain visible in completed authorization copies shared beyond the review team. Missing electronic-consent language can weaken evidence that each participant agreed to review and sign the authorization digitally. Broad folder permissions may expose the authorization form and its signed copy to users without a review-related business need. Sending the form to the wrong recipient can disclose protected information before identity and authorization status are confirmed.
Legal standing of the authorization
A Concurrent Review Authorization Form may be evidence of consent when the signer demonstrates intent, receives required electronic-record disclosures, can be identified, and the completed record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable UETA rules support electronic records, but exclude wills, certain court orders, and family-law decrees.

Best practices for completing the authorization
Accurate scope, participant assignment, evidence preservation, and legal-scope checks reduce disputes involving this authorization form.
Define the permitted review scope
Verify every signer and reviewer assignment
Preserve the completed record and audit trail
Check exclusions and state formalities
Security for signed authorization records
AES-256 encryption:
TLS protection:
HIPAA safeguards:
SOC 2 controls:
ISO 27001 certification:
Audit-ready records:
Platform requirements for signing
Complete the Concurrent Review Authorization Form in signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. The signNow mobile apps support signing on iOS and Android, with encrypted connections using TLS 1.2 or TLS 1.3.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android signNow apps
Organizations should manage mobile access through approved devices and user policies. Enterprise deployments may also require SSO, API access, or integration controls. Confirm that the chosen workflow preserves the authorization, audit trail, and access permissions required by the organization’s privacy and records policies.



Retention periods for authorization records
Retention depends on the record’s purpose and industry, not merely its signature date. Match the completed authorization and audit trail to the governing legal schedule.
Organization schedule applies
Six years for HIPAA records
Three years for tax records
I-9 rule when applicable
State rule may extend
Concurrent review authorization troubleshooting
Resolve field, consent, plan, privacy, and enforceability questions before distributing the completed authorization.
Start by confirming that the Concurrent Review Authorization Form contains every required reviewer, authorization scope, date, and signature field. On signNow Business, upload the form, place fields, and use the audit trail to document completion under ESIGN and applicable UETA rules.
Upload the current Concurrent Review Authorization Form as a PDF or document file, then inspect signNow’s detected fields before sending. Correct field assignments manually when the form’s reviewer names, authorization limits, or signature locations are not detected accurately.
For a consumer-facing authorization, electronic-record consent must address paper-copy rights, electronic access, and withdrawal procedures under ESIGN, 15 U.S.C. §7001(c). Add the required disclosure before requesting a signature rather than relying only on an email invitation.
Business includes legally binding eSignatures, templates, and audit trails at $8 per user per month with annual billing. Business Premium adds bulk send at $15, while Enterprise adds advanced signer authentication at $30.
If the authorization includes protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm the BAA and apply your organization’s access, disclosure, and retention policies before sending the form.
ESIGN and UETA generally recognize an electronic signature when intent, consent, attribution, and record retention are established. They do not override exclusions such as wills, court orders, or family-law decrees, which require separate legal review.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.