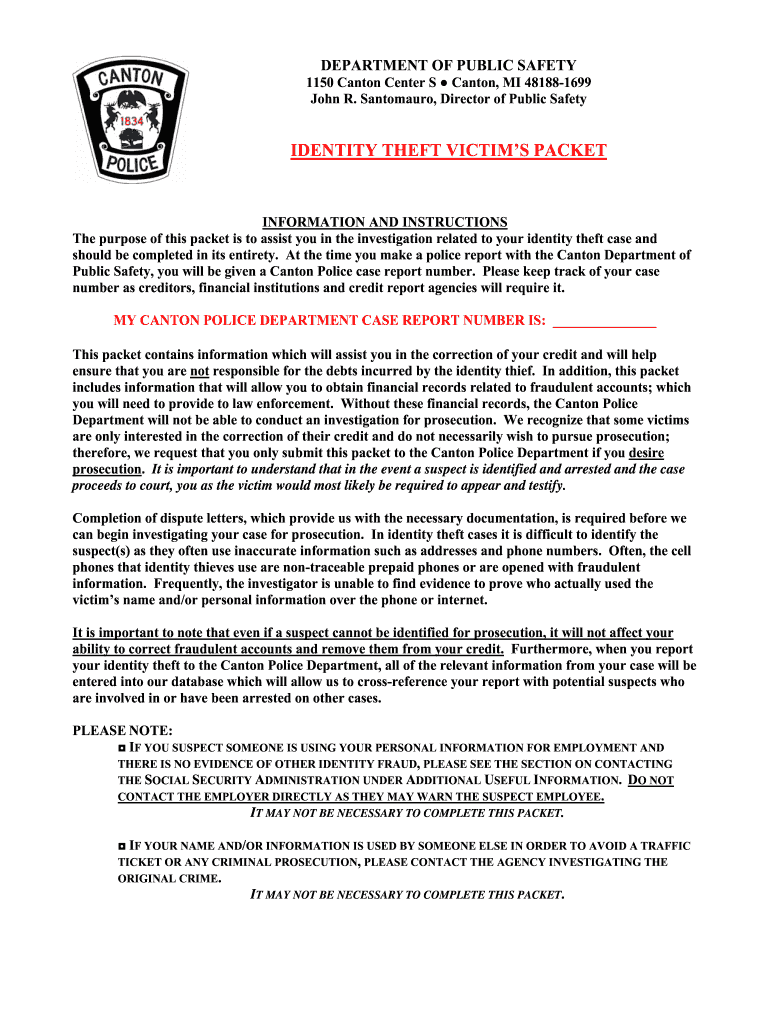
Identity Theft Victims Packet Canton Canton Mi Form
Use a IDENTITY THEFT VICTIMS PACKET Canton Canton mi template to make your document workflow more streamlined.
What the Canton identity packet does
The Identity Theft Victims Packet Canton Canton Mi Form is a document set for recording a Canton, Michigan resident’s identity-theft report and supporting information. It can organize the victim’s identifying details, incident narrative, affected accounts, contacts, and authorizations before delivery to the responsible agency or organization. With signNow, a sender uploads the packet, reviews detected fields, assigns each field to the correct participant, and sends it for electronic completion. The completed packet, signer activity, timestamps, and audit trail can then be retained together. ESIGN and UETA provide the general U.S. framework for qualifying electronic records, subject to applicable exclusions and procedures.
Who uses the Canton identity packet
Canton agencies
Municipal consumer-protection offices, police departments, and victim advocates can use the packet to collect a claimant’s identity-theft statement, supporting chronology, account information, and authorization for follow-up. Limit access because these records may contain Social Security numbers, addresses, financial details, and other sensitive identifiers.
Reviewing organizations
Banks, credit unions, employers, and legal-service teams can use the packet when a Canton resident reports fraudulent account activity or misuse of personal information. signNow keeps the signed packet and audit trail together, while the receiving organization determines its own evidence, disclosure, and retention requirements.
Complete the Canton packet in signNow
Use this sequence to prepare the Canton identity-theft packet, collect the required electronic signatures, and preserve completion evidence.
Upload packet:
Upload the completed Canton packet PDF. Check fields:
Review and correct detected fields. Assign signers:
Assign each field to its signer. Send packet:
Send the packet through signNow. Save evidence:
Download the signed packet and audit trail.
What the packet audit trail records
A signNow audit trail documents the evidence surrounding completion of the Canton identity-theft packet, rather than replacing the packet itself.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Log activity:
Retrieve evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Canton packet setup
Configure the Canton packet around controlled access, clear signer intent, preserved evidence, and the organization’s documented identity-theft retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export certificate with completed packet |
| Document retention | Follow the organization’s identity-theft policy |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
Devices for completing the Canton packet
The Canton packet can be prepared in signNow through Chrome, Firefox, Safari, or Edge on Windows 10, Windows 11, and macOS. signNow mobile apps provide packet review and signing on iOS and Android, while camera capture can add supporting pages when the source material is paper.
Web browsers Chrome, Firefox, Safari, and Edge on Windows 10, Windows 11, and macOS. Mobile apps signNow mobile apps support iOS and Android devices for packet review and signing. Document capture Camera capture can add supporting pages from iOS and Android devices.
Organizations handling identity-theft information should use managed Windows, macOS, iOS, or Android devices, restrict downloads, and apply role-based access. If the packet enters a larger case-management system, confirm API, SSO, and storage requirements with the organization’s signNow administrator before deployment.
Security for identity-theft records
Data at rest:
Data in transit:
Security reporting:
Information security:
Health information:
Electronic signatures:
Privacy issues to check before sending
Identity theft packets can expose Social Security numbers, account details, and addresses when unnecessary personal data remains visible in completed copies. A victim may sign without understanding how the packet will be shared, weakening evidence that electronic-record consent was informed. Unrestricted staff access can expose identity-theft records beyond the investigators, agencies, or financial institutions handling the specific dispute. Missing dates, incident details, or supporting attachments can force recipients to request corrections before reviewing the identity-theft claim.
Documents requiring extra formalities
Notarization required
Wills excluded
Family law excluded
Deed formalities
Legal standing of electronic packets
A completed Canton identity-theft packet may support an electronic business record when the signer’s intent, consent, attribution, and reliable retention are demonstrated under ESIGN, 15 U.S.C. ch. 96, and applicable UETA law. Those frameworks exclude wills, court orders, and certain family-law records; Michigan-specific requirements should be confirmed before use.



Identity-theft packet troubleshooting
Resolve field, authentication, consent, storage, and plan questions before sending a Canton identity-theft packet.
Upload the packet as a PDF, then review signNow’s detected fields before adding the victim, preparer, or recipient roles. If a field is missed, place the appropriate text, date, checkbox, or signature field manually. Preserve the original packet for comparison.
The Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures at $8 per user per month when billed annually. Uploading the Canton packet does not change those plan capabilities, but plan limits and overage terms should be reviewed before volume use.
Use signNow’s signer authentication options, including email delivery and stronger methods available through the selected plan. For sensitive identity-theft information, verify the recipient independently and limit the packet to the people responsible for the dispute or investigation.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. For consumer-facing records, 15 U.S.C. §7001(c) requires electronic-record disclosures and access procedures; confirm whether those requirements apply to your workflow.
Use the audit trail to preserve signer actions, timestamps, IP information, and the completed document. Export the certificate of completion with the signed packet, then store both under the organization’s identity-theft record policy.
The Business Premium plan is listed at $15 per user per month annually and includes bulk send. Subscription plans include 100 signature invites per user per year, so confirm invite usage before sending repeated victim packets.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.