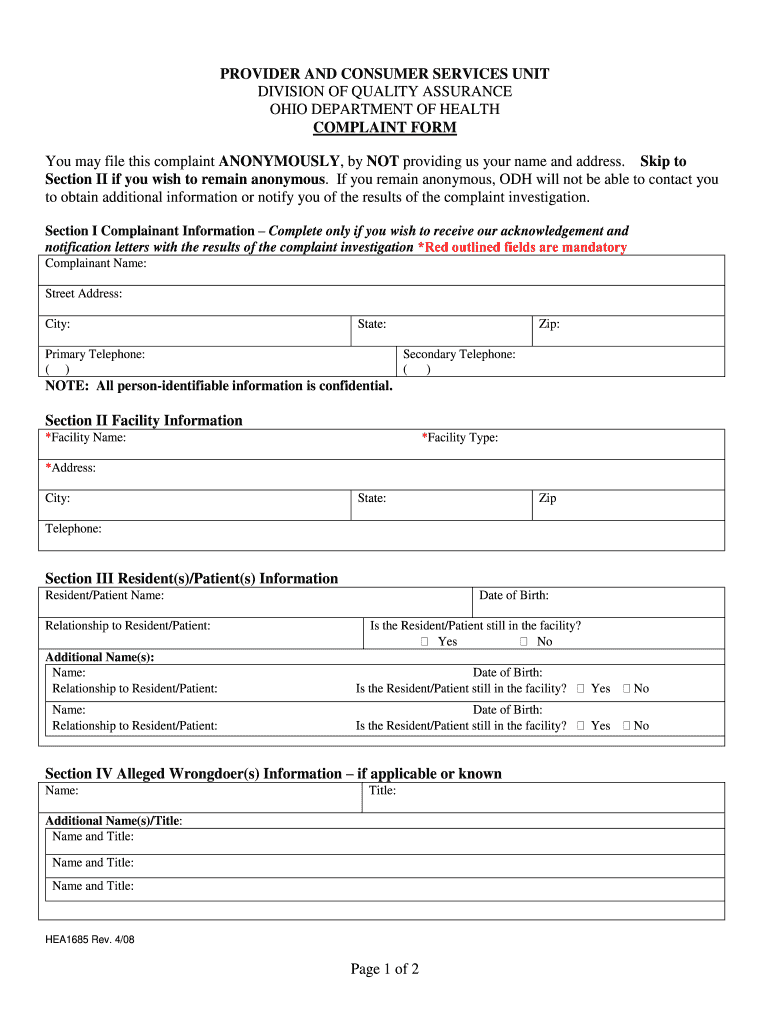
Anonymous Report To Health Department Form
Use a Anonymous Report To Health Department template to make your document workflow more streamlined.
What this anonymous health report does
An Anonymous Report To Health Department Form lets a person communicate a public-health concern without unnecessarily identifying the reporter. Its exact fields and submission rules depend on the receiving U.S. health department, because no single nationwide anonymous-report template governs every jurisdiction. Complete only facts the form requests, avoid unnecessary personal or protected health information, and confirm whether the agency accepts electronic signatures or requires a separate submission method. signNow can upload the document, detect fillable fields, route requested signatures, and preserve the completed record with an audit trail.
Who uses this health department form
Healthcare reporting
Healthcare workers, patients, or community members can report suspected health risks while limiting unnecessary identifying information.
Health departments
Public-health offices can route, review, and preserve submitted reports with controlled access and an auditable record.
Complete the report in signNow
Use the receiving health department’s template and instructions, then complete only the fields necessary for the report.
Upload form:
Upload the agency’s report template to signNow. Check fields:
Review detected fields and add missing details. Set access:
Assign only required recipients and permissions. Complete report:
Complete the report and any requested attestation. Preserve record:
Download the record and audit trail securely.
Recommended report workflow settings
Use controlled access, documented consent, and an auditable workflow when preparing an anonymous report for health department review.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Follow the responsible health department’s policy |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the audit trail records report activity
An audit trail documents the technical history of preparing, signing, and retrieving an anonymous health department report.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Build evidence:
Export history:
Security controls for health reports
Data in transit:
Data at rest:
Independent controls:
Security management:
Health information:
Privacy governance:
Privacy pitfalls in anonymous reports
Including identifying details can compromise anonymity and expose the reporter or affected individuals. Unclear consent language may disclose health information without documenting the reporter’s intended permission. Emailing completed reports to broad groups can expose personal data beyond authorized health department staff. Shared accounts and excessive permissions can let unauthorized users view or alter sensitive reports.
Best practices for anonymous reporting
Accuracy, data minimization, controlled access, and documented preservation reduce avoidable privacy and evidentiary problems when preparing this report.
Minimize identifying information
Describe facts precisely
Export the audit trail
Apply the correct retention rule
Rules that may limit electronic use
Report rejected
Privacy exposure
Confidentiality breach
Submission delay
Legal standing of electronic reports
An electronic health department report can provide a reproducible record when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains accessible. ESIGN and UETA support electronic signatures, but wills, certain court orders, and other statutory exclusions remain outside those rules.

Troubleshooting anonymous health reports
Resolve access, privacy, audit-trail, and compliance questions before sending an Anonymous Report To Health Department Form through signNow.
signNow’s Business plan supports templates, audit trails, mobile apps, and legally binding eSignatures. Upload the report, place fields, and send it only to authorized recipients. If the report requires a government portal submission, complete that separate submission after downloading the signed record.
An anonymous report should not collect unnecessary identifying information. Configure only the fields required by the receiving health department, explain any consent language, and restrict access. HIPAA compliance requires a BAA when the workflow handles protected health information for a covered entity.
signNow records timestamps, actions, and document history in the audit trail. Export the completed report and audit trail together, then preserve them under the health department, employer, or covered-entity retention policy that applies to the underlying record.
Business Premium includes kiosk mode and bulk send, while Enterprise adds advanced signer authentication, formula fields, and conditional fields. Select the plan based on the report’s routing and authentication needs rather than assuming every feature is included in Business.
For health information handled by a covered entity or business associate, signNow identifies HIPAA compliance as requiring a BAA. Confirm that the organization has the required agreement and controls before placing protected health information in the workflow.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are demonstrated. They do not replace a health department’s filing rules, identity requirements, or submission channel, so confirm the receiving agency’s instructions before relying on an electronic report.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.