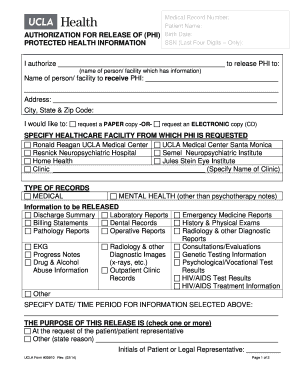
Authorization For Release Of Phi Ucla Health Uclahealth
Use a AUTHORIZATION FOR RELEASE OF PHI UCLA Health Uclahealth 2019 template to make your document workflow more streamlined.
What this UCLA Health authorization does
Authorization For Release Of Phi Ucla Health Uclahealth is a patient authorization that permits UCLA Health to disclose specified protected health information to an identified recipient. The signer reviews the patient and recipient information, confirms the permitted release scope, and records consent through a dated signature. In a signNow workflow, the sender uploads the form, places or confirms fillable fields, sends it to the signer, and retains the completed PDF with its audit trail. HIPAA requires authorization handling and privacy safeguards; signNow states that HIPAA use requires a business associate agreement.
Who uses this UCLA Health authorization
Healthcare providers
Healthcare providers and their records teams use this authorization to identify the patient, define the permitted disclosure, and collect the patient’s signature before releasing protected health information. A completed copy helps staff document consent and route the request to the appropriate recipient.
Authorized recipients
Patients, attorneys, insurers, and designated representatives use the signed authorization when requesting UCLA Health records. The workflow helps identify the recipient, preserve the signed document, and maintain an accessible record of the patient’s stated disclosure permission.
People who use this release form
A UCLA Health records coordinator prepares the authorization, checks the named recipient and disclosure scope, sends it for patient signature, and preserves the completed PDF with audit evidence for the release workflow and privacy review if needed. A patient or legally authorized representative reviews the requested disclosure, confirms the recipient and permitted information, signs through the assigned signNow workflow, and receives or accesses the completed authorization according to the healthcare organization’s records process.
How the authorization workflow works
Follow the document from upload through consent capture and controlled retention for a complete UCLA Health release record.
Upload form: Upload the UCLA Health authorization Place fields: Confirm fields for patient and signer information Send document: Send the release authorization securely Archive record: Store the signed PDF and audit trail
Quick steps to complete the authorization
Use this signNow sequence to prepare the UCLA Health release authorization, collect consent, and retain evidence of completion.
Upload form:
Upload the UCLA Health authorization PDF. Detect fields:
Let signNow detect fillable fields. Check fields:
Review patient, recipient, and signature fields. Send request:
Send the authorization to the signer. Store evidence:
Download the signed form and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the audit trail records consent
The audit trail adds technical evidence around the UCLA Health authorization without replacing the patient’s disclosure decision or consent language.
Authenticate signer:
Capture timestamps:
Hash document:
Seal completion:
Record activity:
Export evidence:
Processing stages for the authorization
Use a defined sequence to prepare, sign, and preserve this UCLA Health release authorization without losing consent evidence.
Prepare the authorization
Deliver to signers
Complete signer review
Archive the record
Find and fill out the correct authorization for release of phi ucla health uclahealth
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2012 UCLA 30910 [2012-10] 2019 | 4.8 Satisfied (4490 Votes) | |
| *2012 UCLA 30910 [2012-10] 2016 | 4.8 Satisfied (113 Votes) | |
| *2012 UCLA 30910 [2012-10] 2012 | 4.8 Satisfied (6827 Votes) |
Security controls for protected health information
HIPAA protection:
Transport encryption:
Stored encryption:
Security certification:
Information security:
Audit evidence:
Record-keeping practices for this authorization
Preserve the signed authorization, audit evidence, and access history together so UCLA Health release decisions remain traceable and reviewable.
Retain authorization evidence for six years
Restrict access before sending
Export the audit trail with the PDF
Archive signed records securely
Platform requirements for signing
Complete Authorization For Release Of Phi Ucla Health Uclahealth in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, while TLS 1.2/1.3 protects data in transit.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android mobile apps
Healthcare organizations should use managed devices, controlled user access, and approved storage for completed authorizations containing PHI. Enterprise deployments may also configure API access, SSO provisioning, and stronger signer authentication. A HIPAA workflow requires a business associate agreement with signNow, alongside organizational privacy procedures.
Privacy pitfalls when releasing PHI
Entering a recipient’s email incorrectly can expose protected health information to an unintended person or delay the requested UCLA Health disclosure. Leaving the permitted information or purpose unclear can make the authorization difficult to apply during records processing and privacy review. Failing to capture electronic consent evidence weakens the connection between the patient, the signed authorization, and the requested disclosure. Giving broad staff access to completed authorizations increases the chance of viewing or sharing PHI beyond the approved release workflow.
State rules and document exclusions
State notarization
Wills excluded
Family law
Deed acknowledgment
Troubleshooting the UCLA Health authorization
Resolve the named signing, privacy, and retention issues before releasing protected health information through this authorization workflow.
Business provides legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR support. A UCLA Health workflow involving PHI additionally requires a business associate agreement and organization-approved privacy procedures.
signNow states that HIPAA compliance requires a business associate agreement. Confirm that the applicable signNow account has the required BAA before sending Authorization For Release Of Phi Ucla Health Uclahealth with protected health information.
Upload the original PDF, then review signNow’s detected fields. Confirm every patient, recipient, date, and signature field before sending because automated field detection does not decide whether the disclosure scope is legally correct.
Use signNow’s signer authentication options, including SMS OTP where configured, when the organization needs more evidence than an email invitation. Stronger authentication supports attribution but does not replace valid HIPAA authorization language.
Business Premium includes bulk send, kiosk mode, request payments, and quick invite links. Bulk sending should not be used for this authorization unless each recipient and disclosure scope is independently reviewed.
Completed records can include the signed PDF and signNow audit trail. Preserve them in an access-controlled repository under the organization’s HIPAA retention policy; 45 CFR §164.530(j) requires six-year retention for specified HIPAA documentation.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.