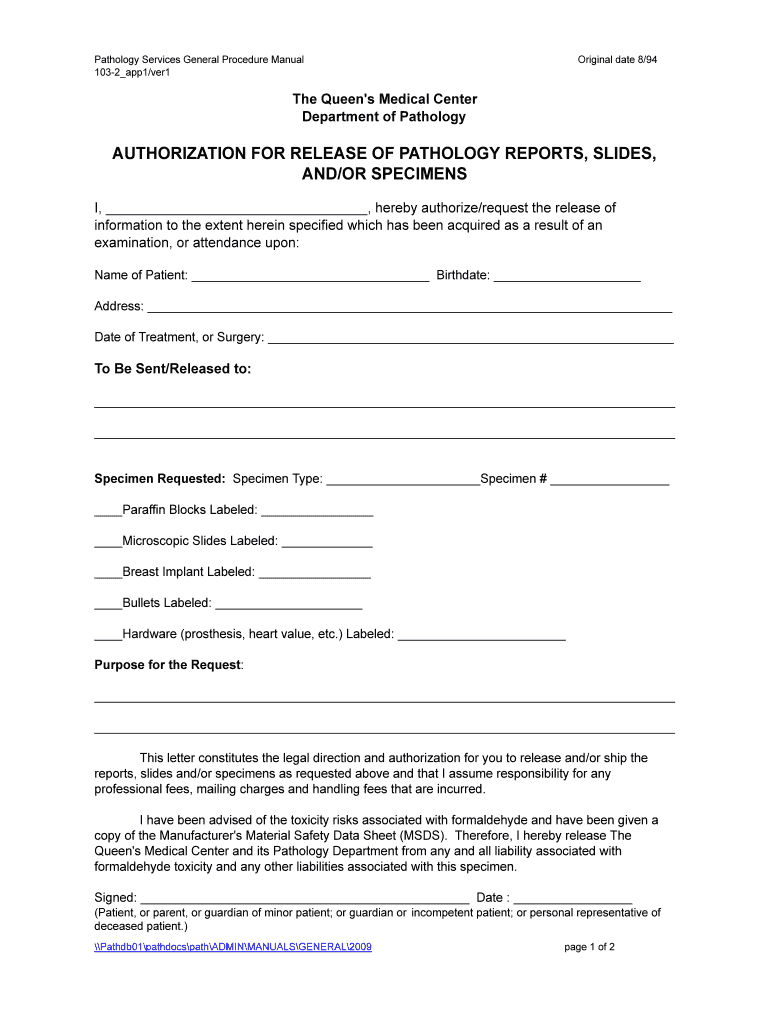
Authorization For Release Of Pathology Reports, Slides, Andor Form
Use a Authorization For Release Of Pathology Reports, Slides, Andor template to make your document workflow more streamlined.
What this pathology release authorization does
An Authorization For Release Of Pathology Reports, Slides, Andor Form is a patient authorization that permits a specified holder to disclose identified pathology materials to a named recipient. The signer reviews the patient details, requested reports or slides, recipient, purpose, and any stated expiration or scope before signing. With signNow, the organization uploads the document, detects or places fillable fields, sends it to the authorized signer, captures the signing event, and stores the completed record with an audit trail. HIPAA-covered organizations must also apply applicable Privacy Rule and state requirements.
Who uses this pathology authorization
Healthcare records
Pathology departments and medical-records teams send this authorization when a patient permits reports, slides, or the named form to reach an identified recipient. They verify identity, scope, recipient, and purpose before releasing protected health information.
Authorized recipients
Patients, attorneys, insurers, or treating providers may receive the authorized pathology materials. The authorization identifies the permitted disclosure, while the records holder remains responsible for HIPAA, state-law, and internal release controls.
How this pathology authorization works
The workflow connects the patient’s authorization, the requested pathology materials, the recipient, and the completed electronic record.
Review patient details: Confirm the patient’s identity and requested pathology materials. Define release scope: Specify the recipient, purpose, and permitted disclosure scope. Request signature: Send the authorization to the patient or authorized signer. Archive securely: Store the completed authorization with its audit trail.
Complete this pathology release online
Use these steps to prepare, send, sign, and retain the authorization without changing its disclosure scope.
Upload form:
Upload the pathology release form. Add fields:
Place or confirm patient and signer fields. Send request:
Send the authorization securely. Archive record:
Review the completed record and audit trail.
What the pathology audit trail records
The audit trail supplements the authorization itself by documenting who acted, when they acted, and how the completed record can be retrieved.
Authenticate signer:
Capture timestamp:
Protect document:
Seal record:
Record events:
Retrieve evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended pathology release setup
Use controlled authentication, a reproducible audit trail, and access-managed storage for every completed pathology release authorization.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enabled with completion certificate |
| Document retention | 6 years when HIPAA 45 CFR 164.530(j) applies |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
Authentication for pathology disclosures
PKI signatures:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signing evidence:
Privacy pitfalls in pathology disclosures
A release can identify the patient but fail to identify the exact pathology reports, slides, or form authorized for disclosure. The recipient or purpose may be entered too broadly, creating uncertainty about where pathology information may be sent. A missing signature date, expiration term, or required witness or authorization language can delay the records department’s response. Patient health information may be downloaded or shared outside the approved access group after the signed authorization is completed.
Risks of incomplete pathology authorizations
Scope dispute
Consent failure
Access violation
Evidence weakness
Retention periods for pathology authorizations
Keep the signed authorization and supporting release record according to the governing healthcare policy and applicable federal rule.
6 years from creation
3 years from filing
6 years for understatement
3 years for payroll
5 years after year
Record-keeping practices for pathology releases
Accurate scope, controlled access, and reproducible evidence matter when a signed authorization permits pathology information to be released.
Apply the correct healthcare retention period
Export the audit trail after completion
Restrict access to signed releases
Match disclosure scope to records



Pathology release workflow examples
Healthcare and legal teams can adapt the workflow to patient-authorized pathology disclosures while preserving document-specific review controls.
Healthcare provider
Fertility Centers of Illinois can use a healthcare authorization workflow to collect patient signatures before sharing pathology-related records with an approved recipient.
- Healthcare records
- Patient signature
- Controlled disclosure
The organization can send a defined authorization, capture the patient’s electronic signature, and preserve the completion evidence with the document. John Butler, founder of Fertility Centers of Illinois, specifically cited signNow’s responsive team and API in the company’s customer story; that source does not identify this exact pathology form.
Legal services
A legal-services team handling a patient’s records request can route the authorization to the correct signer before releasing pathology materials.
- Role-based routing
- Named recipient
- Audit evidence
signNow’s role-based sending capabilities can help separate preparation from authorization while retaining a documented signing event. The workflow still requires the records holder to verify the patient’s identity, disclosure scope, recipient, and any state-law requirements before releasing reports or slides.
Troubleshooting pathology release workflows
These answers address named signing, compliance, plan, and archival issues for this pathology-record authorization.
Upload the original PDF or a clear scan, then use signNow’s field tools to place signature, date, and required response fields. Review the patient, recipient, purpose, and disclosure scope before sending. The Business plan includes templates and audit trails for repeat authorization workflows.
A patient can sign through the email invitation or a shareable signing link. If stronger identity evidence is required, configure SMS-based authentication or another available verification method. HIPAA-covered workflows should use appropriate access controls and a signNow business associate agreement.
The Business plan is listed at $8 per user monthly with annual billing and includes legally binding eSignatures, templates, and audit trails. Business Premium is $15 per user monthly annually and adds bulk send for repeated pathology authorizations.
signNow states that it is HIPAA compliant when a business associate agreement is required. HIPAA’s retention rule for required policies, procedures, and records is six years under 45 CFR §164.530(j); confirm whether the authorization belongs in that record set.
The completed authorization should preserve the signer’s intent, identity evidence, timestamps, and record reproducibility. ESIGN, 15 U.S.C. ch. 96, and applicable UETA law support electronic records when statutory requirements are met; state healthcare rules may impose additional conditions.
Export the signed document and audit trail after completion, restrict access to authorized healthcare personnel, and archive them under the organization’s retention policy. Do not treat signNow storage alone as a substitute for HIPAA security, records, or state-law obligations.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.