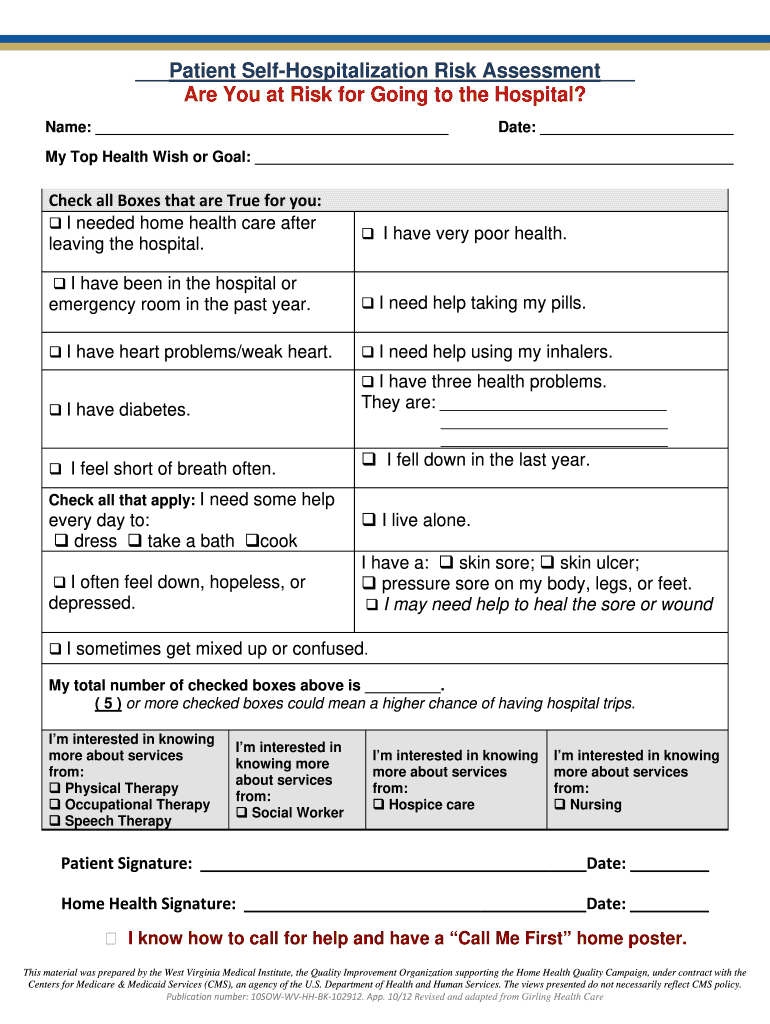
Patient Self Hospitalization Risk Assessment Patient Self Hospitalization Risk Assessment Form
Use a Patient Self Hospitalization Risk Assessment Patient Self Hospitalization Risk Assessment template to make your document workflow more streamlined.
What this patient assessment form does
A Patient Self Hospitalization Risk Assessment Form records a patient’s own answers about factors relevant to possible hospitalization and gives a healthcare organization a documented basis for review. The patient completes the form, signs it electronically when permitted by the organization, and returns it for clinical assessment. With signNow, staff upload the PDF, review auto-detected fields, add missing questions or signature fields, send it to the patient, and retain the completed document with an audit trail. HIPAA safeguards and applicable state medical-record rules still govern handling.
Who uses this patient assessment form
Healthcare providers
Healthcare providers can send this assessment to patients before hospitalization decisions, capture responses and signatures, and preserve a searchable audit trail. Staff should limit access to authorized personnel and apply HIPAA policies when responses contain protected health information.
Patients and representatives
Patients or authorized representatives can complete the assessment remotely on a desktop or mobile device. Clinical teams can use reusable signNow templates for consistent questions, then review the signed record before storing it in the organization’s approved health-record system.
How to complete the patient assessment
Use this workflow to prepare the assessment, collect the required patient signature, and preserve the completed record with its audit evidence.
Upload form:
Upload the patient assessment PDF to signNow. Check fields:
Review auto-detected fields and add missing inputs. Assign signers:
Assign patient and staff signature fields. Send securely:
Send the assessment through email or a signing link. Store records:
Download the signed assessment and audit trail.
Recommended assessment workflow setup
Configure the patient assessment workflow around authenticated signing, documented consent, protected transmission, and controlled record retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled for every completed assessment |
| Document retention | Six years for HIPAA documentation |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the signNow audit trail records
The audit trail documents identity, timing, actions, and record history after the patient receives and signs the assessment.
Authenticate signer:
Capture timestamps:
Protect document:
Seal history:
Export audit trail:
Archive evidence:
Security for patient assessment records
HIPAA safeguards:
Transport encryption:
Storage encryption:
Service assurance:
Security certification:
Electronic signatures:
Platform requirements for signing
The signNow web application supports Chrome, Firefox, Safari, and Edge on Windows and macOS. Patients can also review and sign the assessment through signNow mobile apps for iOS and Android.
Supported browsers Chrome, Firefox, Safari, and Edge Desktop operating systems Windows and macOS desktops Mobile access iOS and Android mobile apps
Healthcare organizations should use managed devices, current browser security updates, and approved access controls when handling assessment responses. Configure user permissions, SSO, API connections, and storage destinations according to the organization’s HIPAA risk analysis and retention policy.
Privacy risks in patient assessments
Including unnecessary diagnoses, medications, or identifying details can expose protected health information beyond the assessment’s stated purpose. Sending the assessment to an incorrect email address can disclose patient information and create an access-control incident. Failing to capture electronic consent can weaken evidence that the patient agreed to receive and sign the assessment electronically. Sharing a completed PDF without its audit trail can make signer attribution, timestamps, and document history harder to verify.
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Best practices for retaining assessments
Use a controlled workflow that protects patient information, preserves signing evidence, and separates federal documentation rules from the organization’s patient-record schedule.
Separate HIPAA documentation from patient-record retention
Preserve the assessment and audit trail together
Minimize disclosure before sending the form
Review state rules and legal holds
Retention schedule for signed assessments
Retention depends on the record category and governing rule. HIPAA documentation has a specific federal period; patient-record schedules and state requirements may extend longer.
Six years for HIPAA documentation
Organization policy for patient records
Consent evidence under ESIGN
Security records under HIPAA
Longer state retention periods
Troubleshooting the patient risk assessment form
These answers address field detection, electronic consent, plan limits, HIPAA safeguards, and audit records for this patient assessment workflow.
If the form contains protected health information, use signNow’s HIPAA-compliant configuration with a business associate agreement. Business, Business Premium, and Enterprise plans provide audit trails; confirm the selected account includes the controls required by your organization.
The Business plan includes templates and audit trails, while Business Premium adds bulk send. For repeated patient assessments, choose Business Premium only when sending the same form to multiple recipients is necessary; otherwise, Business supports individual workflows.
A typed, drawn, or click-to-sign signature can document intent under ESIGN and UETA when consent, attribution, and record retention requirements are met. Keep the completed assessment and audit trail together for later review.
If auto-detection misses a response field, open the uploaded PDF in signNow’s editor and place the required text, checkbox, date, and signature fields manually. Review every risk-assessment question before sending the document.
For consumer-facing healthcare records, provide the ESIGN electronic-record disclosure, demonstrate access to the electronic format, and explain withdrawal procedures under 15 U.S.C. §7001(c). Your organization must also follow applicable HIPAA policies.
Use the audit trail to review signer identity, timestamps, actions, and document history. Export the completed assessment and audit record, then retain them according to your healthcare organization’s policy and 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.